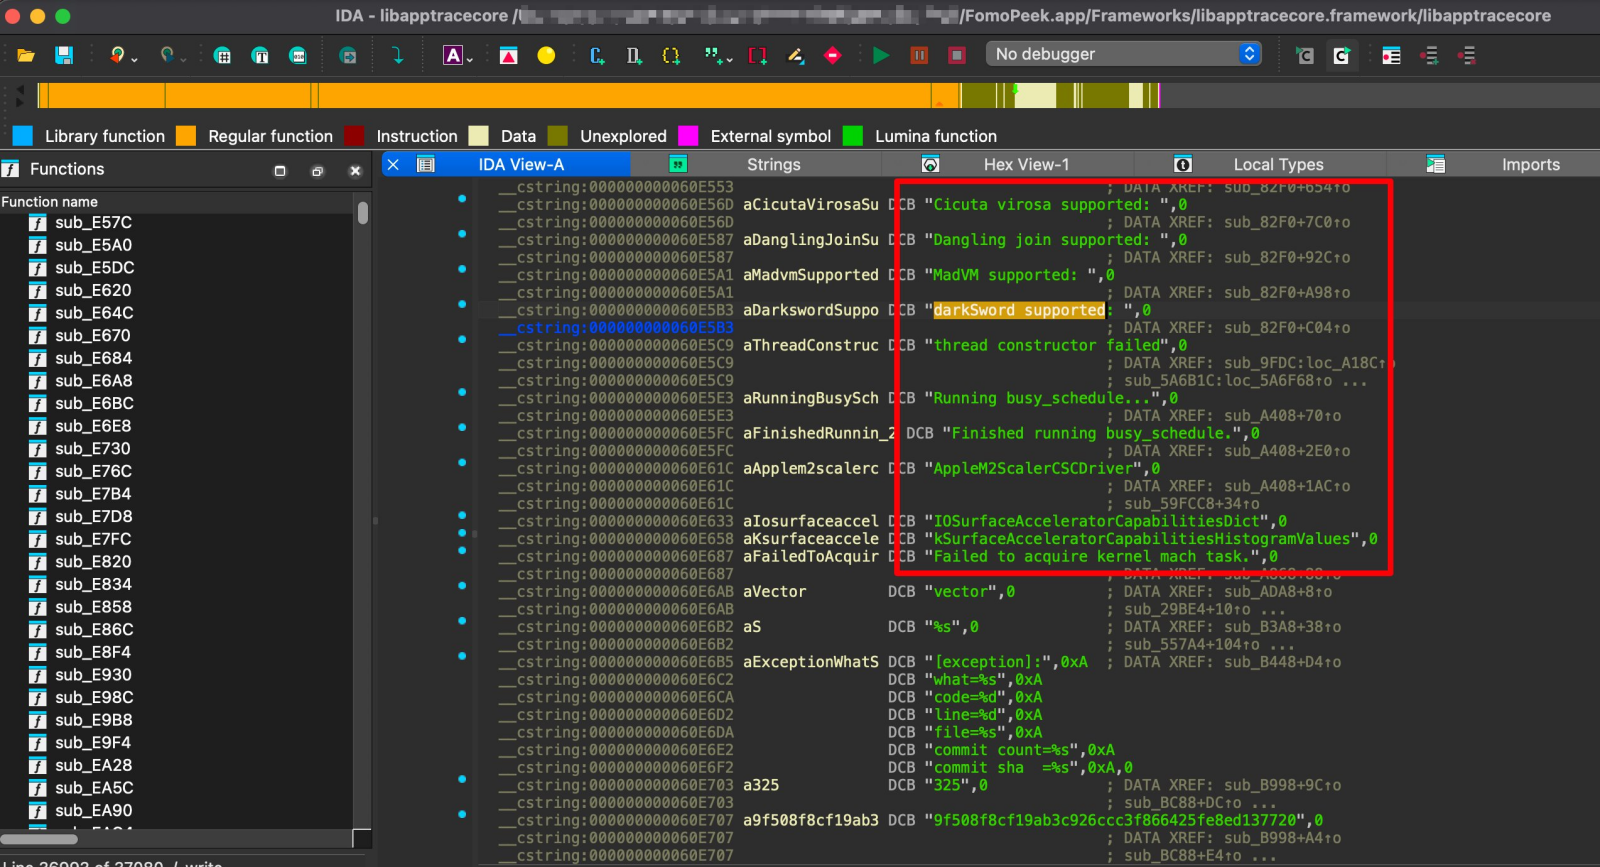
SLOWMIST says it has received multiple reports of cryptocurrency being stolen from users who had installed, or previously installed, the FomoPeek iOS application. FomoPeek is presented as an on-chain activity tracker rather than a cryptocurrency wallet, but the security firm found two unrelated functional modules inside it. One was an iOS kernel-level exploit framework that could select attacks based on the device model and iOS version.
If successful, it could escape the app sandbox, access and decrypt Keychain data, read files belonging to other applications, upload stolen information to attacker-controlled servers and receive remote commands.
The exposed information could include cryptocurrency private keys, mnemonic or seed phrases, login credentials, chat records and other files. SlowMist’s account says affected wallets were emptied and that recovering the assets is difficult. The article does not provide a confirmed number of victims or a total loss. FomoPeek reportedly used cryptocurrency influencers to recruit users, offering new registrants 7 USDT through referral codes, while influencers may have received larger rewards.
The framework is described as targeting iOS 12.0 to 18.7 and iOS 26.0 to 26.1, exploiting flaws Apple has already fixed. The report says the activity most likely involves the DarkSword exploit series, which Google reported in March 2026, although this attribution is presented as an assessment rather than a confirmed finding. Users running the latest iOS version should have the relevant flaws patched. SlowMist’s practical advice is to keep iOS updated, enable automatic updates, avoid applications of unknown origin and do not open unfamiliar websites.