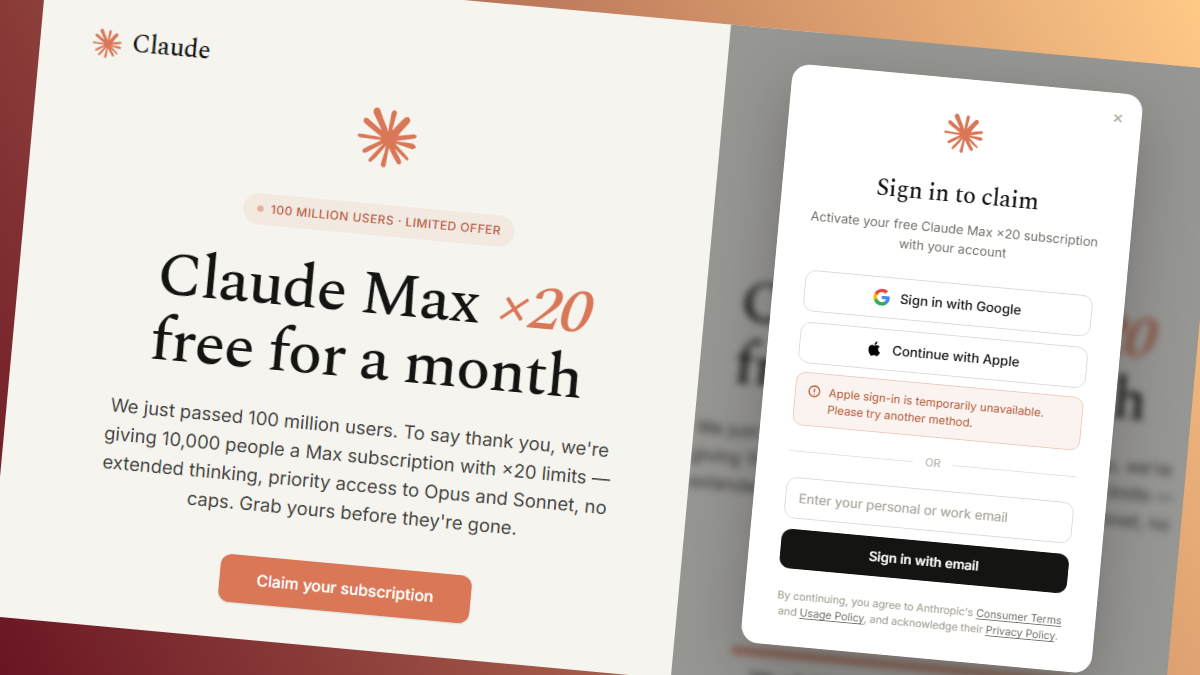
MALWAREBYTES says it has uncovered a phishing campaign offering fake one-month Claude Max subscriptions in exchange for a Google account sign-in. The page claims Anthropic is celebrating reaching 100 million users by giving away 10,000 subscriptions, and uses Anthropic branding, fabricated reviews and a countdown showing fewer than 750 places remaining. Researchers found that the counter is generated in the visitor’s browser and resets on reload, making the apparent scarcity artificial.
The page does not request payment details or install malware, instead targeting Google credentials, which could expose email, documents and password-reset messages, as well as Claude accounts linked to Google sign-in.
The campaign uses a “browser-in-the-browser” phishing technique. Clicking the Google option creates a fake, draggable sign-in window inside the existing webpage, complete with a fraudulent address bar, padlock and Google URL. A human-verification screen appears before the credential stage, potentially helping evade automated analysis. The real browser’s address bar continues to display the phishing domain.
Malwarebytes says the feature is loaded through a single line of code from an external service, whose Russian-language comments suggest it is a maintained, reusable widget rather than campaign-specific code. Users who entered credentials should change their password through Google’s genuine website, sign out of other sessions, and review connected applications and unfamiliar devices.
The researchers recommend checking the actual browser address bar, testing whether a login window can move beyond the webpage, and relying on a password manager’s autofill behaviour.