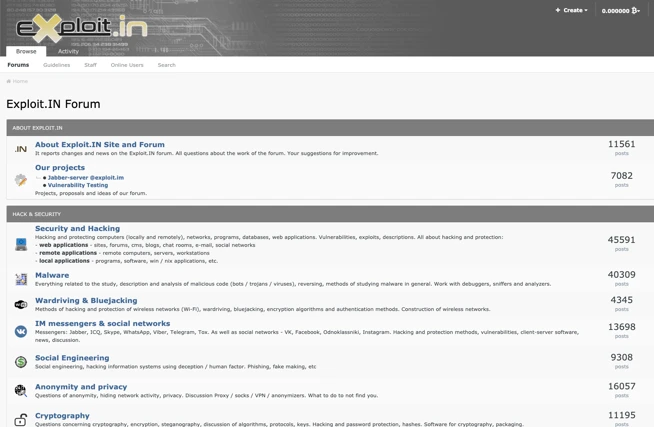
A database covering Exploit.in’s first three years, from February 2005 to May 2008, offers an insight into the origins of practices now associated with ransomware operations. Analysed by Ransomnews researcher Dancho Danchev, the dump contains 9,647 registered members, 13,925 threads and 80,891 posts. Its sections combined cybercrime activity, including malware, spam, carding, vulnerability testing and the sale of shells and credit cards, with everyday discussions about cars, phones, games and humour.
The analysis found that 5,843 accounts, or 60.6%, never posted, while a further 15% posted only once. Just 82 accounts made more than 200 posts, and the top 1% produced 52.6% of all content. Danchev therefore estimates that roughly 90 users were genuinely active, with thousands mainly reading. Activity peaked at 10pm Moscow time, and weekends were about 8% quieter than weekdays, suggesting an informal community rather than a professional operation working shifts.
The researcher also identified 205 distinctive handles appearing in both the early database and private message archives from five later forums, including XSS, RAMP and BreachForums. Twenty-six had made at least 20 Exploit.in posts, while 13 had made more than 100. Danchev stresses that a matching handle does not prove the same person, and has not published the identities because the dump includes email addresses, IP addresses and password hashes.
The report argues that early reputation lists, private sections and access trading evolved into modern escrow services, affiliate vetting and initial-access markets within ransomware-as-a-service operations.