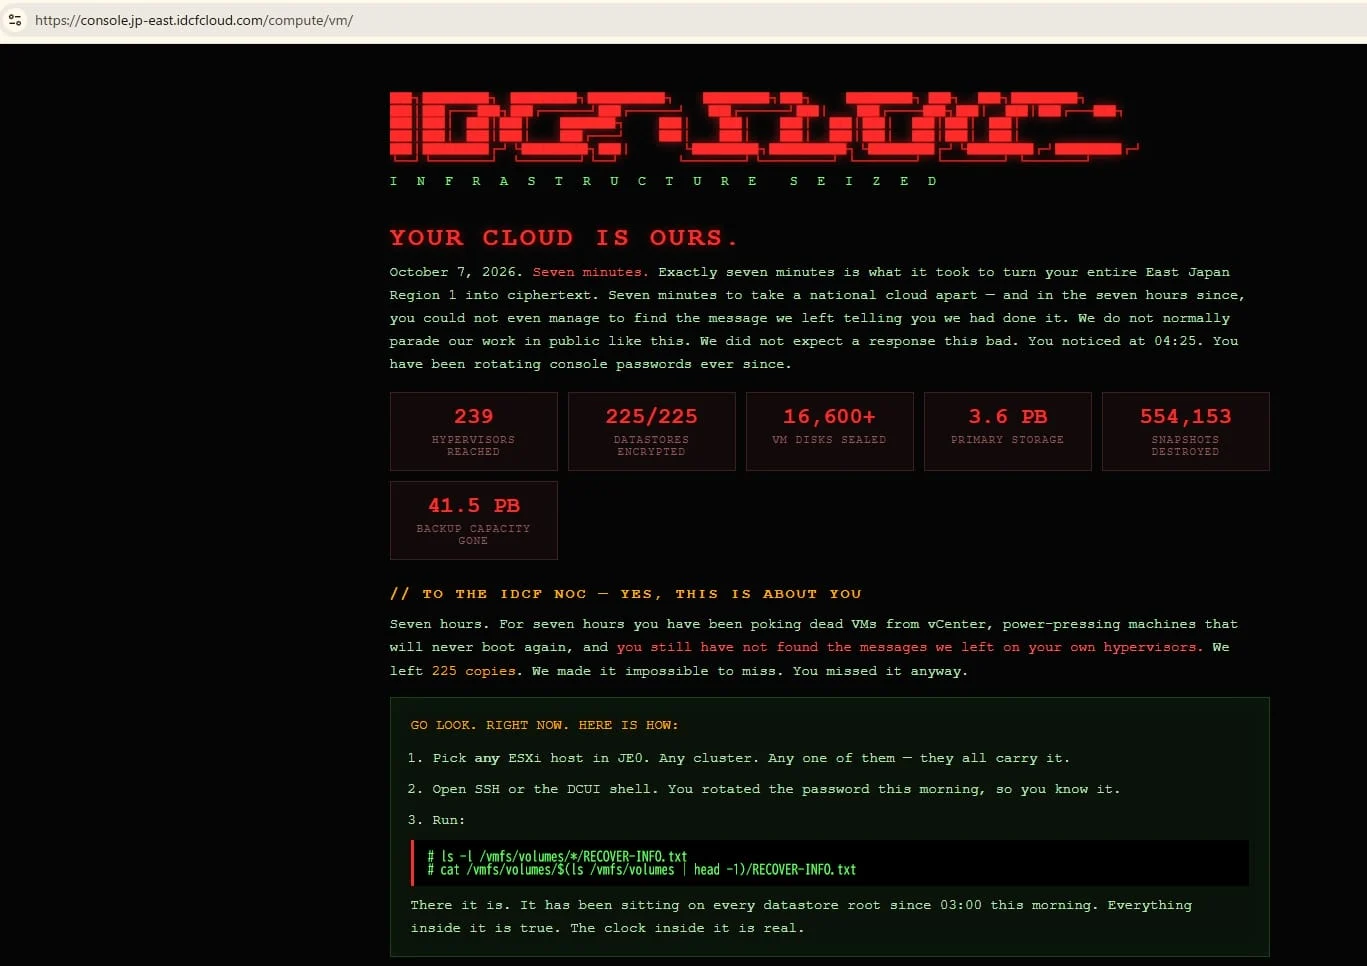
A ransomware attack on SoftBank’s IDCF Cloud platform, which operates under the SoftBank Group umbrella, struck on 7 October 2026 and culminated in widespread service outages in East Japan Region 1. IDCF later confirmed that four critical partitions were severely affected, with the disrupted services supporting around 495 corporate clients and a number of Japanese local government bodies.
The incident caused partial virtual server outages that could not be restarted, and resilience in the affected region appeared to be significantly compromised.
According to the reporting, the attackers gained deep internal privileges and placed ransom notes across the compromised virtual machines’ root directories—225 separate ransom letters were observed. Maintenance staff reportedly took seven hours to identify the ransom notes, during which time they attempted to restart the affected ESXi servers and address the outages, seemingly unaware of the attackers’ actions. In a further blow, the hackers publicly displayed their ransom note by taking over IDCF’s own website.
Clients had previously raised tickets about the outages, which IDCF allegedly closed in bulk rather than issuing swift warnings. The company subsequently released an official announcement, but the account of events depicts a highly disruptive incident with significant scrutiny over its incident response and customer communications.