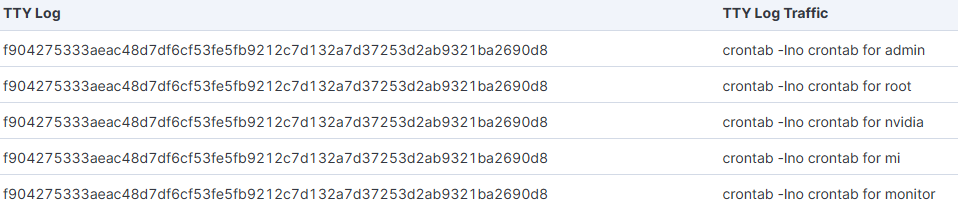
A SANS ISC diary entry reports on an experiment in which Guy Bruneau created a script to parse and send TTY logs collected from attackers or bots that log in to a DShield sensor. The logs are then forwarded daily to the DShield SIEM for correlation with the broader data set. The post provides a concrete ES|QL query that summarises contab commands associated with a specific TTYLog hash over a 90‑day window, illustrating how such activity can be tracked across multiple actors.
The author details several outputs derived from the data: a decoded set of contab commands tied to a transaction[.]id (f904275333aeac48d7df6cf53fe5fb9212c7d132a7d37253d2ab9321ba2690d8) and the fact that this hash was observed across more than 3130 different actors (IP addresses). Three illustrative visuals are referenced, including a TTYLogs decoded image and two examples of event hash decoding sent to the DShield SIEM for analysis. The reported top ten indicators list a mix of IPs and ASNs, showing wide geographic and network diversity among the observed actors.
Overall, the piece demonstrates how TTY log data, when correlated with SIEM tooling, can reveal cross‑actor patterns in compromised systems. It presents evidence in the form of a specific transaction ID, cross‑referenced hashes, and a public‑facing list of source IPs, while clearly framing the work as an observational exercise rather than a report of active exploitation.