SECURITY researchers have reported a critical vulnerability in KGUARD digital video recorder firmware, tracked as CVE-2026-87827 and rated 10.0 under CVSSv4. The flaw allows unauthenticated attackers to execute arbitrary system commands remotely, potentially gaining complete control of an affected DVR. Netlab 360 identified the issue while tracking botnet activity and said the vulnerable service listens on all network interfaces without requiring authentication. The precise port has not been disclosed to reduce further abuse.
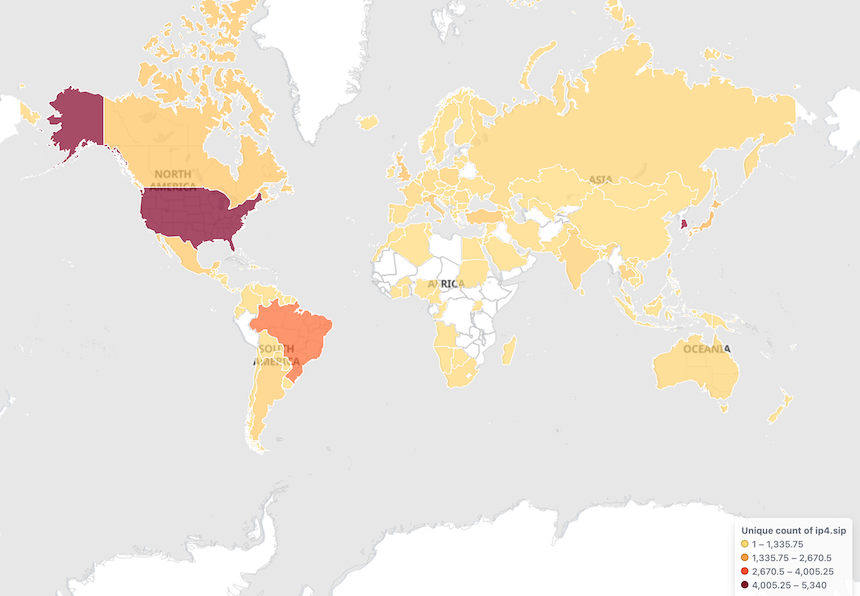
The report says the Mirai_ptea (Rimasuta) and Mirai_aurora botnets have already weaponised the vulnerability to spread malware and conduct later distributed denial-of-service attacks. Some RapperBot versions also reportedly incorporated the exploit, with further abuse observed in 2026. This conflicts with the article’s separate “no confirmed exploitation yet” status field; the detailed account explicitly describes exploitation in the wild. At least 3,000 exposed devices were estimated to remain online.
Affected hardware includes various D1004NR, D1008NR, D1016NR, D1104, D1108NR, D1116NR and D99xx models running firmware dating from 2016. Firmware released after 2017 reportedly mitigates the problem by binding the service to 127.0.0.1. Users should update where possible, remove unsupported DVRs from direct internet exposure, block inbound management access with a firewall, segment them from critical systems and monitor for unusual outbound traffic.