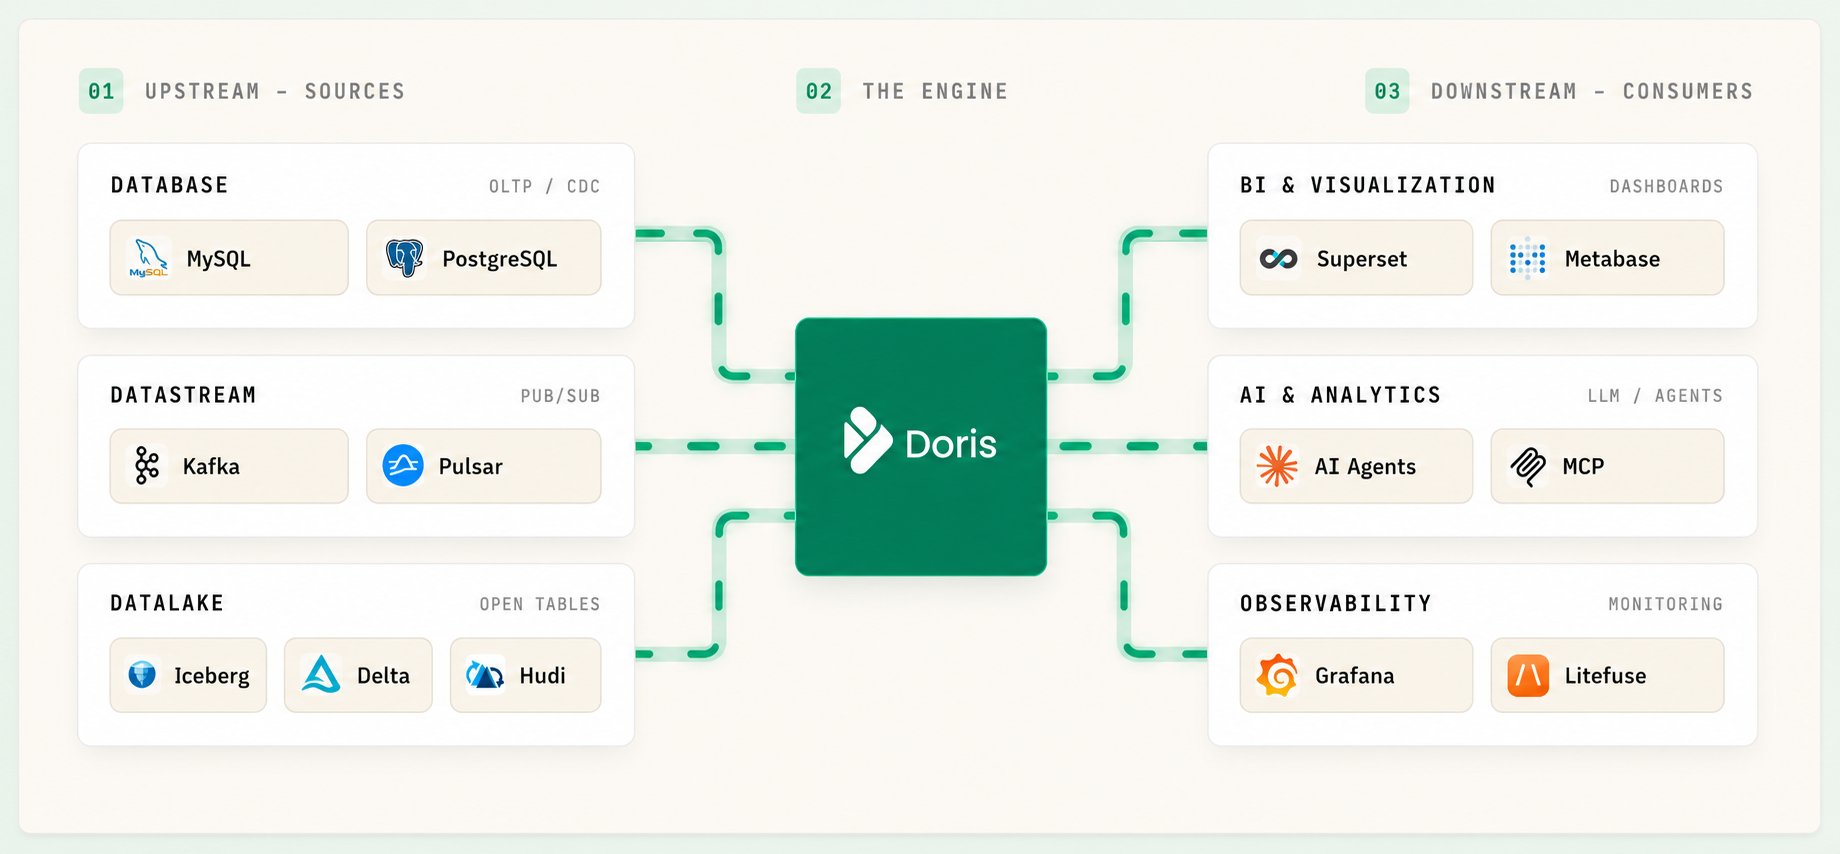
THE Apache Software Foundation has patched two vulnerabilities in Apache Doris, a real-time analytics database. CVE-2026-31377 is rated 7.5 (High) and affects the Frontend metadata service. An authentication weakness allows an unauthenticated attacker to bypass access controls and retrieve internal cluster configuration details because the service trusts client-supplied node information without adequately authenticating the requester. It affects Doris versions 2.0.0 through 4.0.7 and 4.1.0 through 4.1.3; versions 1.2.x and earlier are not affected.
CVE-2026-96443, rated 6.5, involves insufficient validation of JDBC driver URLs. A user who already has privileges can provide a crafted database connection string, potentially resulting in remote code execution on the Frontend node. It affects versions 2.0.5 through 4.1.3. The report says both issues were responsibly disclosed, with no confirmed exploitation or publicly available proof-of-concept code. Apache resolved the flaws in Doris 4.0.8 and 4.1.4. Administrators should upgrade to one of those versions and restrict network access to internal Frontend service ports.