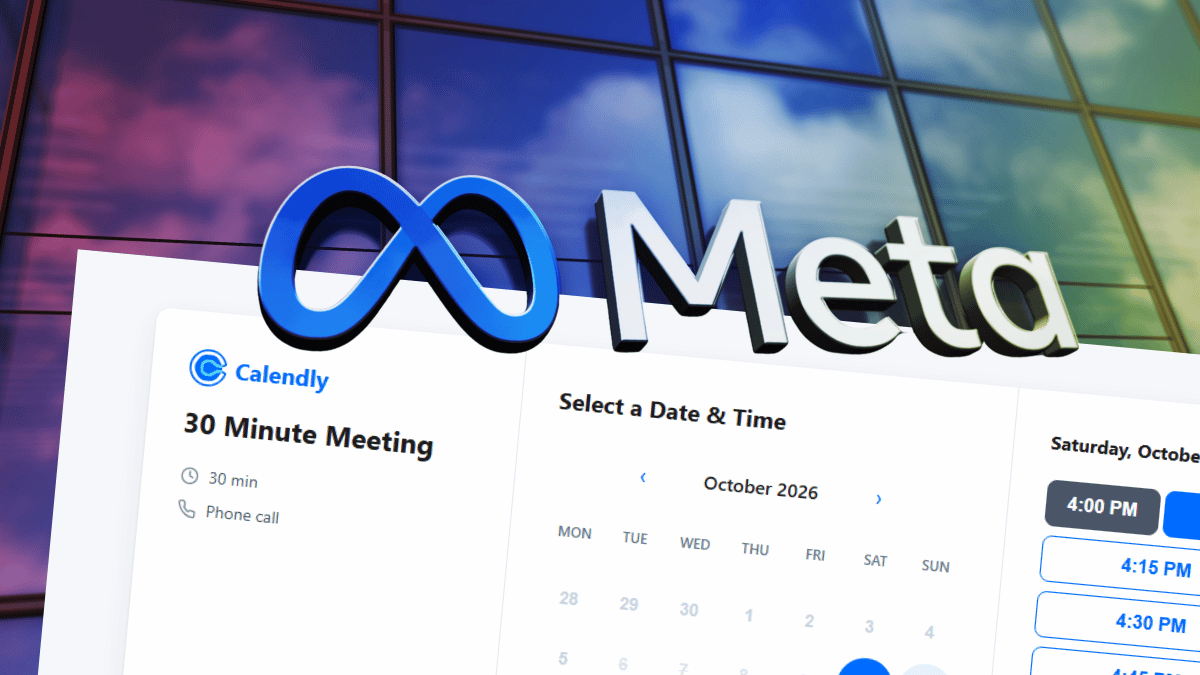
MALWAREBYTES reports a wave of fake Calendly interview scheduling pages purporting to be for “Meta Careers” that redirect victims to steal Facebook and Google logins. The deceptive pages lure users into booking a 30-minute phone interview, entering name, email and phone number, and then passing what looks like a CAPTCHA. The pages then present a Facebook login window embedded within the page, followed by requests for a Facebook 2FA code and, later, a Google login.
The attackers collect credentials and security codes in real time and the pages claim to send a calendar invitation, all while not being affiliated with Meta, Calendly or Google. The campaign’s aim is clear: capture access to compromised accounts and weaponise them for further exploitation.
Evidence within the campaign points to a reusable phishing kit. The page code includes a version string (0.8.0) and campaign keys, with the attack traffic hosted via AWS API Gateway in ap-southeast-1 (Singapore). Indicators of compromise include a set of generic “join” domains such as joinconnect, joinhire, joinquest and jointheteam across .cfd, .info and .works, none of which reference Calendly or Meta.
The collection flow mirrors legitimate authentication steps, enabling attackers to seize Facebook login codes (and potentially Google prompts or MFA codes) before confirming the manipulation to the user. Practical response emphasises verifying the recruitment domain directly, never entering passwords on embedded login prompts, and securing affected accounts promptly.
Malwarebytes Browser Guard and Scam Guard are highlighted as preventive measures, with guidance to audit recovery options and look for unusual domain or session activity on both Facebook and Google accounts.