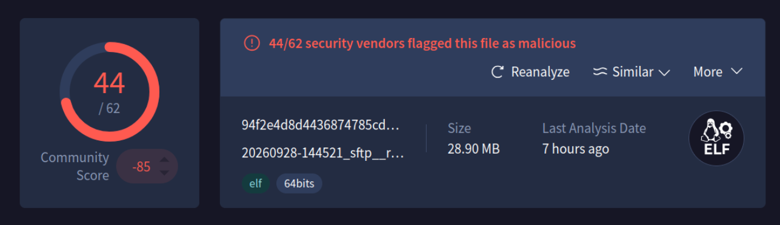
A guest diary from Zachary Norwood describes the Panchan worm, a long-running crypto mining botnet that propagates via multiple methods and remains active despite the passage of time. The entry notes that the worm was obtained from the DShield honeypot after a malicious binary was uploaded and run, and identifies Panchan as a Golang-written, peer-to-peer botnet first detected in 2022.
The author emphasises that the threat targets insecure, internet-facing systems and can undermine a network through SSH access, often leveraging a rootkit to maintain access.
The diary details how Panchan operates, including its use of a command-and-control channel and a number of functions demonstrated in captured binaries. It highlights a network analysis workflow using FakeNet-NG and Wireshark to observe the worm’s external communications, including a Discord-based C2 channel. Evidence of compromise is described as including multiple failed SSH authentication attempts, unusual resource usage, and hidden directories in user home folders or in /tmp with high-entropy names.
Practical mitigations suggested in the piece focus on deny-by-default network posture, egress and ingress filtering, robust firewalling, and the deployment of e.g. SIEMs, logging, and intrusion prevention. The diary also advocates for strong SSH controls—disabling password login, using key-based authentication, and employing short-lived credentials via systems such as HashiCorp Vault—and for limiting access to SSH via ACLs or a jump box, alongside enabling Fail2Ban and MFA where appropriate.