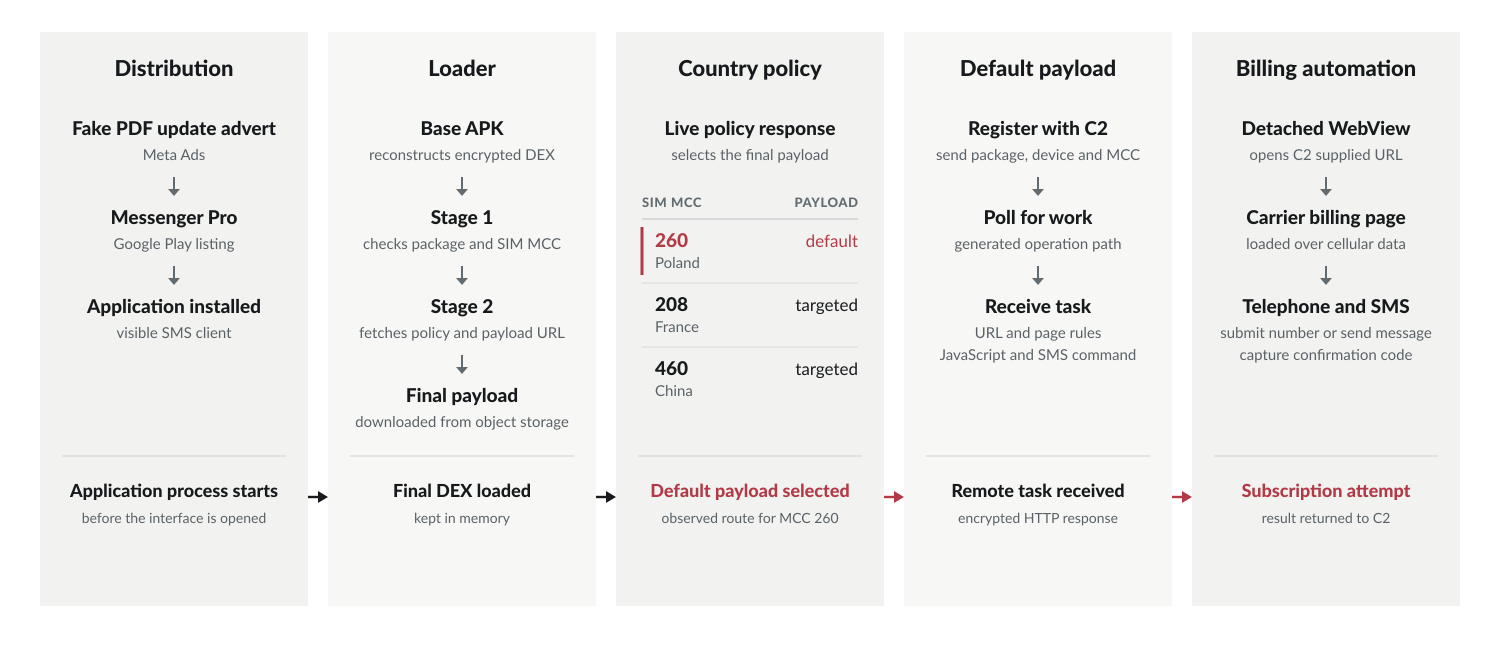
CERT Polska has uncovered a coordinated Android toll-fraud campaign that used deceptive Meta advertisements to direct victims to Google Play applications posing as SMS clients and device-cleaning tools. Investigators tracked 1,235 advertisements across 74 Meta account profiles; 852 promoted 17 applications linked to the operation. Some adverts falsely claimed that a PDF viewer had expired, but redirected users to an unrelated SMS app called Messenger Pro.
The campaign targeted users in Poland, France, China and 12 other countries. Google removed the identified apps and Meta removed the associated advertising profiles, although previously installed apps remain a risk until manually removed.
The malware used a four-stage, modular infection process. An exported Bluetooth Message Access Profile provider could start the app after installation, while encrypted code was decrypted in memory, downloaded from Alibaba Cloud Object Storage and loaded through dynamic class loaders. The malware checked the device’s mobile country code and received routing instructions from a remote policy server.
By becoming the default SMS application, Messenger Pro obtained permissions to read, receive and send messages, which it abused to authorise paid services. In Poland, it sent premium SMS messages to numbers including 92505, 92512 and 92513, each costing 30.75 PLN. It also used hidden WebView sessions and intercepted verification PINs for recurring direct-carrier subscriptions, including one costing 17 PLN every seven days. CERT Polska said it could not attribute the operation. Users should remove suspicious apps, review default SMS settings and mobile bills, and ask their provider to block premium SMS and carrier billing.