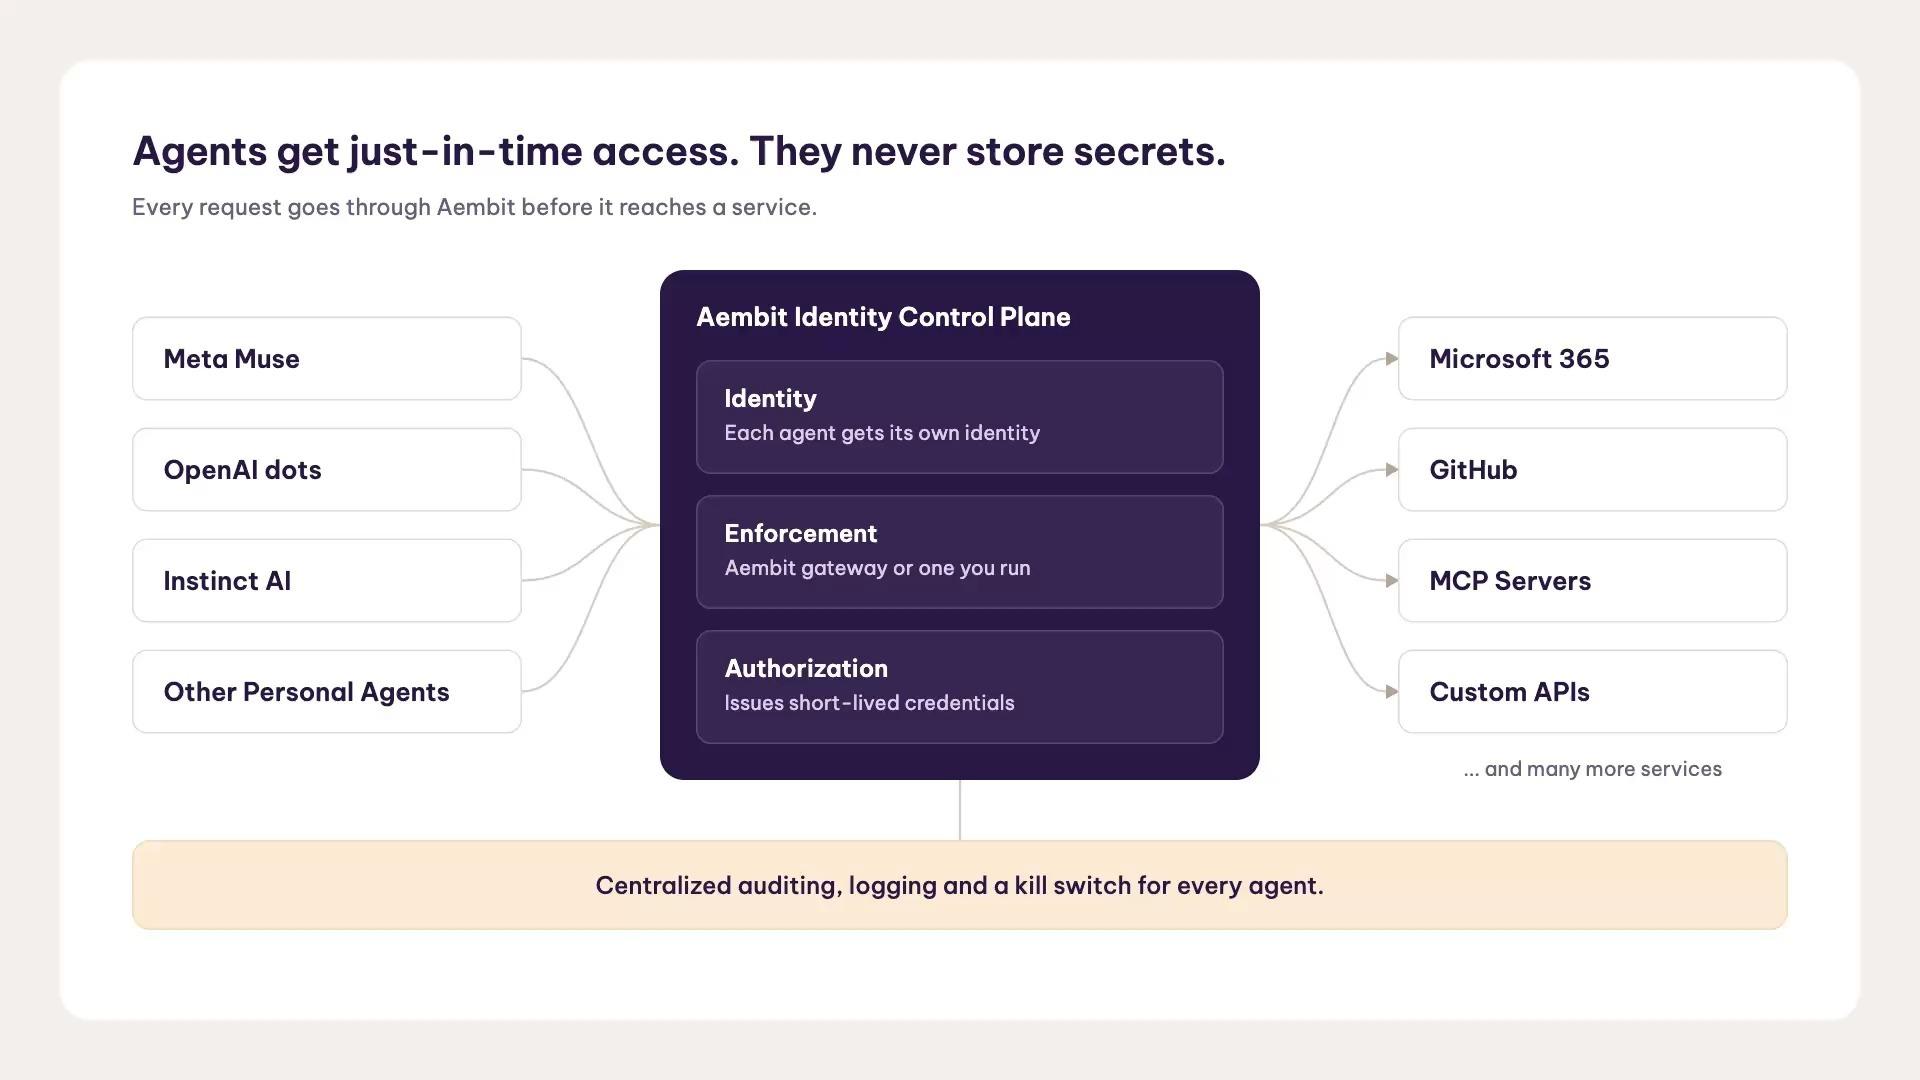
AEMBIT , the identity control plane for AI agents, has announced new features that extend enterprise access controls to personal AI agents such as Meta Muse and OpenAI Dots. The rollout, available immediately to existing customers at no extra cost, aims to curb the heightened risk that personal agents pose as they gain access to email, cloud apps, code repositories, and other corporate services via employee credentials.
The concern highlighted is that credentials may sit inside the personal agent platform, outside the security team’s direct oversight, making sensitive data exposure or unauthorised changes harder to detect.
The approach blends the agent’s own identity with the employee’s, allowing organisations to assess both at access time, issue short‑lived credentials for approved requests, centralise audit logs, and revoke an agent without disabling the employee’s account. Aembit’s model supports policy enforcement across SaaS, developer platforms, and internal services, and can be deployed through the Aembit MCP Identity Gateway or other existing gateways.
Key features include distinct identities for each agent, runtime access evaluation, short-lived credentials, centralised audit trails, and the ability to revoke an individual agent’s access independently. The company notes support already extended to Meta Muse and security for agents and AI platforms including Microsoft Copilot Studio, Claude, ChatGPT, Gemini, and other LLM‑based workflows.
CEO David Goldschlag emphasised that this addresses a fundamental access problem by “giving the agent its own identity, controlling what it can reach, and shutting it off without taking the employee offline.”