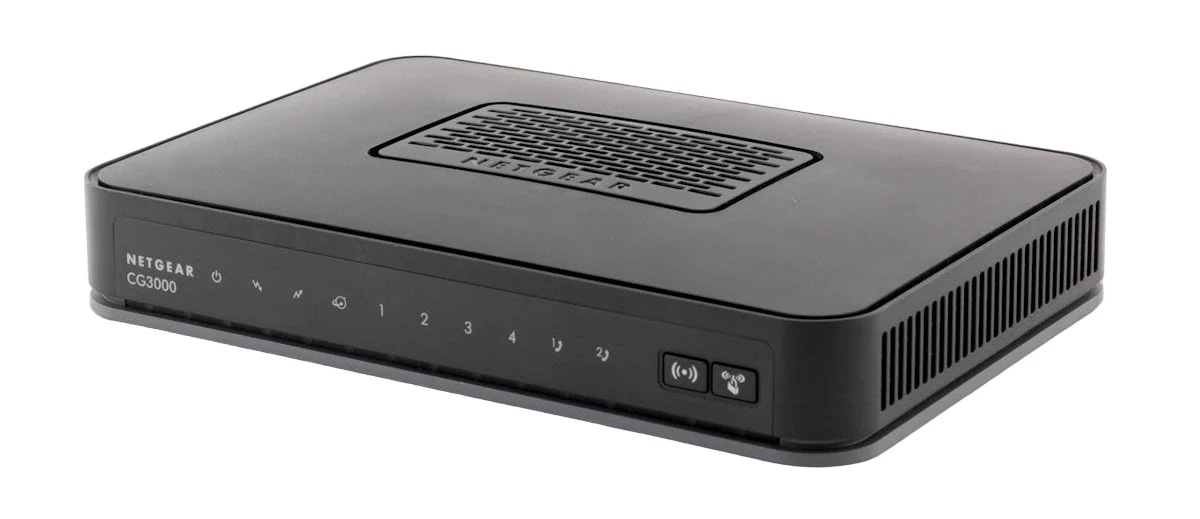
A Broadcom Wi‑Fi vulnerability dating back to 2010 allows an attacker within Wi‑Fi range to execute code on vulnerable routers without any authentication or knowledge of the network password. The flaw resides in Broadcom’s proprietary 802.11 implementation and affects the WPS EAP reassembly code that handles part of the wireless setup process.
Kaiser’s demonstrations show unauthenticated remote code execution and, in at least one case, extraction of the Wi‑Fi PSK from the router’s memory over the wireless channel, followed by using that password to access the network. The bug has been present in Broadcom’s SDK since 2010, with an incomplete patch released in 2018 and Broadcom later advising migration to a different software stack rather than delivering a complete patch for its own code.
The vulnerability affects devices across eCos‑based platforms (for BCM3380, BCM3383, BCM33834) and, on Linux‑based platforms (BCM3390, BCM65xx, BCM68xx), the outcome depends on OEM actions. Kaiser demonstrated working exploits against two devices: Orange Belgium ASKEY TCG3000 and Proximus Sagemcom F@st/BBOX3V+ (also known as Sagemcom), both allowing code execution without authentication; one demo opened a reverse shell over Wi‑Fi frames.
CERT/CC opened a case but closed it the same day after confirming Broadcom could assign CVEs itself and had no intention to do so. Belgium’s market data estimate roughly 1.5 million potentially exposed gateways, with broader implications for devices worldwide that use these chipsets. Kaiser notes AI‑assisted analysis helped reach these findings rapidly, underscoring both defender and attacker capabilities in mapping and exploiting such long‑standing flaws.