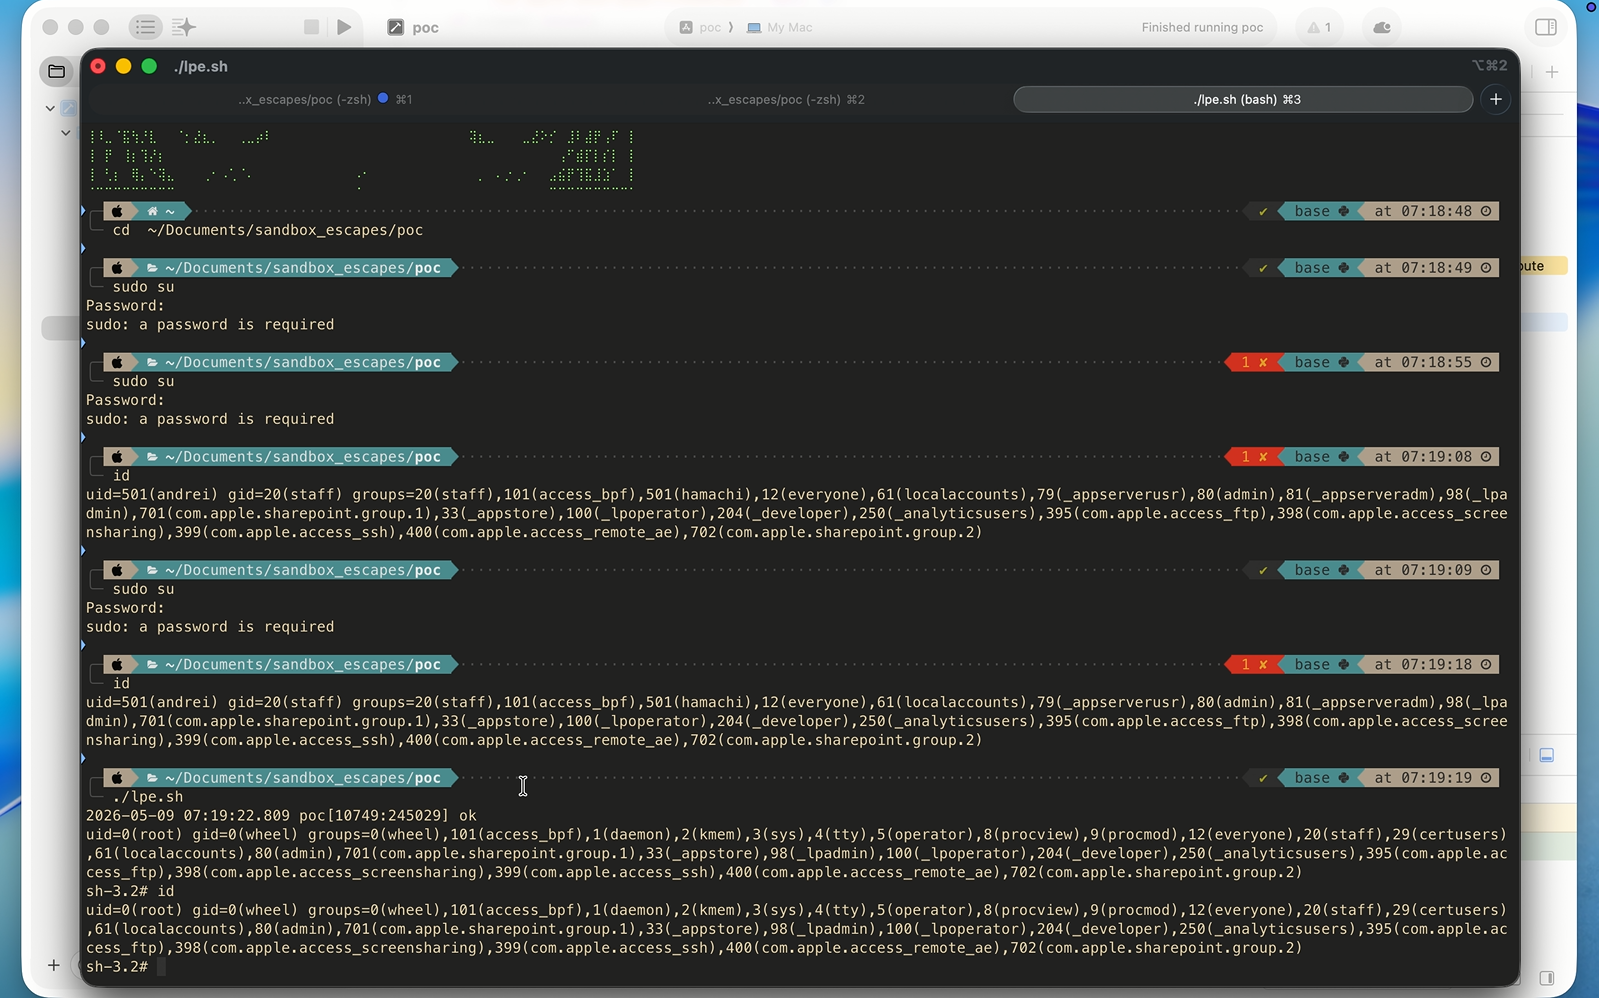
SECURITY researcher Ilya Andr of PT MAZE has disclosed details and working proof-of-concept code for CVE-2026-43783, a high-severity local privilege-escalation vulnerability in macOS’s DesktopServicesHelper daemon. The flaw is rated CVSS 7.8 and affects macOS versions below 26.6, although the article gives conflicting patch guidance elsewhere, referring to both 26.5 and 26.6. No exploitation has been confirmed in the wild, but the PoC is publicly available on GitHub.
DesktopServicesHelper processes Finder requests for administrative file operations. According to the report, its RepairPermissionsForCloudItems routine does not properly check entitlements or restrict supplied paths to iCloud directories. A local, potentially sandboxed application can therefore make the daemon recursively change ownership of arbitrary files and directories using `fchown`.
The described attack targets `/private/etc/pam.d`, creates a `sudo_local` configuration containing the `pam_permit` rule, and then uses `sudo` to obtain a root shell.
Apple reportedly addressed the issue by adding a requirement for the `com.apple.private.desktopservices.cloud-repair-perm` entitlement; unauthorised callers are disconnected. Users and administrators should apply the relevant latest macOS update, with the article’s version references verified against Apple’s release documentation before deployment, and prioritise devices running versions below 26.6.