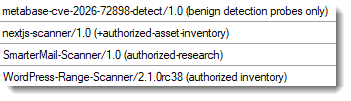
A recent Internet Storm Center diary by Didier Stevens surveys amusing and worrying examples of User Agent Strings seen in honeypot logs. The piece collates a variety of UA strings that attackers send in requests, ranging from so‑called “authorized” scans to elaborate spoofing and disinformation. Stevens notes that many UA strings come from masscan variants, occasionally including coded labels such as “KGB variant,” and that attackers sometimes rotate or swap the entire list of user agents for each request.
He also points to instances where the strings themselves reveal contact details or links to behind‑the‑scenes actors, including a Belarusian email address referenced in a previously discussed diary.
The article also highlights practical observations about how UA strings are constructed and parsed in real traffic. Some requests deliberately embed parsing flaws or legacy payloads, with examples such as Shellshock‑style patterns lingering in UA fields, and even attempts to probe for services that stream GPS correction data via the NTRIP protocol.
Stevens presents evidence as screenshots and cites a public repository of user‑agent strings used to group or separate entries, noting that incomplete sanitisation means odd or misleading strings can appear in actual requests.
The overall takeaway is a reminder that UA strings remain a rich source of noise and misdirection in scanning activity, and defenders should continue to monitor honeypot telemetry for unusual, rotating, or discrediting identifiers while acknowledging that some observed strings may be more about masquerade than genuine client behaviour. Published 4 October 2026.