DARKTRACE has documented a campaign around a Rust-written remote access trojan named CikaBika Bot, which uses Discord as its command-and-control (C2) channel. The infection chain begins with a disk image that masquerades as a business proposal, paired with a malicious Windows shortcut. When opened, a hidden PowerShell process runs in the background while a misleading PDF is displayed.
The shortcut reads the fake PDF as raw data, decrypts and extracts a loader written in Nim, which then loads a Rust DLL and a PowerShell script. The script attempts to copy the DLL into Microsoft Edge’s installation folder and perform a DLL search-order hijack to sideload it, using a registry modification to bypass the UAC prompt. Darktrace notes that the Edge delay-import table is not fully compatible in every case, so the technique may not work on all systems.
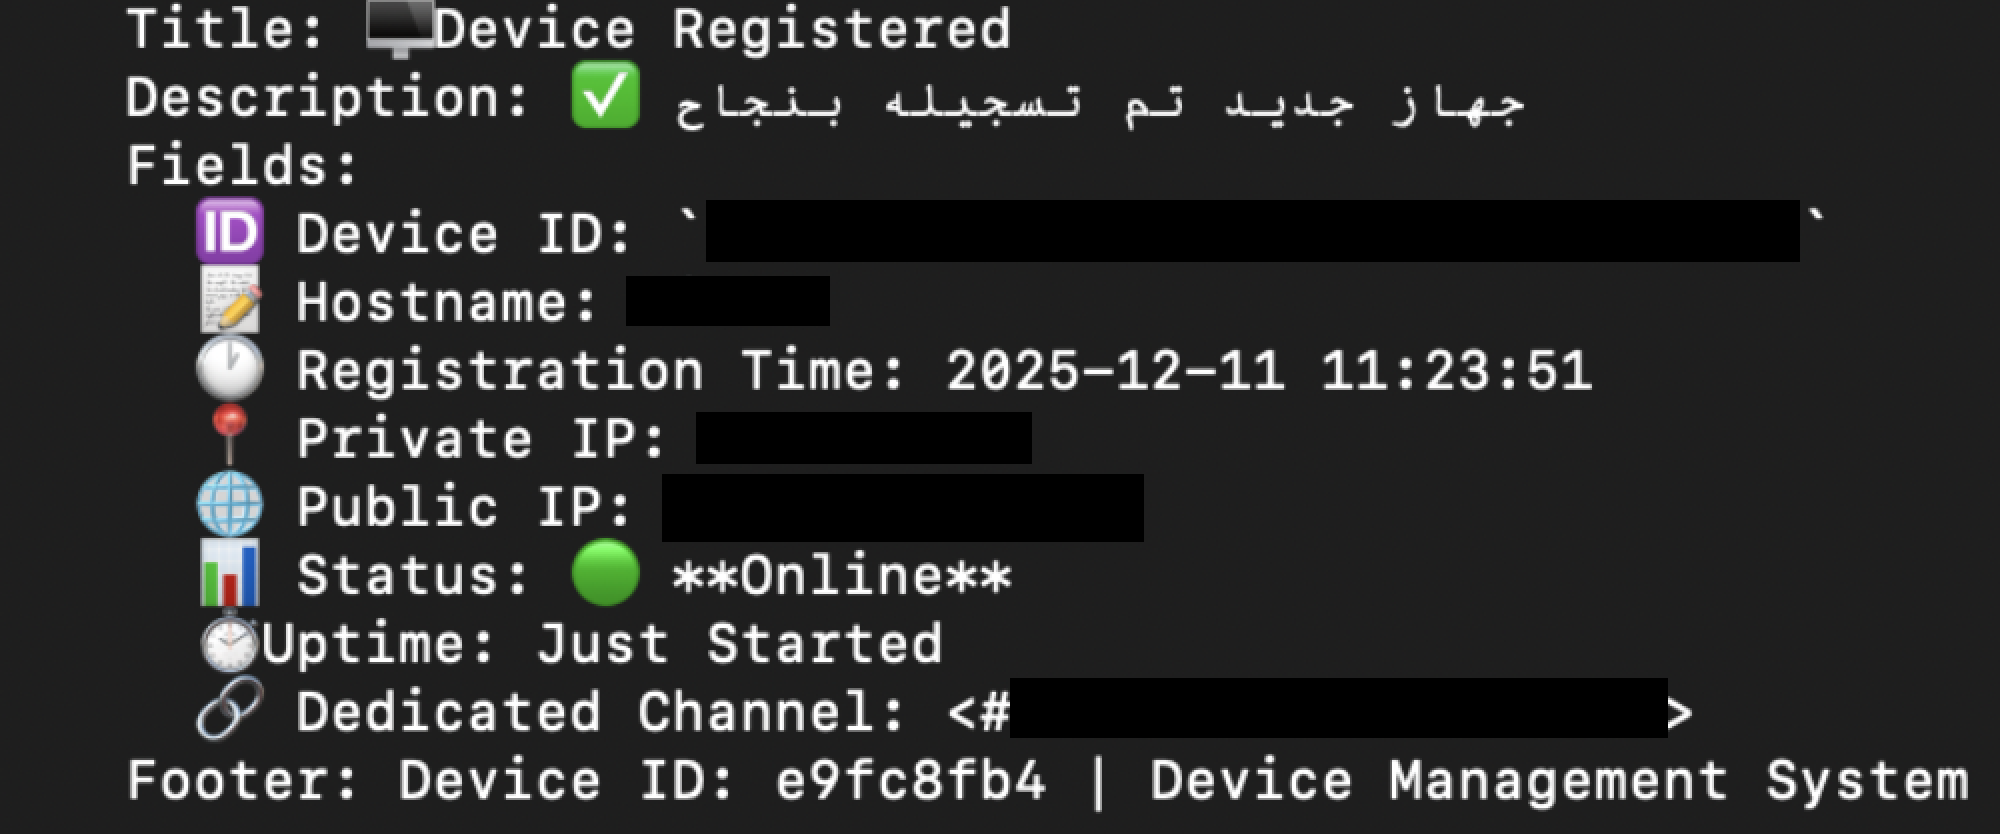
Once installed, the implant registers the infected host with Discord and creates a dedicated channel for that device. It immediately collects host information, runs commands such as tasklist and ipconfig, takes a screenshot, and transmits data back to the operator. The command set includes remote shell access, process listing and termination, and file upload/download, as well as surveillance features like camera access and screen streaming.
The attackers also use Ngrok to transfer exfiltrated data rather than overloading Discord with large data, and can exfiltrate via Ngrok if Discord access is restricted. The report emphasizes how the campaign demonstrates ongoing reliance on social engineering and repurposing legitimate services for malware operations, with Discord capable of acting as a distributed C2 platform for individual victims.