KASPERSKY has reported a malware campaign dubbed MovieReaper that uses compromised torrent content to target people downloading pirated films. The campaign allegedly abuses the itorrents.org repository, meaning malicious files may be distributed through multiple tracker sites. The files are disguised as films with long names such as “the odyssey (2026) [1080p] [webrip] [5.1].exe”, making the executable extension less visible.
Kaspersky says the campaign has affected several hundred victims since August 2026, including government agencies, agricultural companies and IT consultancies across Europe, Asia, Africa and Latin America.
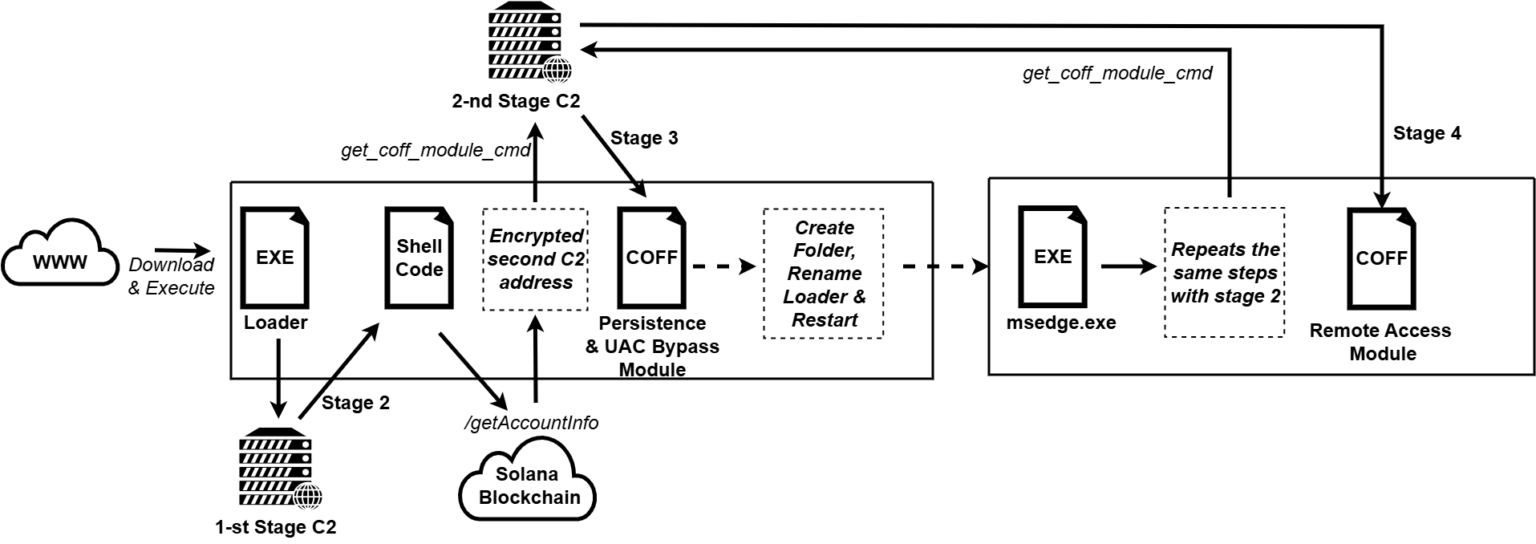
After execution, the loader checks for sandboxes and virtual machines, decrypts its strings and retrieves shellcode disguised as image files over HTTP. The second stage uses data stored in a Solana blockchain account to obtain an encrypted command-and-control address, then communicates with the server over HTTPS with certificate pinning. The malware reportedly bypasses Windows User Account Control and persists while posing as a Microsoft Edge telemetry process.
Its in-memory file-management module supports 21 commands, including reading, uploading, downloading, copying, moving, renaming and deleting files, as well as creating previews before exfiltration. Kaspersky suspects additional modules can be loaded on demand.
The article recommends blocking unauthorised torrent activity and the campaign’s hardcoded initial domain, investigating movie-themed executables and suspicious binaries in the Windows Telemetry folder, and monitoring corporate endpoints for unexpected Solana RPC traffic.