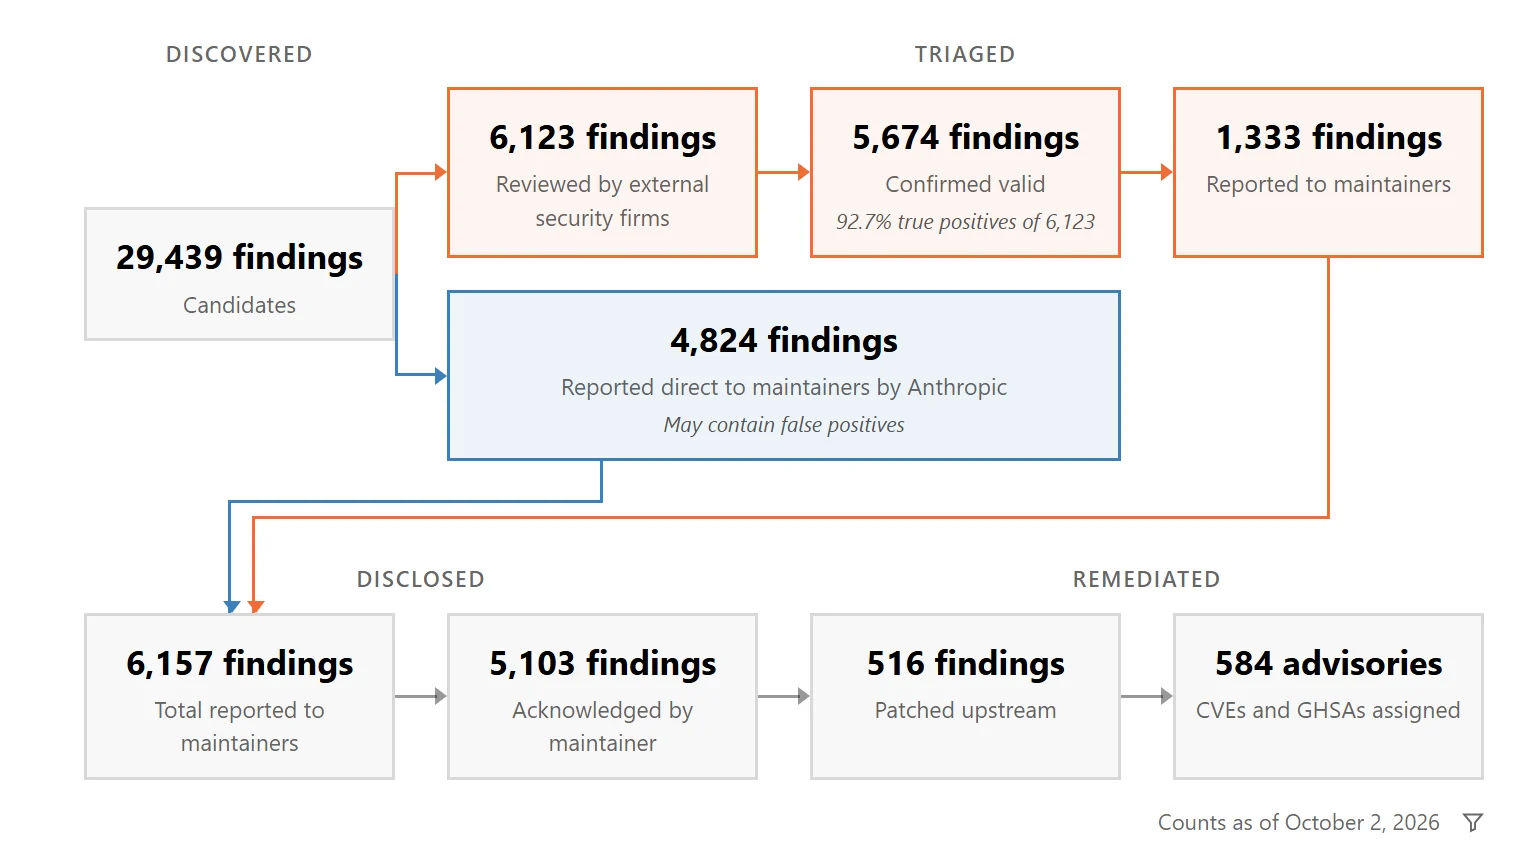
ANTHROPIC has unveiled OSS Scanner, a service aimed at providing eligible open-source projects with complimentary and regular vulnerability scanning. The programme, which uses Anthropic’s Claude Mythos models to review codebases for security flaws, sends a full vulnerability report to project developers whenever issues are found, including potential remediation steps where available.
Participation is voluntary: core maintainers apply via Anthropic’s GitHub repository, and a panel of Anthropic engineers assesses eligibility based on the project’s infrastructure or safety relevance. Approved projects then receive scheduled scans and ongoing reporting, with detailed vulnerability descriptions, reproduction materials, and fixes where possible.
A key feature is that the OSS Scanner operates end-to-end with automated AI generation. Reports, including remediation guidance, are produced without human review or confirmation. Anthropic argues this enables faster, more frequent vulnerability updates for maintainers, though it also notes that AI-generated output may contain errors, misjudge severity, or misinterpret a project’s threat model, so developers should evaluate findings independently.
Early testing involved 97 high- and critical-severity vulnerability reports across 48 projects; 85 reports (88 per cent) met the standards of the coordinated vulnerability disclosure workflow, with 11 genuine issues duplicating known flaws and 1 finding deemed invalid. The article notes that unverified reports remain confidential and outside the 90-day disclosure window, while critical issues in major projects may still follow traditional disclosure practices. 9 October 2026.