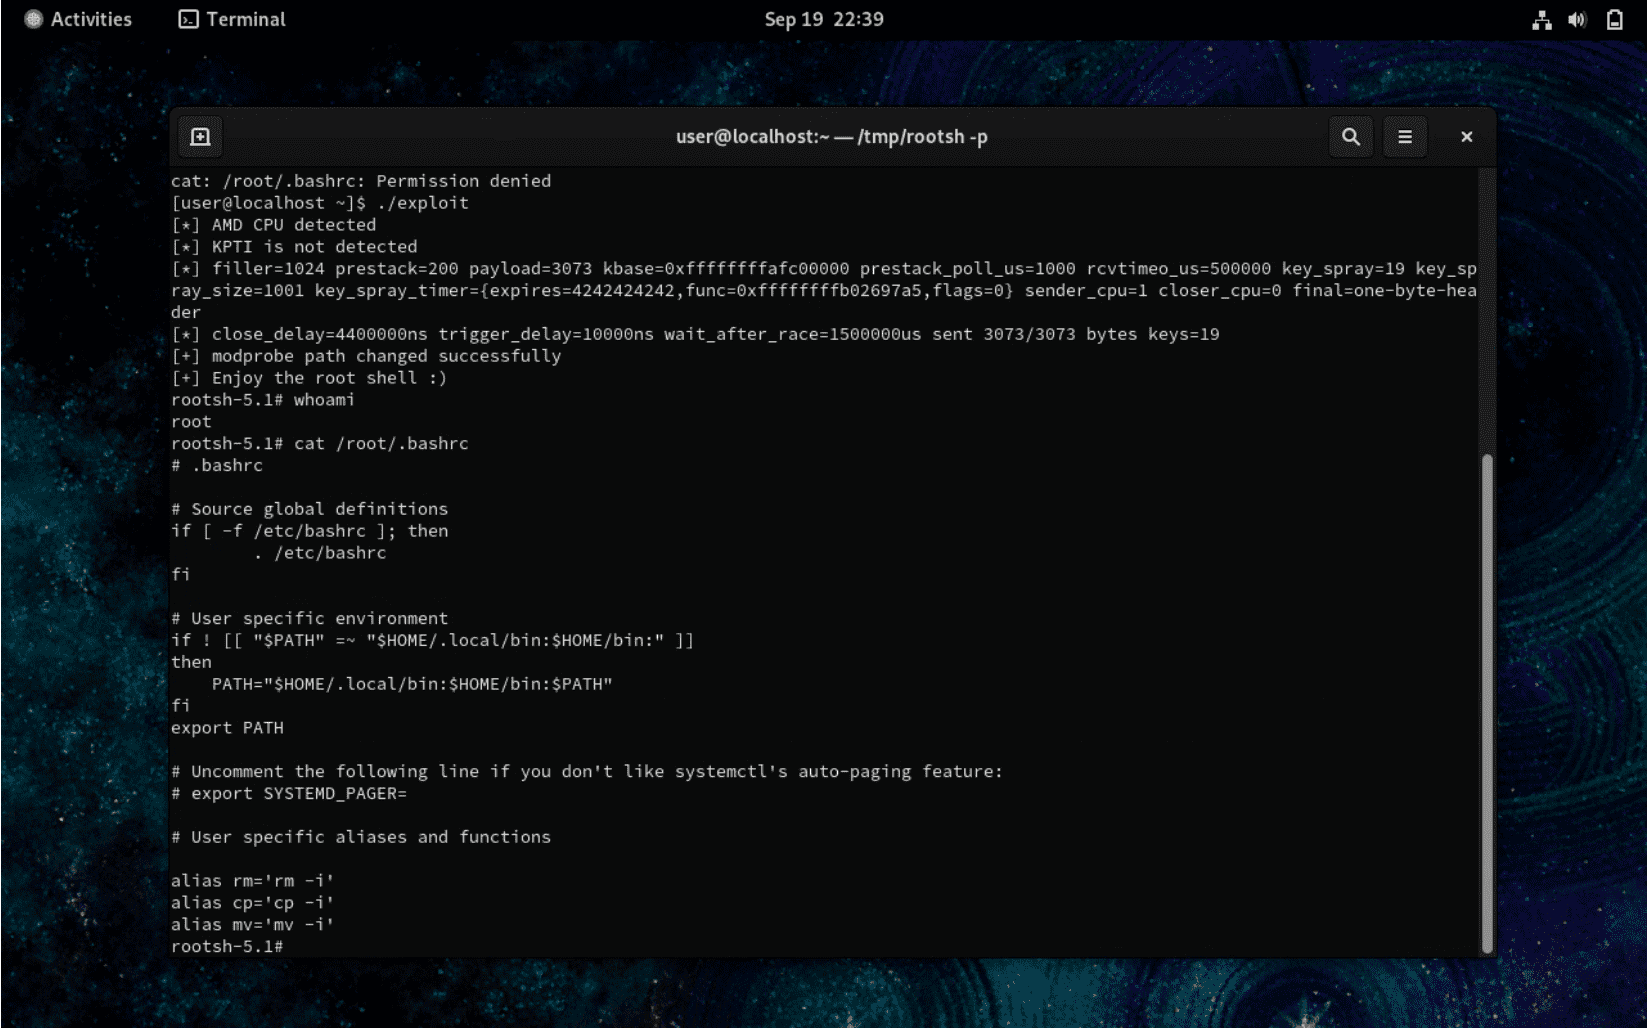
A researcher has published RustyTux, a working proof-of-concept exploit for CVE-2026-23239, a Linux kernel privilege-escalation vulnerability rated High with a CVSS score of 7.8. The flaw affects the espintcp module and involves a race condition during socket teardown in the strparser and espintcp code. An unprivileged local user reportedly needs no Linux capabilities to reach it.
The article says the race was present in standard kernels for CentOS Stream 9 and Ubuntu 26.04 LTS as of September 2026, while the public proof of concept targets CentOS Stream 9 kernel 5.14.0-745.el9. No exploitation in the wild has been confirmed.
RustyTux overlaps an active receive parser with socket closure, causing a message timer to be rearmed after it has been cancelled. This can leave an espintcp context freed while another code path still uses it. The exploit then reclaims the object with attacker-controlled data, uses an x86 prefetch timing side channel to derive the randomised kernel base, and redirects a callback to obtain root access. The technique is timing-sensitive and requires target-specific tuning; a crash-only variant can instead cause an unprivileged kernel denial of service.
The article advises applying the latest distribution kernel updates and rebooting afterwards. The upstream fix replaces unsafe work-cancellation logic in the espintcp close path. Until systems are patched, administrators should restrict local access on shared machines and, where espintcp is unnecessary, block the module from loading. The listed fixes include commit f7ad8b1d0e421c524604d5076b73232093490d5c and seven additional commits.