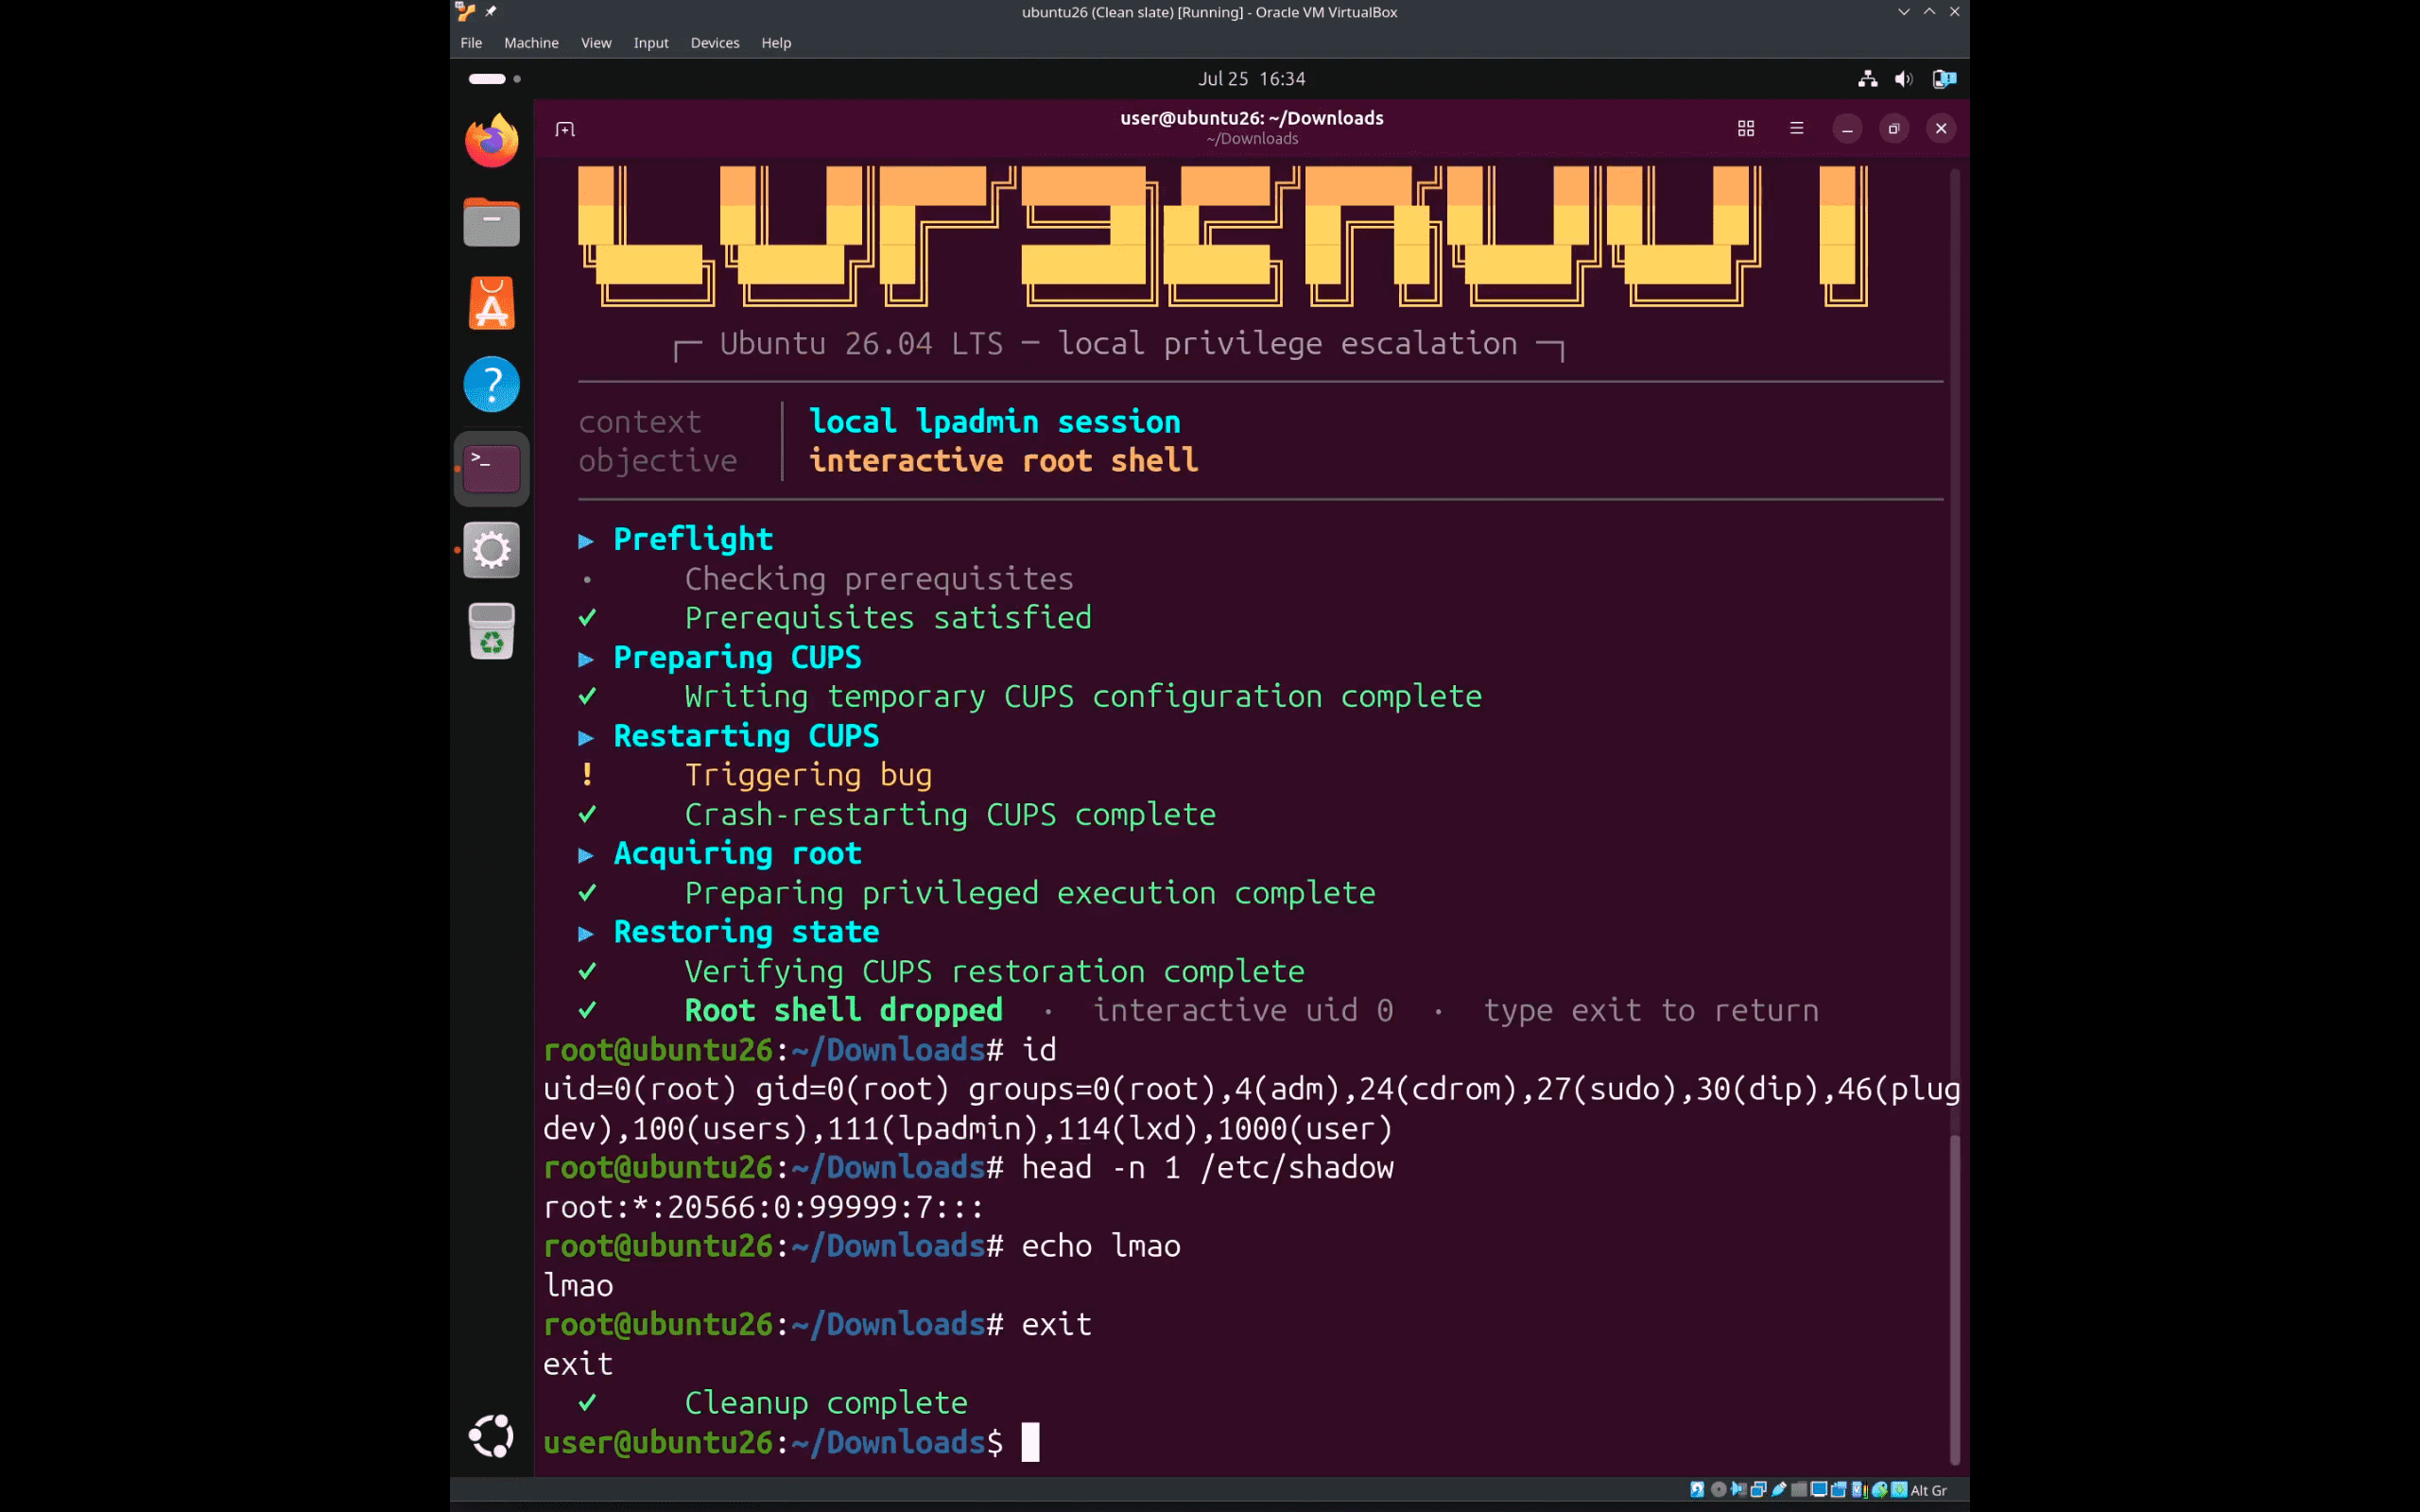
A researcher from V12 security has published cups2root, a proof-of-concept that can escalate a local user in Linux’s `lpadmin` group to root through the Common Unix Printing System (CUPS). The report says the exploit targets Ubuntu systems using systemd, with a local CUPS service and the serial backend enabled, and supports AMD64 and ARM64. CUPS is widely used on Linux desktops and some servers, making systems with unnecessarily broad `lpadmin` membership potentially exposed. However, no CVE or CVSS score has been assigned, and exploitation in the wild has not been confirmed.
The attack abuses the root-running CUPS serial backend to create a raw serial printer whose device URI points to a CUPS configuration file. Crafted print data overwrites the file, redirecting paths such as `ServerBin` to an attacker-controlled directory. A malformed IPP request then crashes the daemon; when systemd restarts it, CUPS executes a replacement helper as root. The PoC uses that access to install a setuid shell before restoring the original files and cleaning up.
There is currently no vendor patch. The article recommends limiting `lpadmin` membership to trusted administrators, disabling the serial backend where it is not needed, and keeping CUPS bound to localhost. Administrators should monitor OpenPrinting for a fixed release and apply it when available.