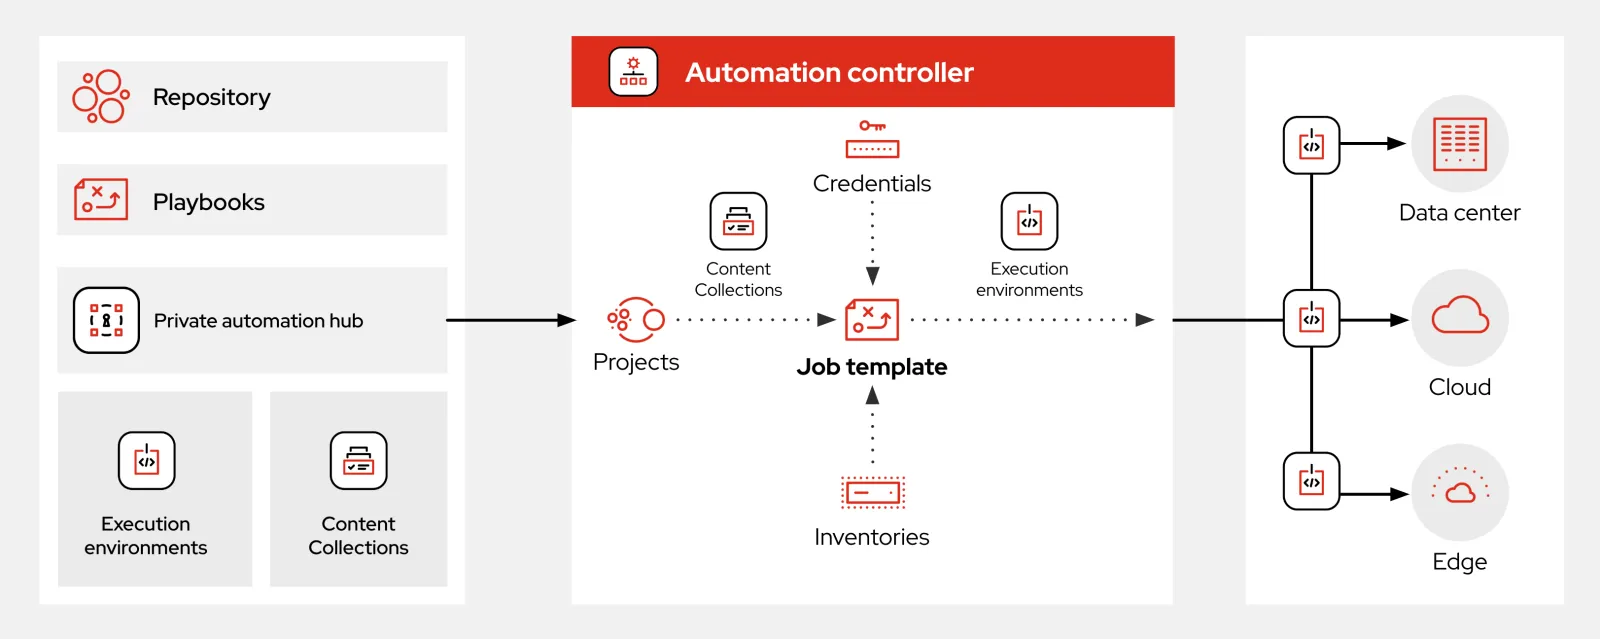
RED Hat has disclosed two critical vulnerabilities in Ansible Automation Platform 2.4 for RHEL 8: CVE-2026-84719, rated 9.9, and CVE-2026-75884, rated 9.1 on CVSSv3. The article says neither flaw has been exploited, and no public proof-of-concept code has been confirmed. CVE-2026-75884 involves incomplete input validation in container-group configuration, allowing an administrator to inject overrides and escalate privileges to OpenShift namespace-level access.
This could expose sensitive information including administrator passwords and database encryption keys. Containerised Podman installations are described as unaffected by this flaw.
CVE-2026-84719 affects the automation-controller subsystem. When a workflow job template is copied, its deep-copy permission sanitiser fails to check authorisation for inherited instance groups. A user could therefore schedule jobs on restricted groups, including the control plane, potentially achieving arbitrary code execution in the control-plane execution context. The affected areas include the AWX controller and automation-controller subsystems, with standard cluster deployments exposed according to the report.
Red Hat has issued fixes, including 0:4.5.36-1.el8ap, 0:4.5.36-1.el9ap, 0:4.6.33-1.el8ap and 0:4.6.33-1.el9ap. Administrators should apply the vendor’s latest security updates.