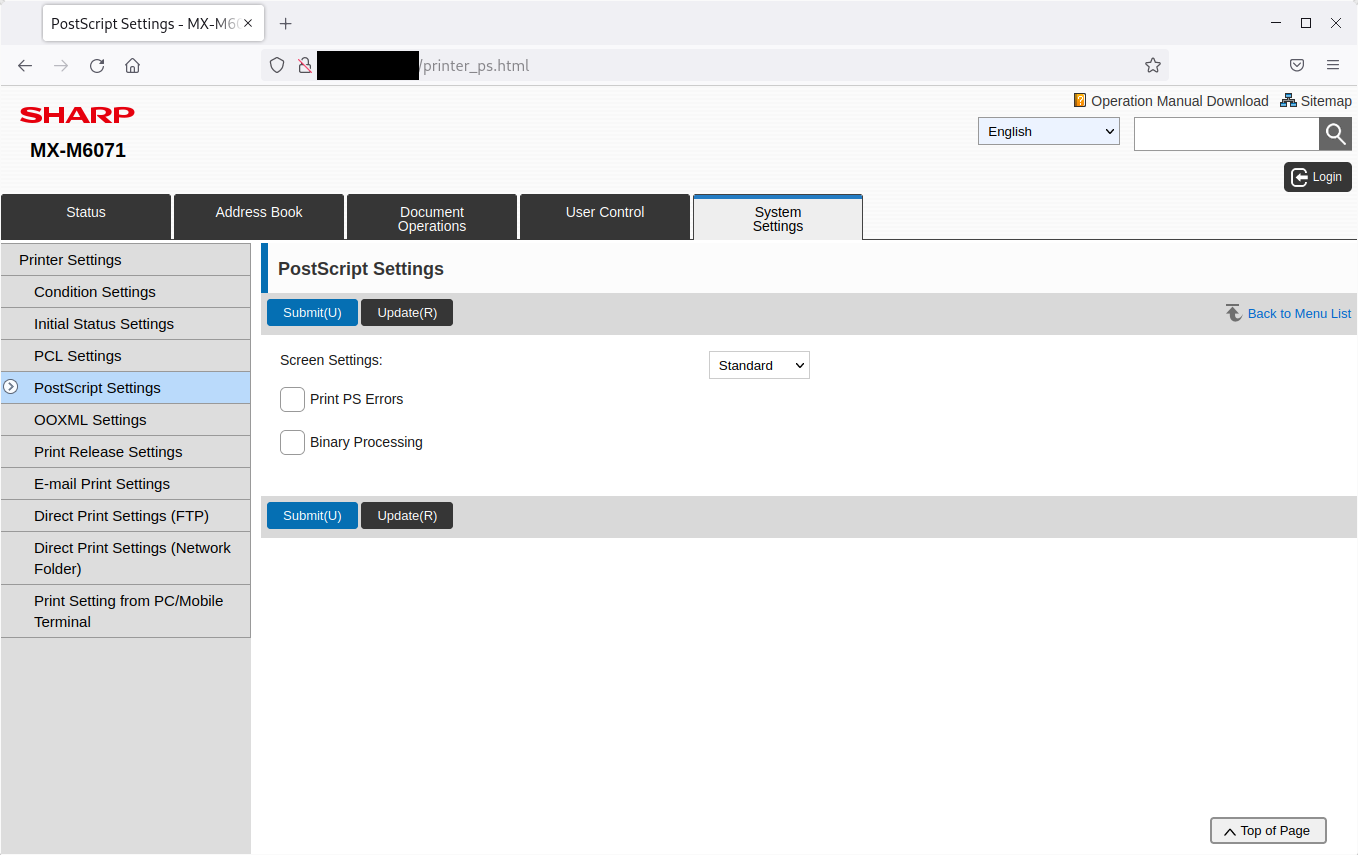
A Sharp printer vulnerability, tracked as CVE-2024-58388, allows unauthenticated attackers to read files on affected devices through the web manual download page. The flaw is a local file inclusion (LFI) issue in the installed_emanual_down.html pathway, where a mislinked file path parameter permits directory traversal without requiring login. Evidence cited in the report includes a public proof-of-concept and a ready-made Nuclei template, making the vulnerability easy to scan for at scale.
The CVE is rated CVSS 8.7 (High, CVSSv4), and the advisory notes that core dumps retrieved via this route can contain credentials, enabling attackers who obtain passwords to access other systems on the network. Exploitation in the wild was observed from July 2024, with CVE assignment recorded later, on 1 October 2026.
Impact and response are summarised with the affected scope as Sharp multifunction printers, including rebranded Toshiba Tec models, though specific models and firmware builds are not named in the record. Practical mitigations include applying the latest firmware from Sharp or Toshiba Tec, removing printer web interfaces from the internet, restricting admin panel access to trusted subnets, and changing passwords stored on the device since credentials may already be compromised.
Given the public PoC and established exploitation, the guidance treats exposed units as potentially compromised and urges remediation through vendor advisories. The article attributes findings to VulnCheck and the VulnCheck advisory, and notes the PoC publication by researcher Pierre Kim.