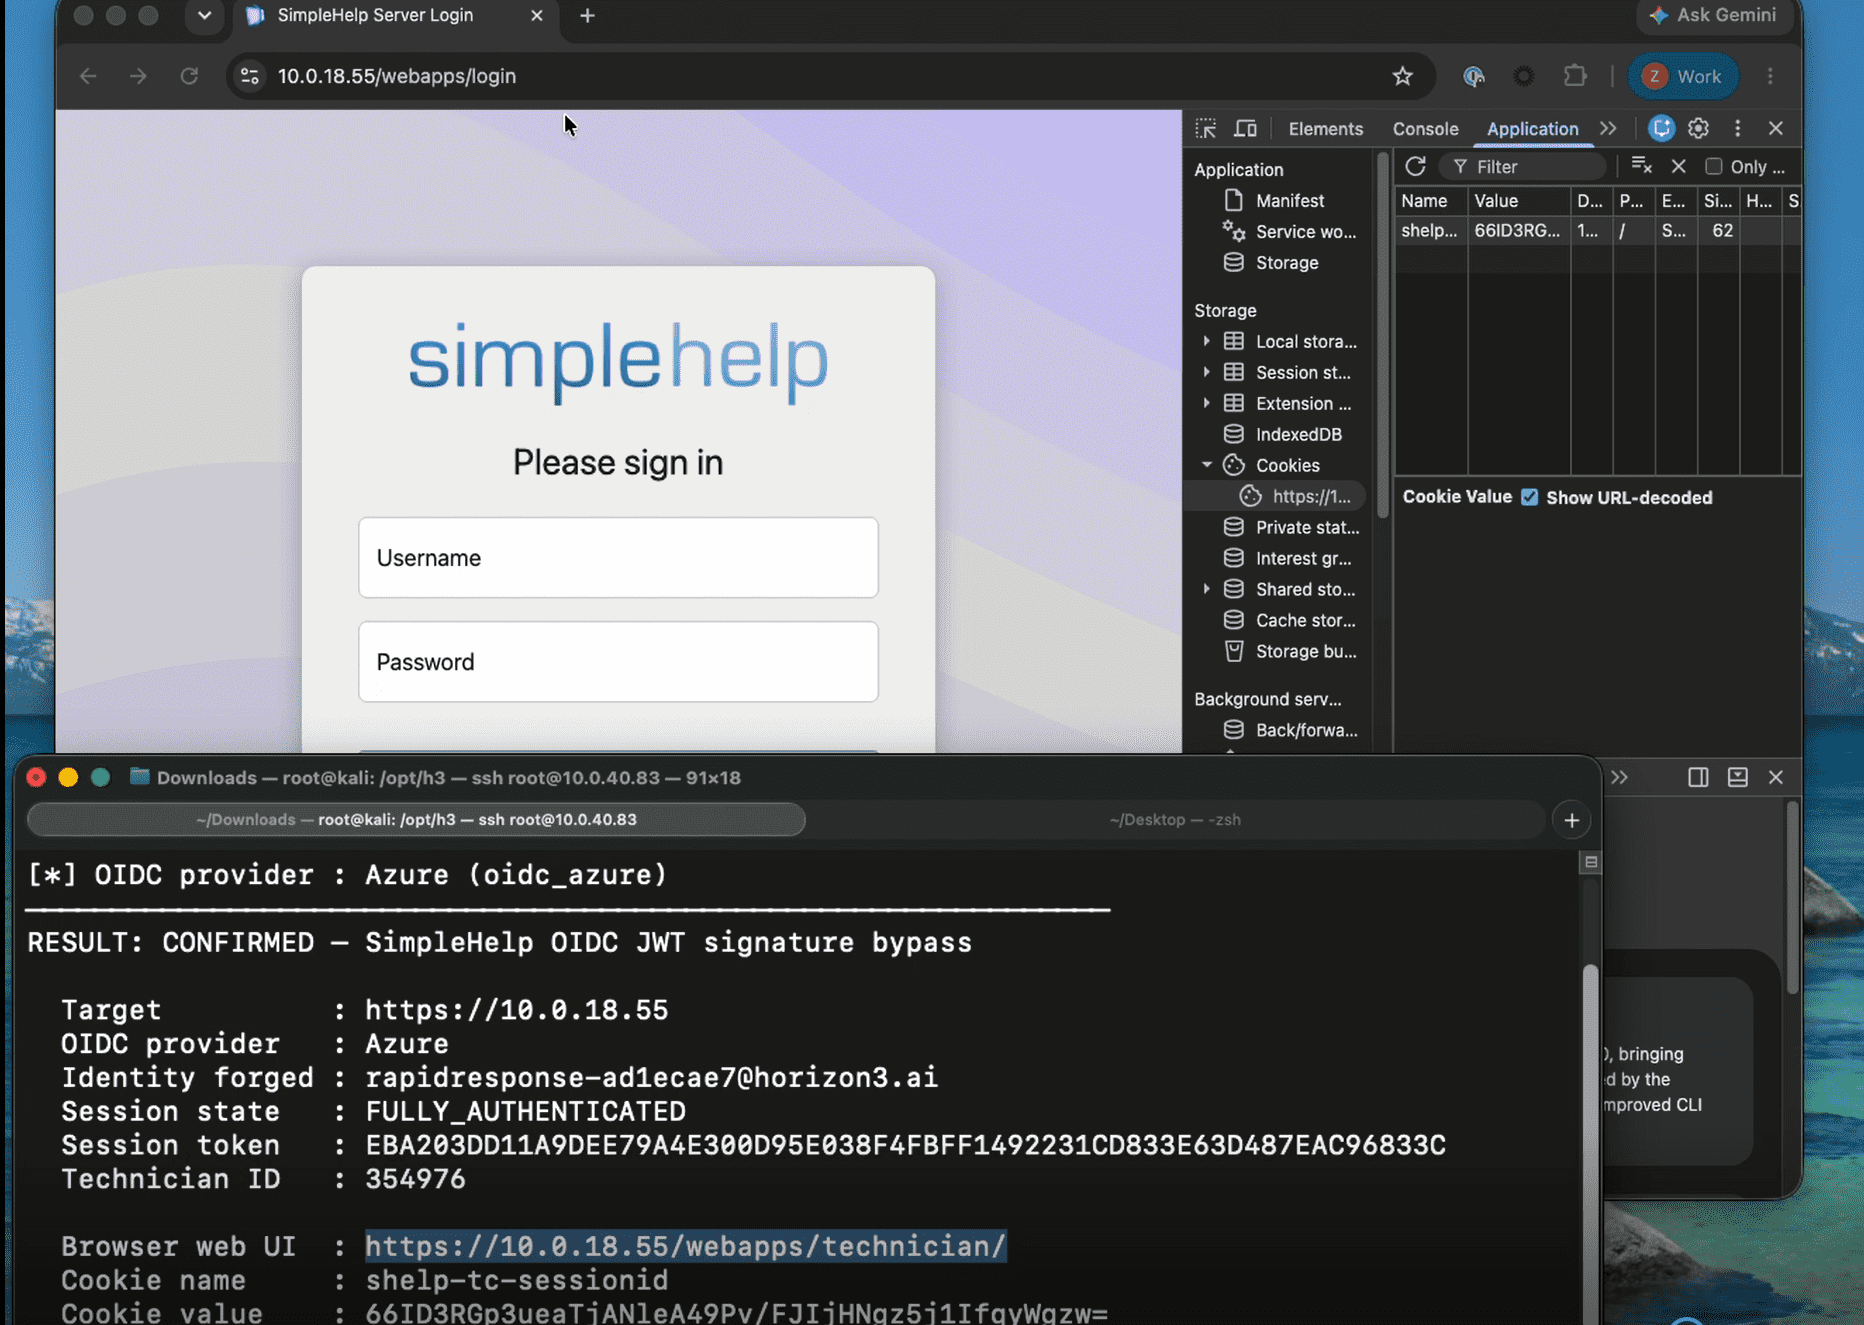
A critical vulnerability identified as CVE-2026-48558 in SimpleHelp remote management software poses serious security risks. This flaw allows unauthenticated attackers to bypass authentication mechanisms and gain administrative control. The vulnerability is linked to failures in the application's OIDC authentication flow, where manipulated identity tokens can be accepted without verification.
As a result, an attacker can obtain unauthorized access to technician accounts, sidestep multi-factor authentication (MFA), and potentially execute malicious scripts within corporate environments. Exposed servers running vulnerable configurations have surged from 3,400 to nearly 14,000 globally. To mitigate risks, organizations are advised to apply software patches and implement strict network controls like IP restrictions to prevent unauthorized access.