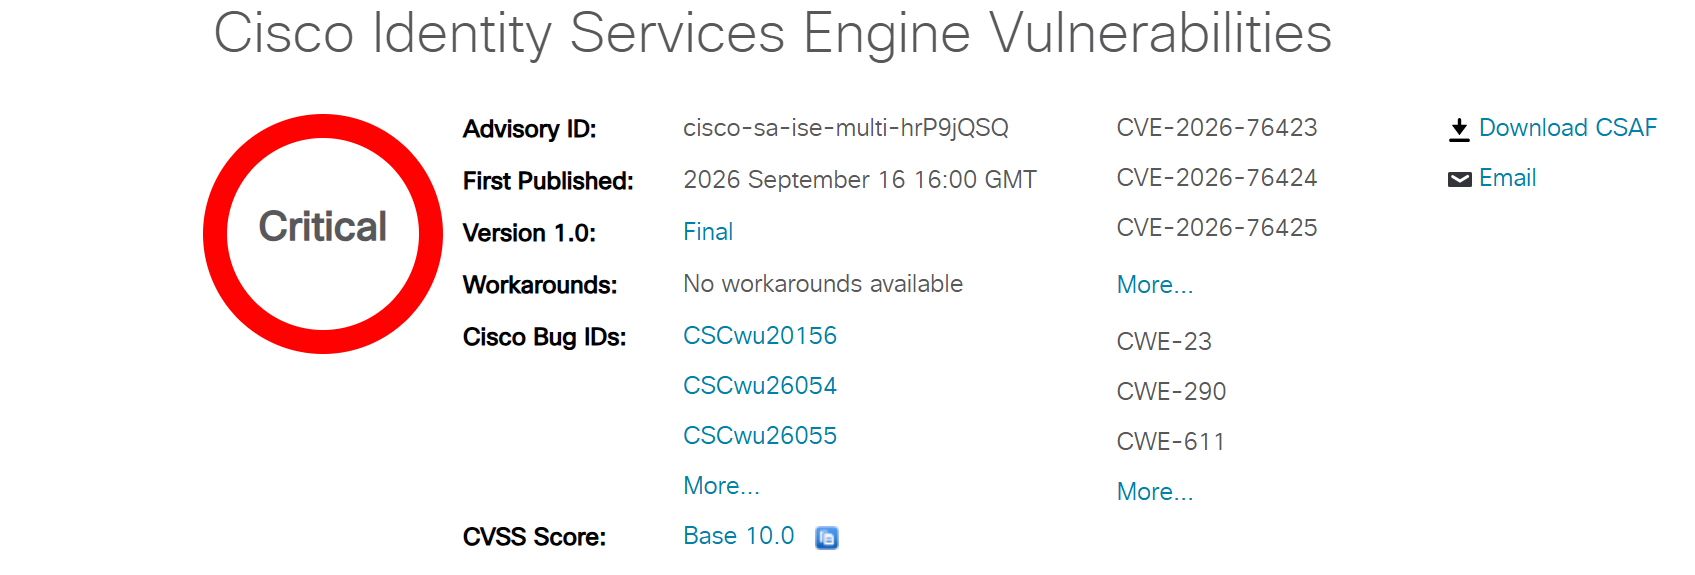
CISCO issued advisories on 16 September 2026 for five critical vulnerabilities in Identity Services Engine (ISE), used to manage network access for employees, devices and visitors. The flaws affect ISE releases 3.1, 3.2, 3.3, 3.4 and 3.5, with some also affecting ISE Passive Identity Connector deployments. None of these specific CVEs has been confirmed as exploited.
The highest-rated issue, CVE-2026-76423, has a CVSS v3 score of 10.0 and allows unauthenticated remote attackers to obtain administrative access through insufficient authorisation checks in the REST API. Other vulnerabilities include CVE-2026-20307 (CVSS 9.9), which can enable remote code execution through insecure deserialisation of Java objects; CVE-2026-20305 (9.1), involving command injection; and CVE-2026-20284 (9.1), involving SQL injection in the SXP REST API.
Cisco said the findings were identified through internal security testing, including testing with frontier AI models. Some command-injection flaws require authentication but could allow attackers to execute commands on the underlying operating system and elevate privileges to root.
Cisco has released fixes in ISE 3.1 Patch 12, 3.2 Patch 11, 3.3 Patch 12, 3.4 Patch 7 and 3.5 Patch 4. Administrators should install the applicable update or move from older releases to a supported version. Cisco says there are no complete workarounds, although access control lists can restrict management traffic to trusted internal subnets.