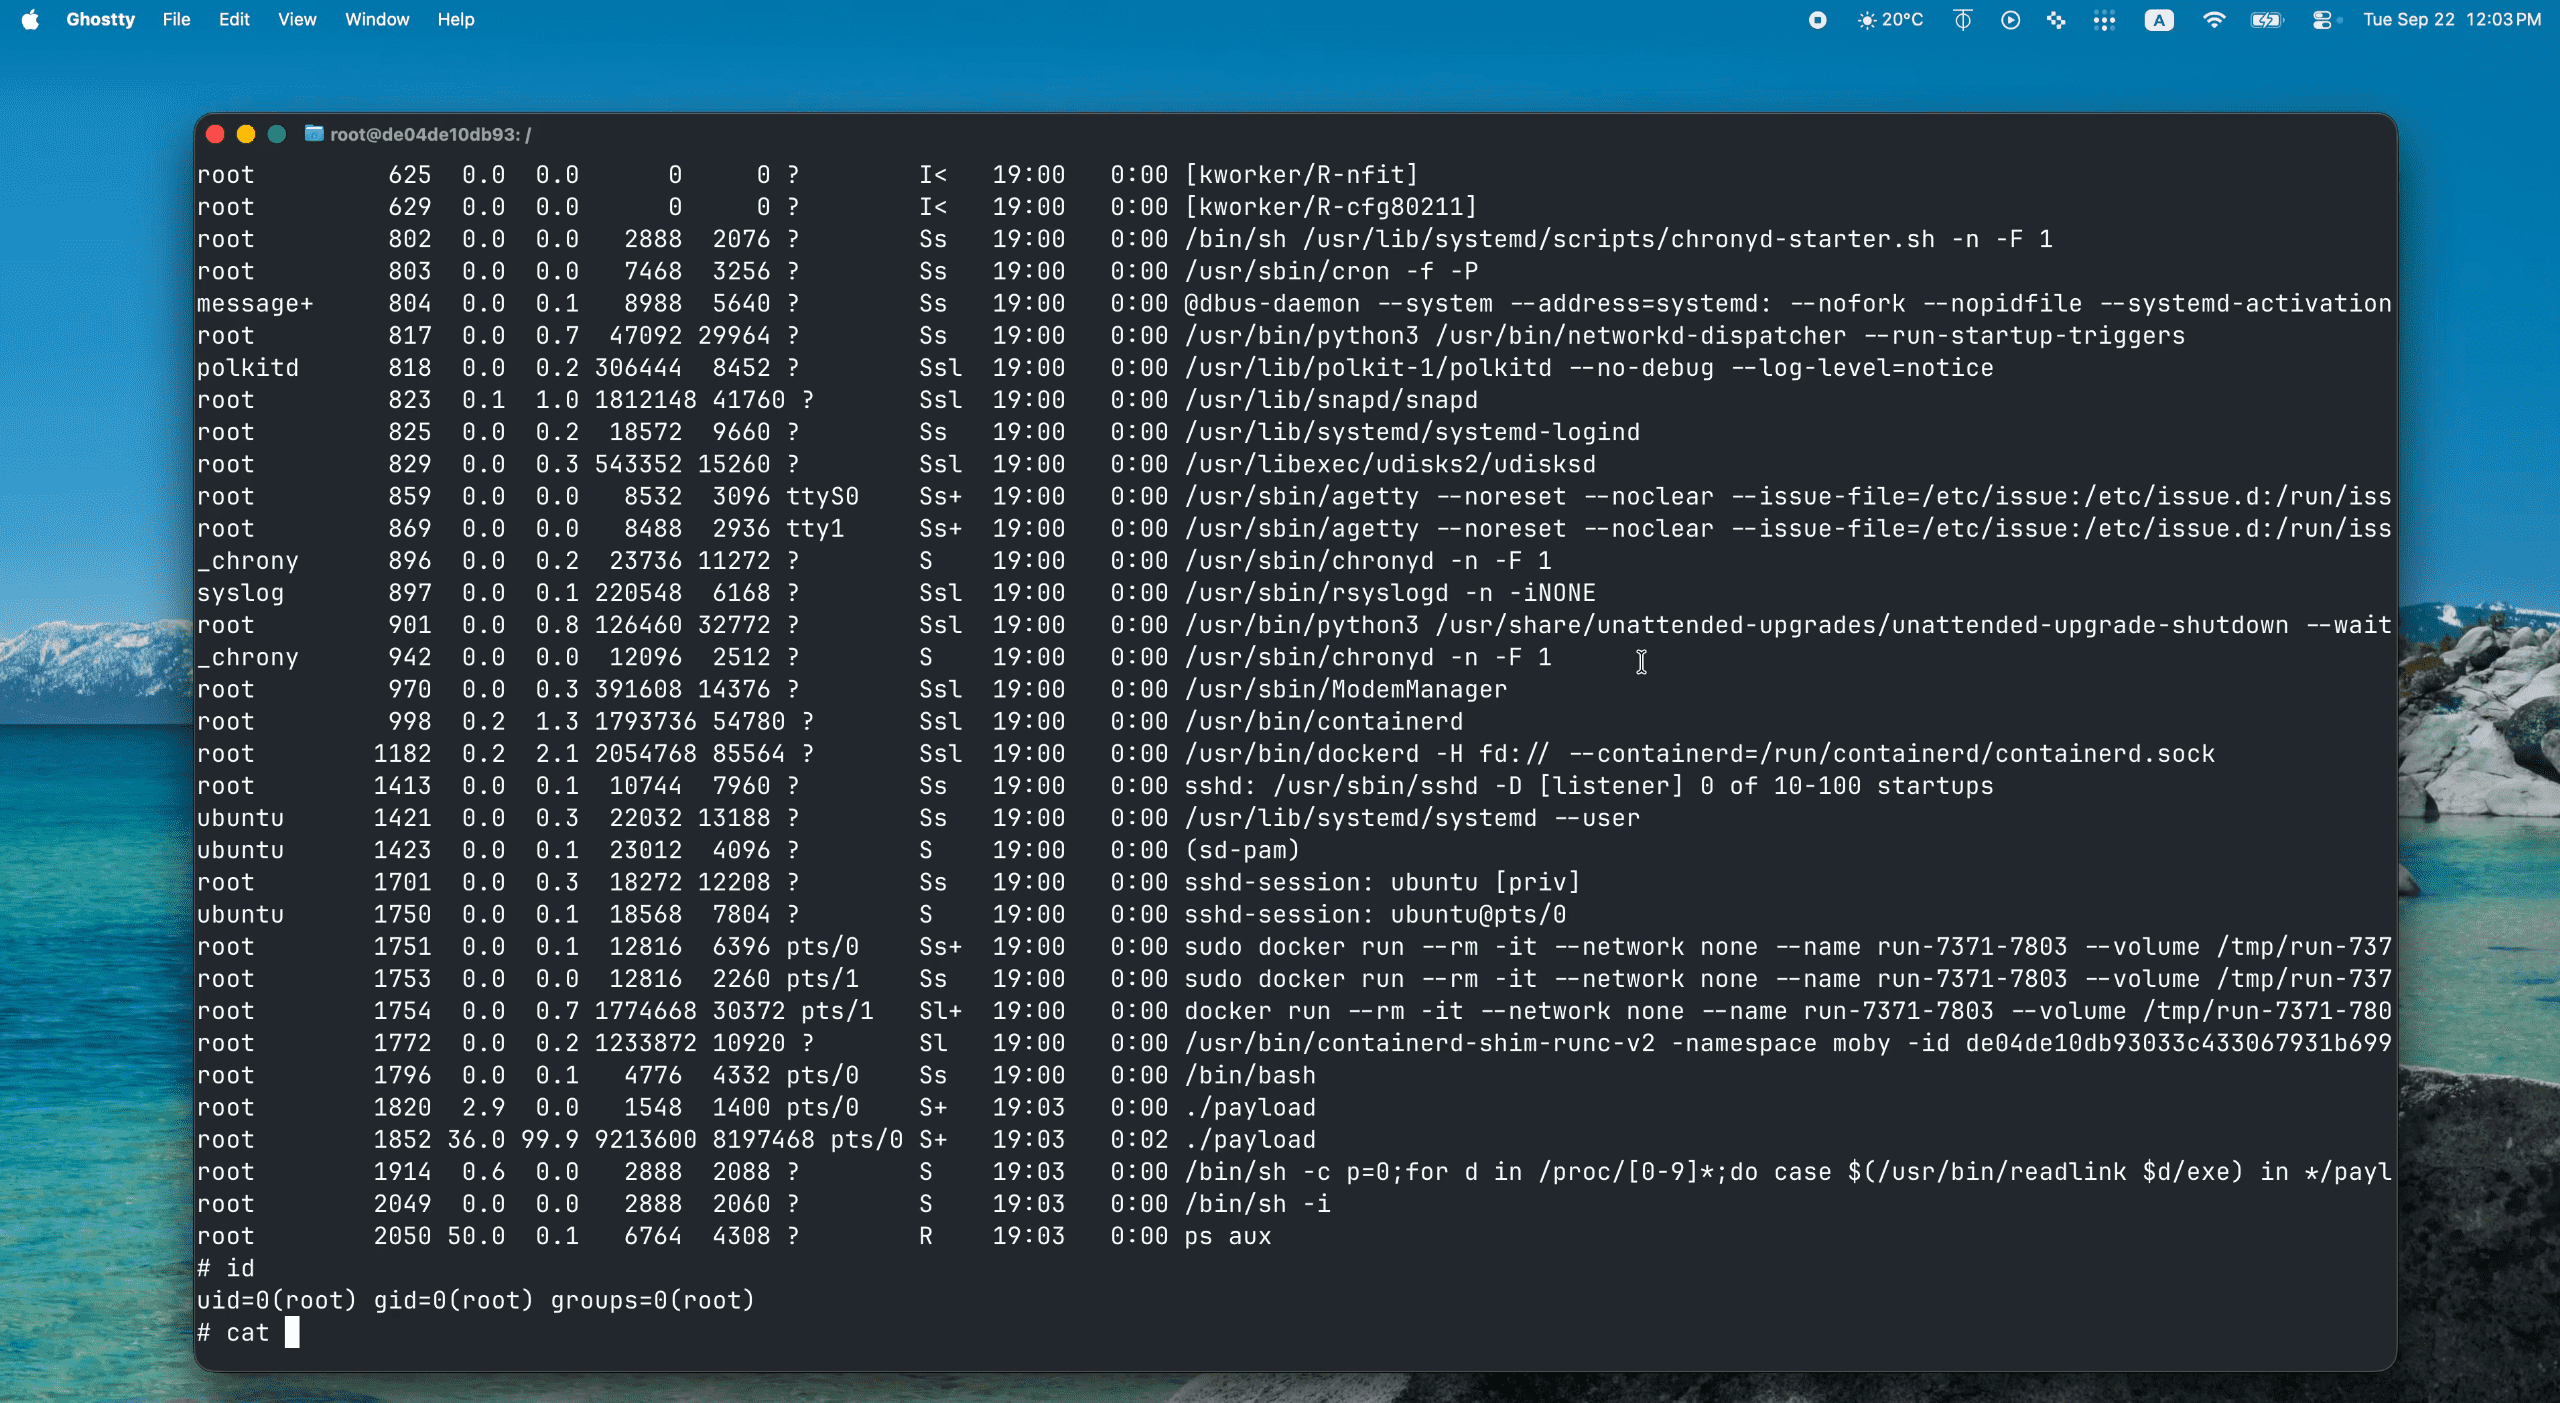
SECURITY researchers have disclosed CVE-2026-80521, a Linux kernel vulnerability rated 7.8 (High) that could allow an unprivileged attacker to escape a container and take control of the host. The flaw affects the AF_UNIX socket family’s garbage collection of SCM_RIGHTS messages. According to researcher Zhenpeng Lin of DepthFirst AI, a timing error can cause the kernel to free a socket vertex without removing it from its persistent `scc_entry` ring.
A later garbage-collection pass can then dereference the stale pointer, triggering use-after-free memory corruption and potentially enabling kernel-level code execution.
The article says researchers demonstrated a zero-day exploit in July 2026 during Google’s kernelCTF competition and have since published technical analysis and working exploit code. It reports that the exploit runs against Ubuntu 26.04 and that isolation tools including nsjail, Firejail and Bubblewrap may also be undermined. However, there is no confirmed exploitation by cybercriminal groups in the wild. Affected identifiers listed include 6.1.141, 6.6.93 and 6.10, alongside several specific commits.
Administrators should apply the listed upstream fixes, including `1293fd69a50d188a5788b08ba3741a3e86be1608`, `fe198b077864feafd4aa4b33b1a5ce26f50195a2`, `e3702470ced94fad74d71e2232f022d2eb752a6d` and `594d905195024b228c962627ae5ae7c17bd582a4`. The article also recommends using microVMs to isolate untrusted workloads while patching.