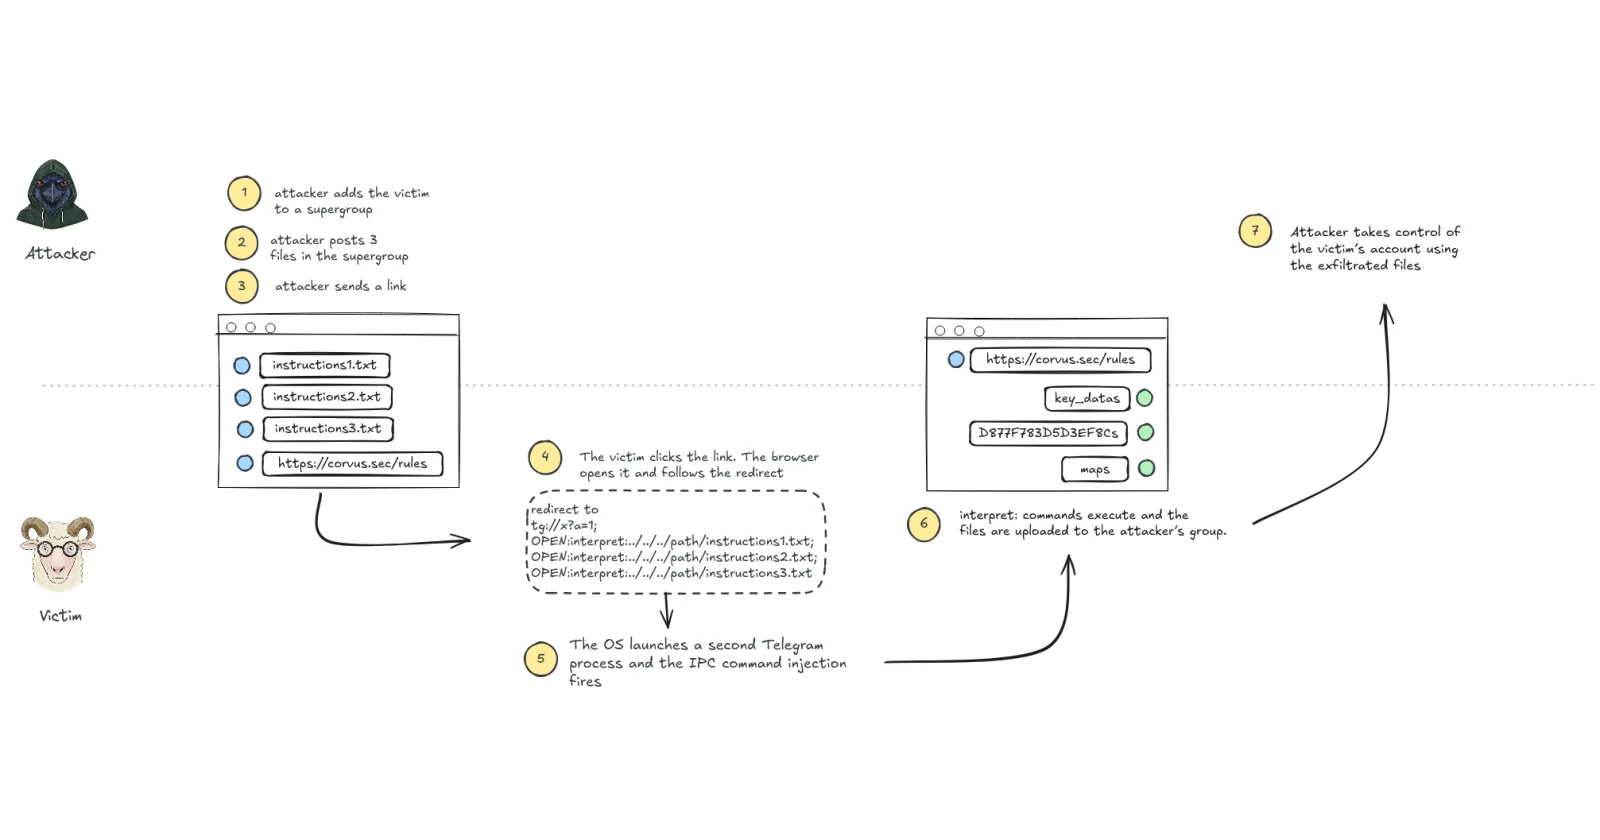
SECURITYRESEARCHERS publicly disclosed a high-severity vulnerability in Telegram Desktop, designated CVE-2026-107181, which enables an account takeover through a remote attacker stealing session keys with a single click. The flaw affects Telegram Desktop versions up to and including 7.2.8, with exploitation tied to an IPC Record Injection via an interpret: URI scheme.
A proof-of-concept exploit has been released publicly, increasing the immediacy of risk, though authorities have not confirmed active exploitation in the wild as of the report date.
In practice, the attack leverages an inter-process communication flaw in the application sandbox. Telegram Desktop communicates with running instances over a local socket and does not escape the record separator used to split commands. An attacker can craft a malicious link containing unescaped semicolons, causing the client to process injected commands that read local files and exfiltrate session data to the attacker, effectively cloning the active session.
The reported chain involves the attacker first sending a disguised text file to a group chat, prompting automatic download, then delivering a crafted hyperlink to the victim, whose click triggers the local socket to reveal the session keys. Telegram developers have patched the issue in version 7.2.9 by removing the vulnerable interpret: scheme and improving escaping of record separators. Interim mitigations include enabling “ask where to save each file,” tightening group invitation controls, and configuring a local desktop passcode.