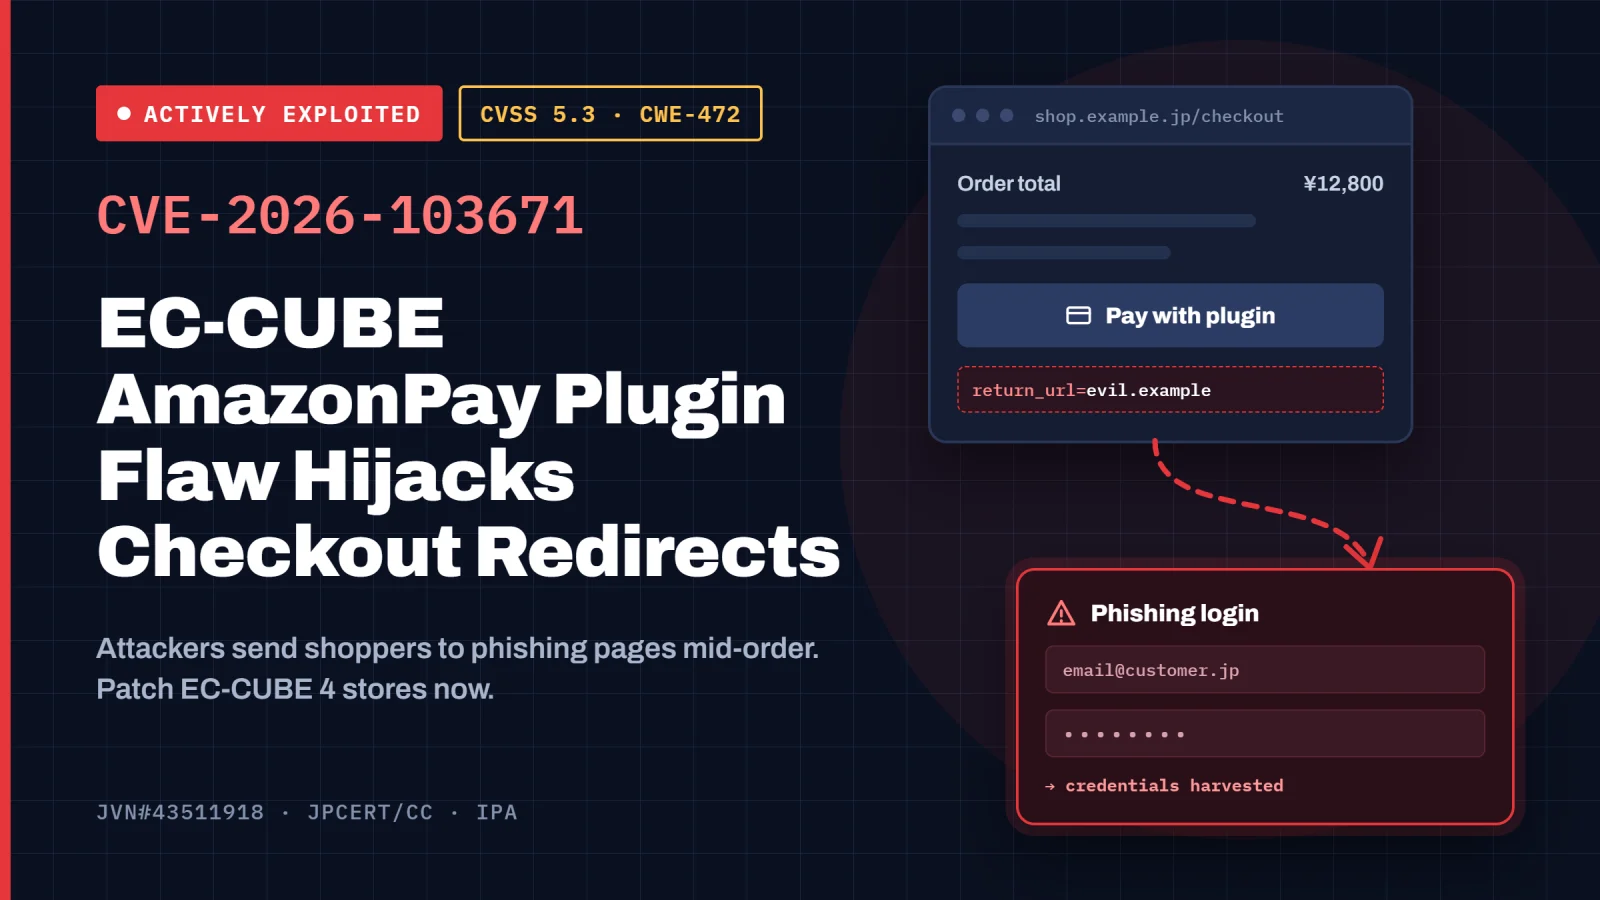
EC-CUBE’S AmazonPay Plugin is under active exploitation for CVE-2026-103671, with JPCERT/CC, IPA and EC-CUBE reporting threat actors are weaponising the flaw in the wild. The vulnerability allows unauthenticated attackers to tamper with checkout parameters that the server expects a browser cannot alter, enabling malicious redirects during order processing. In practice, a redirected shopper may land on an attacker‑controlled site where login credentials and personal data could be harvested. The advisory notes that exploitation has been observed, though there is no public PoC confirmed by the vendor or JPCERT/CC at this stage.
Affected products span EC-CUBE 4 series plugins, including AmazonPay V2 Plugin (4.0/4.1 series) versions from v1.0.0 up to v1.1.12, and v4.2.0 to v4.3.1 (including the 4.3.1 Bundle Edition); and the AmazonPay Plugin CV1 (4.0 series) up to v1.3.0 and earlier. The CVE carries a CVSS v4 score of 5.3 (CVSSv3.0: 4.7), with EPSS around 0.2% (30‑day).
Mitigation centres on applying the vendor patch promptly and reviewing web server logs for suspicious checkout redirects, with guidance to update the payment extension per EC-CUBE’s security notice and patch guide. Administrators are advised to contact affected customers if any redirects are observed. The vulnerability is classified as CWE-472, external control of assumed‑immutable web parameters, and is exploited via rogue checkout links to capture usable data.