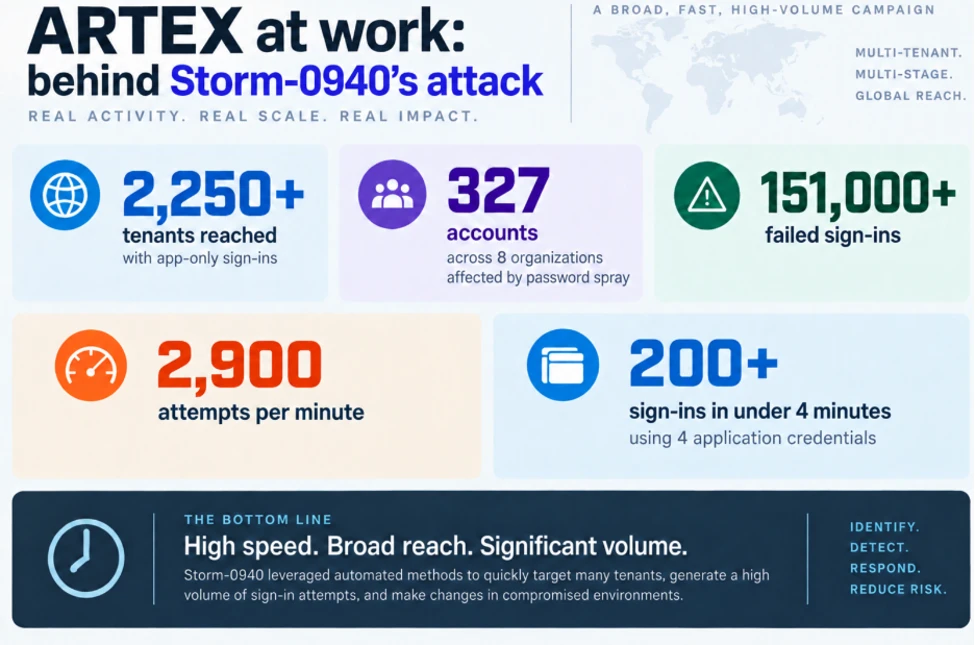
MICROSOFT has attributed the ConnectWise Cloud Backup supply chain incident to Storm-0940, a China‑state aligned group, which it says used ARTEX, an open‑source AI‑driven pentesting framework, to scale attacks across hundreds of Microsoft 365 tenants. According to Microsoft, ARTEX allowed the group to run attacks at machine speed against organisations in sectors including aerospace, defence, energy, financial services, government, and manufacturing. In some campaigns, the time from targeting to achieving privileged cloud access was reported to be under three hours.
Prior to exploiting ConnectWise credentials, Storm-0940 conducted a password spraying campaign between 10 and 14 October. Microsoft observed over 151,000 failed login attempts across 327 accounts at eight organisations, with peak activity on 11 October at about 2,900 failed attempts per minute; 48 accounts each received more than 1,000 failures.
After the breach became public on 15 October, the attackers shifted from password spraying to abusing already‑granted ConnectWise credentials to log into customer Microsoft 365 environments without requiring interactive sign‑in. In affected environments, the actors moved into Microsoft Graph, performed directory reconnaissance, and attempted changes to credentials, identities, groups and privileged roles to establish persistence.
Microsoft notes that the ARTEX‑driven activity can leave backdoors even after the original application is revoked, since attackers may add credentials to trusted applications. The report also points to other threat actors in several regions using ARTEX; ARTEX originated as open‑source in Go and supports multiple AI agents, though details vary by campaign.