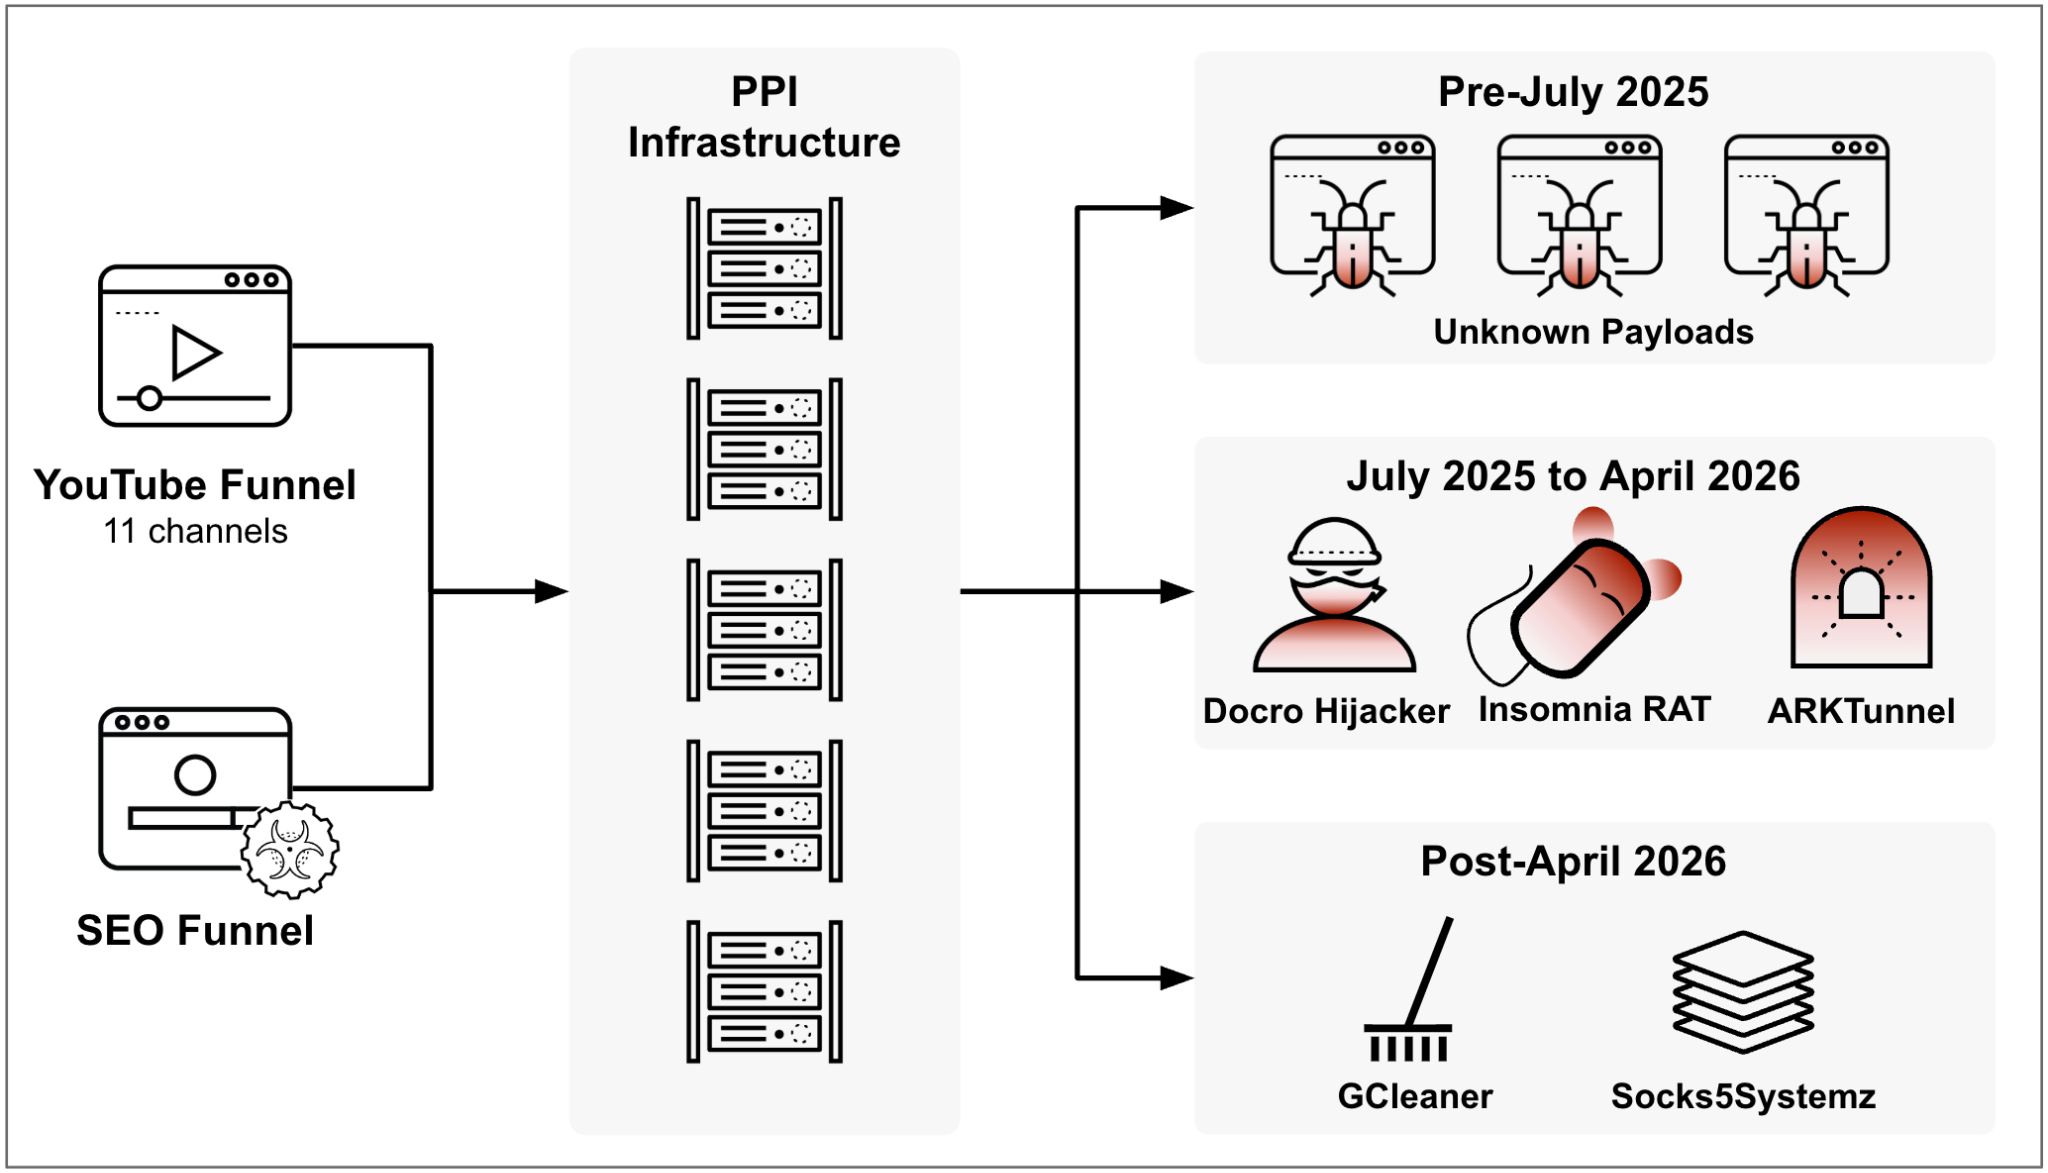
UNIT 42 researchers have identified more than 10,000 distinct OfferLoader malware samples linked to a pay-per-install operation active for at least two years. The suspected cybercrime syndicate, tracked as CL-CRI-1171, distributes trojanised software installers through 11 gaming-focused YouTube channels and search-engine optimisation poisoning.
The channels reportedly have hundreds of thousands of subscribers and millions of views, while poisoned results imitate pages for tools such as Bluetooth drivers and disk-management utilities. Researchers said the infrastructure fingerprints visitors, including their browser, operating system and search terms, showing benign decoys to automated scanners and malicious archives to selected users.
When a victim runs an installer, OfferLoader contacts a gate server and can launch three separate payloads. Insomnia RAT establishes persistence using disguised scheduled tasks and reportedly disables Windows Defender protections; ARKTunnel is hidden in bitmap images, installed as a delayed-start Windows service and used for remote access over WebSocket connections; and Docro Hijacker alters Chrome’s Secure Preferences file to change search providers and inject adverts across more than 190 search domains.
Unit 42 describes each payload as an independent “offer”, allowing operators to change the malware delivered. The researchers recommend treating an OfferLoader detection as a potential entry point for a wider intrusion, monitoring unexpected Node.js or Python activity from temporary directories and suspicious scheduled tasks, and inspecting outbound WebSocket traffic and browser-preference changes.