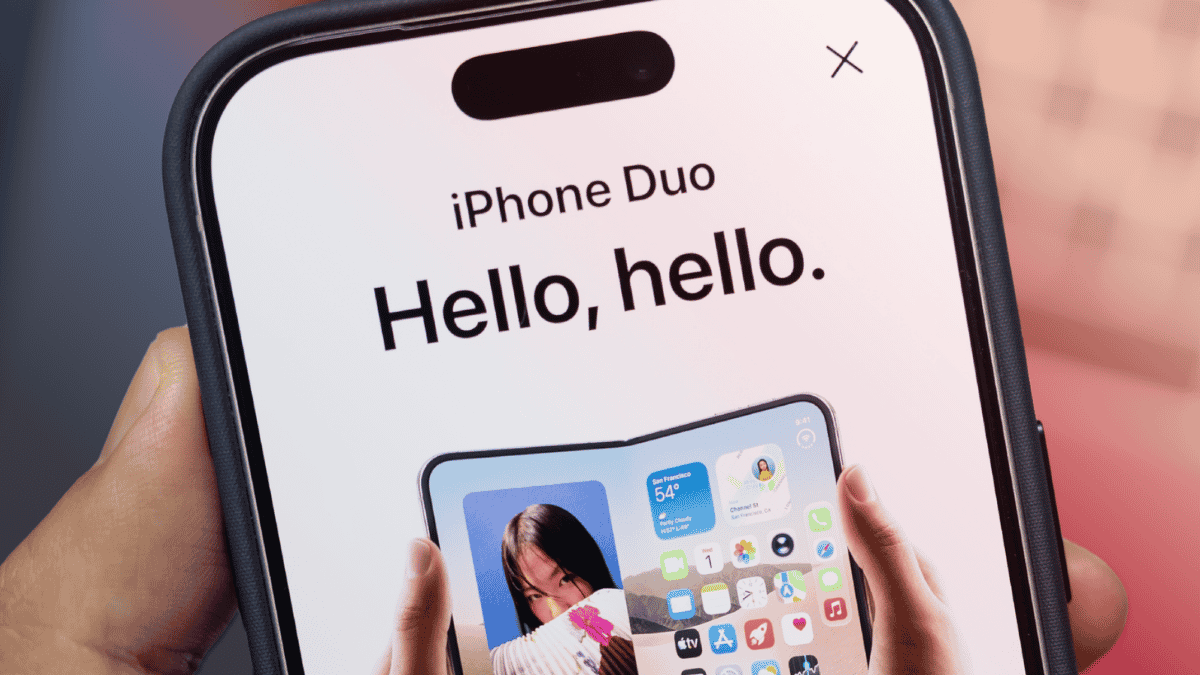
MALWAREBYTES says a fake Apple-style iPhone Duo preorder page is being used to deliver the leaked DarkSword iOS exploit chain. Published on 29 September 2026, the page advertises a $500 voucher, AppleCare+ and a countdown, but Apple’s genuine preorders do not open until 16 October. The fraudulent form requests contact details but, in the captured version, does not transmit them or place an order. Instead, the exploit attempt starts as soon as the page opens, without requiring a download, tap or approval.
The page attempts to direct iPhone visitors to Safari, checks the reported iOS version and loads corresponding code through an invisible frame.
If successful, the payload could obtain device and app information, Apple Notes, keychain credentials, cryptocurrency wallet data, messages, call history, contacts, voicemail, email, calendar entries and cached location data. It can also retrieve files and photos, execute server-supplied JavaScript and delete diagnostic reports. Malwarebytes analysed the code but did not test it on an iPhone or observe data leaving a device, so the report does not confirm successful compromises.
Several elements match the DarkSword chain documented by Google in March; Apple has patched the relevant vulnerabilities. Malwarebytes has not established the page’s precise affected iOS range, and an iPhone reporting an older version to Safari does not prove it is vulnerable. Users should update iOS, avoid unfamiliar preorder links and restart an affected phone after updating. Potentially exposed passwords and cryptocurrency wallets should be secured from a trusted device. The identified infrastructure includes `pnmrud[.]cc` and `cloud[.]cmatgldn[.]click`.