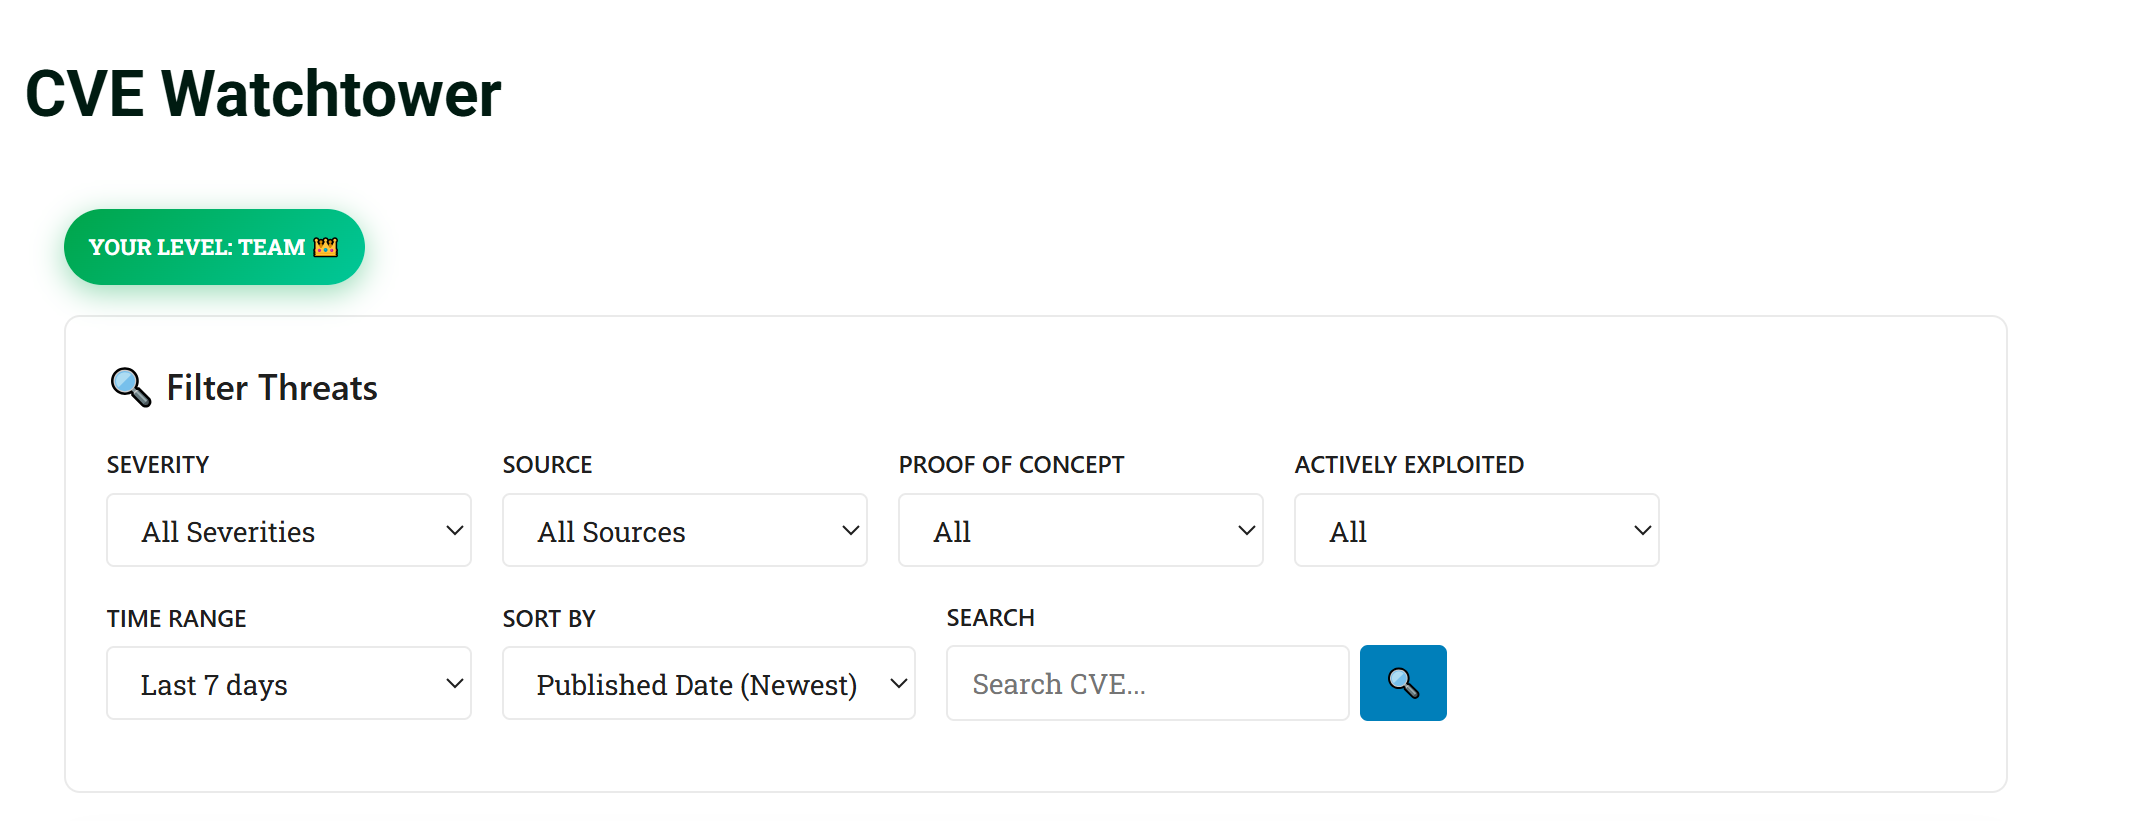
CVE Watchtower is described as a service that tracks new CVEs for selected vendors and products, scores them for severity and exploitation likelihood, and emails users when a relevant CVE emerges. The guide walks new users through choosing a plan, creating an account, building a vendor watchlist, and understanding the statistics and alert pages they will use to manage notifications.
Users can choose from Free, Pro, and Team tiers, with different levels of access to CVE details and alert channels. Free provides a public feed, KEV and EPSS-based alerts, and a vendor watchlist but hides full CVE descriptions for admin-curated “Premium Threat Intelligence” items. Pro unlocks full CVE details for admin-curated items, plus additional alert channels and a welcome summary email. Team adds collaboration features and integration options such as Slack/Teams webhooks and GitHub exports. The pricing page shows the monthly costs and included features, and users can start with a 14-day free Pro trial.
The guide explains how to tailor alerts: create a Vendor Watchlist from a supported vendor list, and set two thresholds—EPSS and CVSS—to control which CVEs trigger emails. It also covers using Vendor Vulnerability Stats to view recent activity per vendor, and how to read a CVE detail page, including data sources, exploitation status, and whether a CVE is Reserved-but-Public. Troubleshooting and help contacts are provided, along with notes on how Premium Threat Intelligence items behave on the Free plan. The document is a practical, feature-focused walkthrough for first-time CVE Watchtower users.