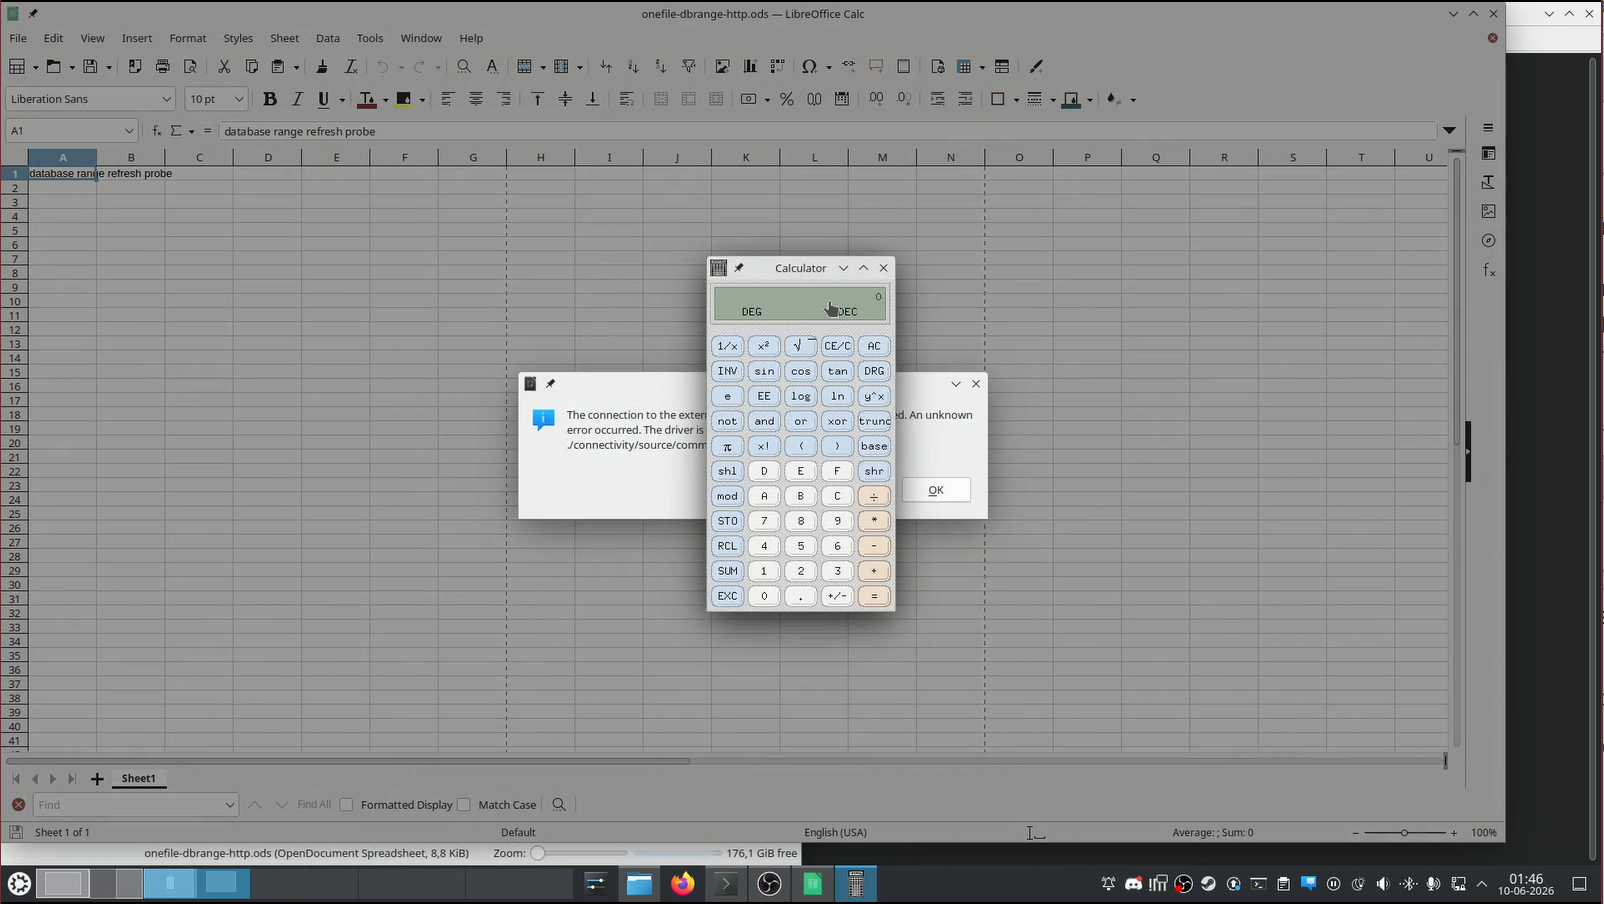
LIBREOFFICE Calc has a set of code-execution and data-leak flaws disclosed alongside public PoC exploit details. The focal point is CVE-2026-63277, a high-severity RCE in Calc that can run attacker-supplied Java code when a spreadsheet is opened, provided Java and JDBC support are enabled. The Document Foundation has stated these issues affect the LibreOffice 26.2 series prior to 26.2.5, with CVSSv4 scores peaking at 8.5 for the main flaw.
The PoC and technical write-up are publicly available, enabling rapid study by potential attackers, though there is currently no confirmed exploitation in the wild.
In addition to CVE-2026-63277, five related weaknesses stem from the same data-link feature that Calc uses to connect to external sources. These include CVE-2026-63266 (arbitrary file write via Firebird backup and data-mappings links), CVE-2026-63267 and CVE-2026-63268 (local file reads via data-mappings and CSV provider, with additional host-request possibilities in 63267), CVE-2026-63269 (data leaks through GStreamer on Linux via HLS playlists), and CVE-2026-63270 (environment/INI data leakage).
These are rated medium (6.7–6.8) and, unlike 63277, have not been exploited publicly to date. The guidance from security advisories is clear: update to LibreOffice 26.2.5 or 26.8.0, which contains the fixes and blocks external data links from loading arbitrary code.
Until patched, users should consider disabling Java in LibreOffice if not required, and exercise caution with spreadsheets from unknown senders.