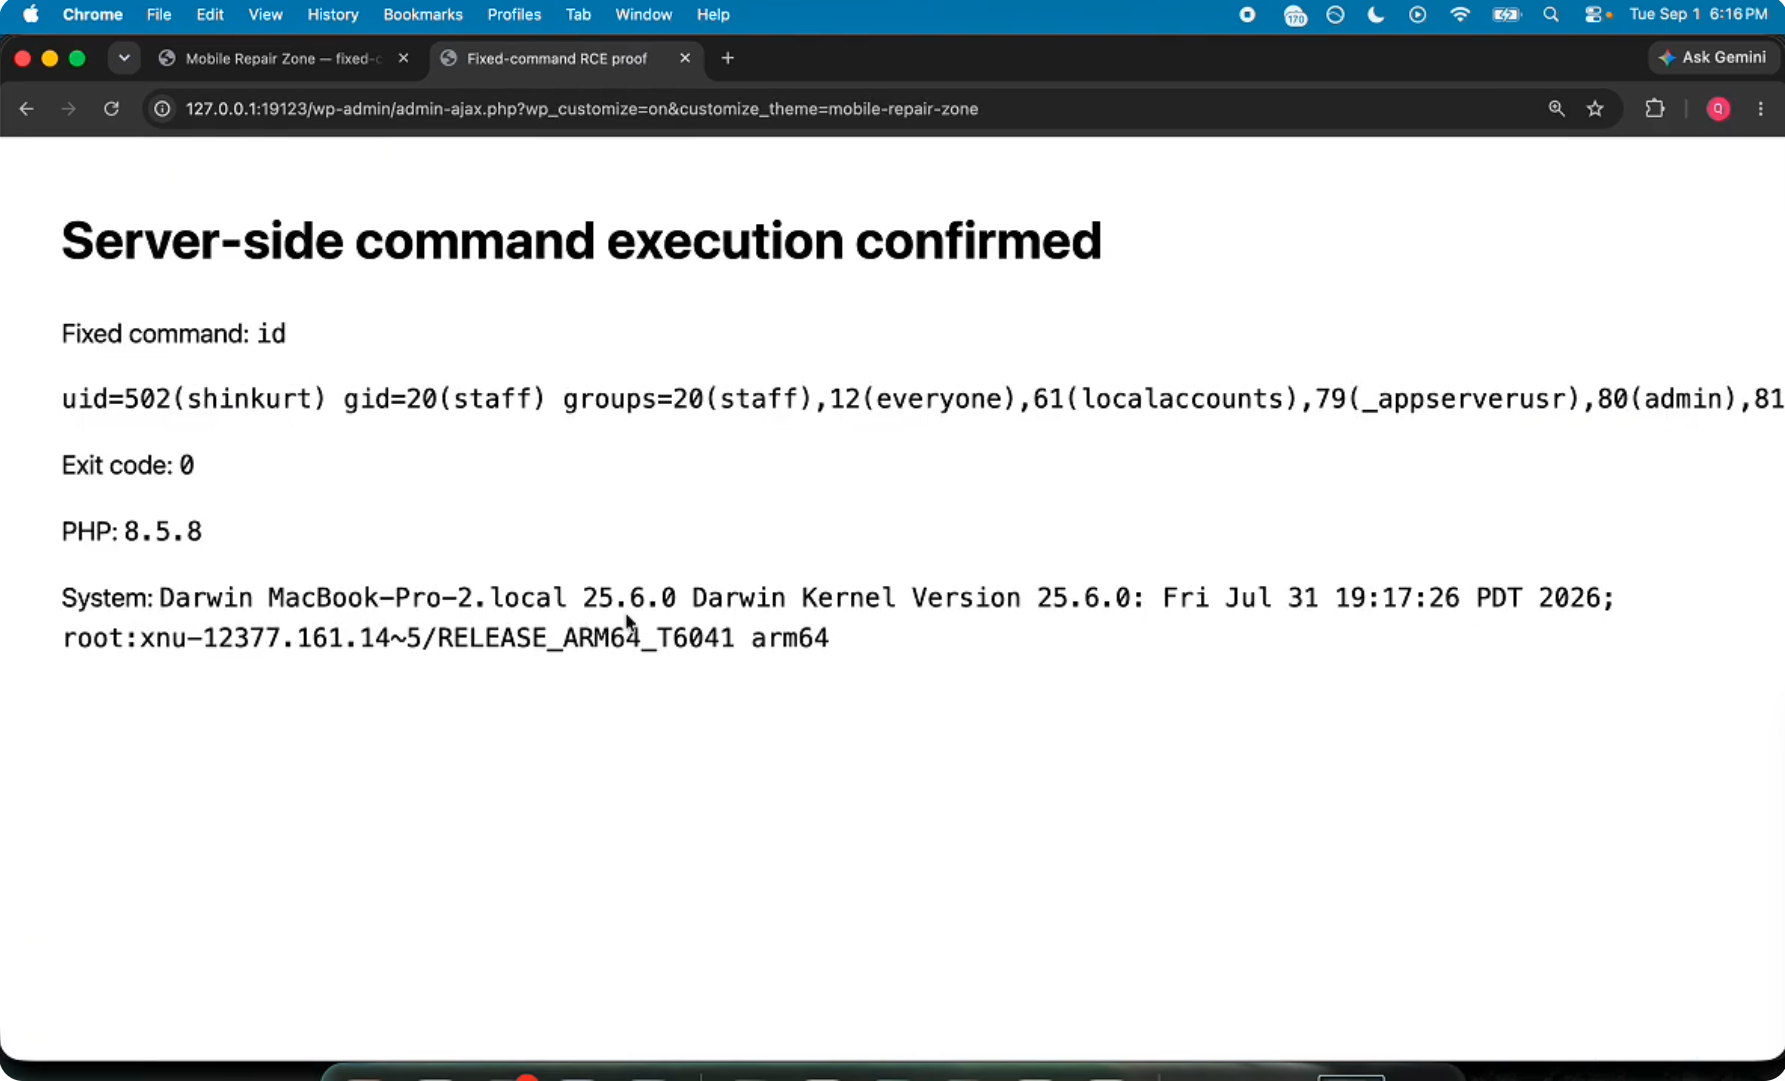
SECURITY researchers at pwn.ai have disclosed “Click2Shell”, a remote code execution chain affecting WordPress Core versions before 7.1.1. The attack does not require an account on the target WordPress site, but it does require a logged-in administrator to visit a specially crafted link. Researchers said the issue had not been exploited in the wild and that WordPress fixed it in a scheduled maintenance release. No official CVE identifier has been published.
The chain combines a client-side parsing flaw with weaknesses in certain third-party themes. A crafted theme parameter is handled differently by WordPress’s backend and browser code, allowing a jQuery selector injection to trigger automatic installation of a catalogue theme. During a Customizer preview, WordPress loads PHP from the inactive theme.
Researchers found an insecure AJAX handler in Mobile Repair Zone 2.5.4 and more than 40 other catalogue themes; the handler did not check user capabilities or nonces and accepted a remote package URL. An attacker could therefore make the server download and execute a malicious PHP archive under the web server account.
WordPress addressed the Core issue in changeset 63664 and version 7.1.1 by escaping the theme slug before passing it to jQuery selectors. Administrators should upgrade to WordPress 7.1.1, review installed themes and remove unused ones. The article also recommends restricting administrative access with IP allowlists.