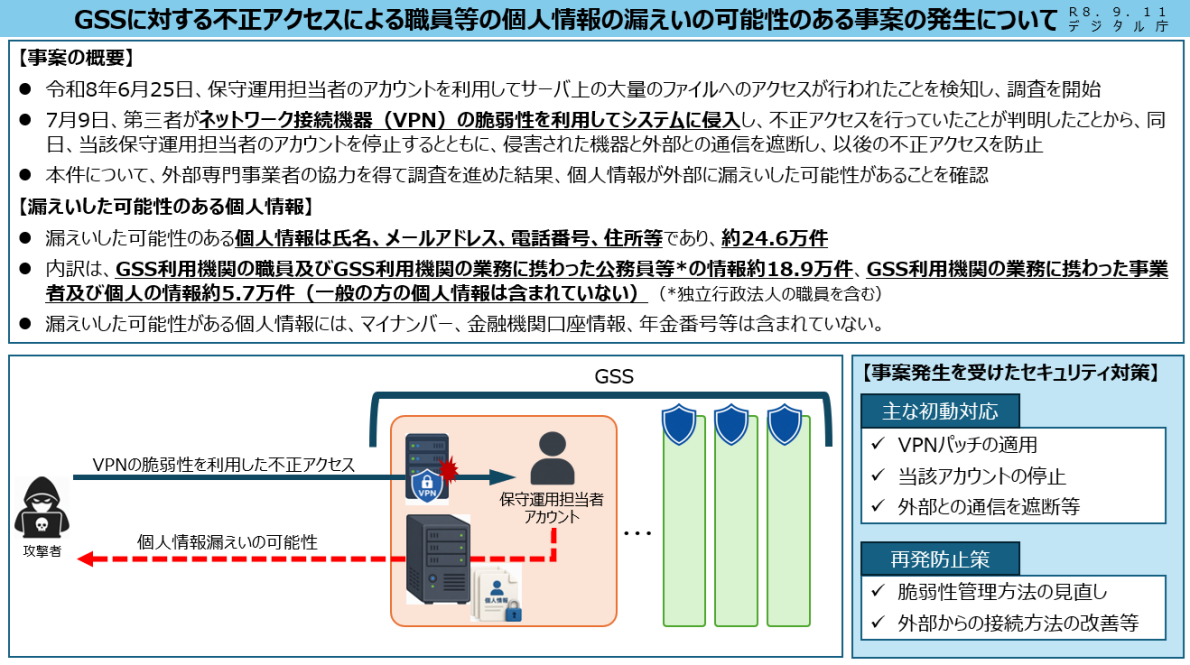
JAPAN’S Digital Agency has disclosed a breach of its Government Solution Service (GSS), a shared IT platform used by 23 ministries and agencies. Attackers exploited a medium-severity vulnerability in a VPN device, for which a patch was already available, and used a maintenance and operations staff member’s account to access files. The agency detected unusual activity on 25 June 2026, confirmed the VPN exploitation on 9 July and publicly disclosed the incident on 11 September. It has not identified the VPN product or vulnerability.
Approximately 246,000 records may have been exposed, including about 236,000 names, 231,000 email addresses, 94,000 telephone numbers and 1,000 physical addresses. Around 189,000 records concern government employees and officials, while 57,000 relate to contractors and other businesses or individuals supporting the organisations. The data did not include My Number identification numbers, bank-account details or pension numbers.
The agency said it suspended the compromised account and isolated the affected equipment on 9 July; an investigation involving an external security company found that the information may have been taken by an outside party. No misuse has been confirmed.
The privacy regulator was notified on 15 July. The agency plans to improve vulnerability management and alter external connection methods. It will contact affected individuals and warned that it will not request passwords or payments by email or telephone, amid concerns that the exposed contact details could support targeted phishing or impersonation scams.