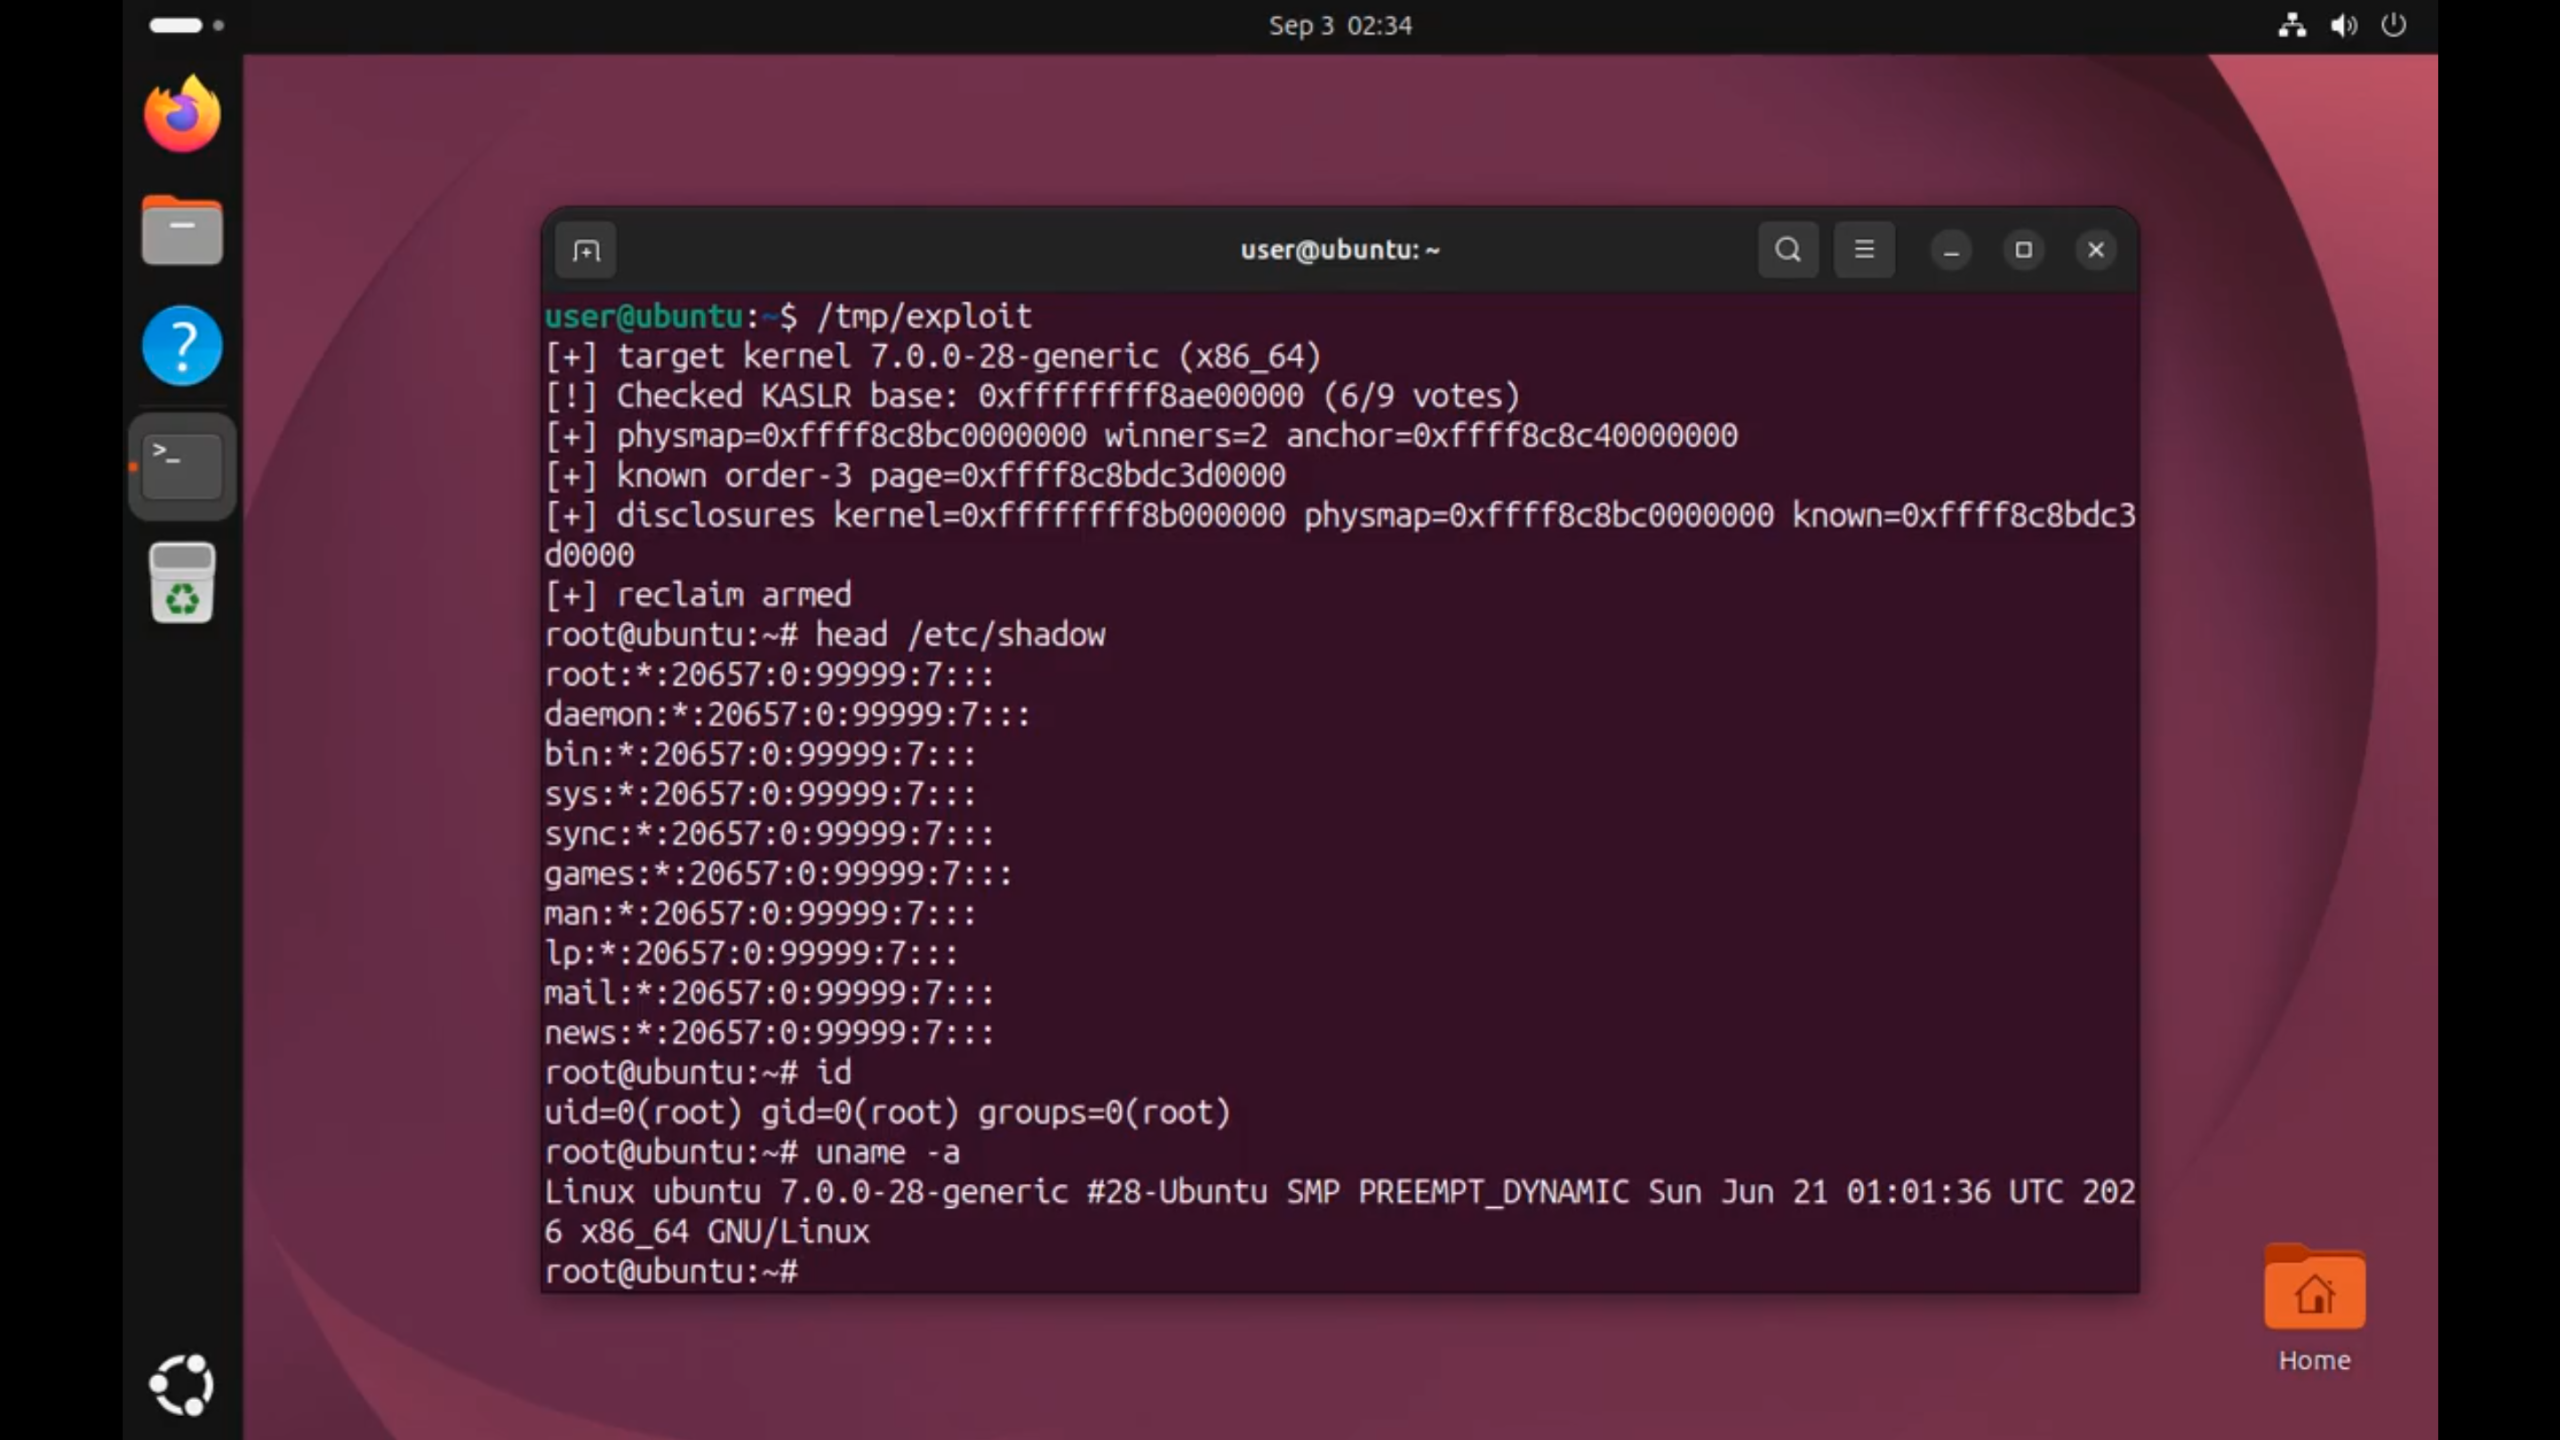
SECURITYONLINE [.]info reports that NebuSec researchers published technical details and a functional proof-of-concept exploit for Linux CVE-2026-52924, a high-severity use-after-free in the kernel SCTP handling during stale COOKIE-ECHO events. The PoC demonstrates local root privilege escalation, with a video demonstration posted by CyberMeowfia illustrating complete local compromise.
The article notes the vulnerability dates to code introduced in October 2017 and that upstream fixed the issue in June 2026, with Ubuntu 7.0.0-28 specifically tested. Although the PoC exists and appears working, the piece states there are no confirmed cases of exploitation in the wild at the time of writing.
At a glance, CVE-2026-52924 is assigned a CVSS score of 9.8 (Critical, CVSSv3). The advisory lists affected kernel references including 5bbbbe32a43199c2b9ea5ea66fab6241c64beb51 and 4.15, and notes the issue affects multiple long-term kernel branches. The patch deploys upstream changes that purge the association outqueue during stale-cookie events, dropping pending transmission state and clearing scheduler pointers.
The article advises updating to patched builds (examples include 84b7a319105db2f917ccdcf502bdc866082b1285, f46e1d1a758878f0d22c4fbbd1bf42bb7165d1e8, 3c0741a441a7df7099d7ca6a64a6a0de09c677c8, 2afc9e684dc7fecf73db1edc937ebbc47b4b68dc, plus 12 more) and, where SCTP is not required, disabling the protocol module as an alternative mitigation.
The article’s status line emphasises a low probability of observed exploitation to date, while highlighting the urgency of applying patches to mitigate local privilege escalation risks.