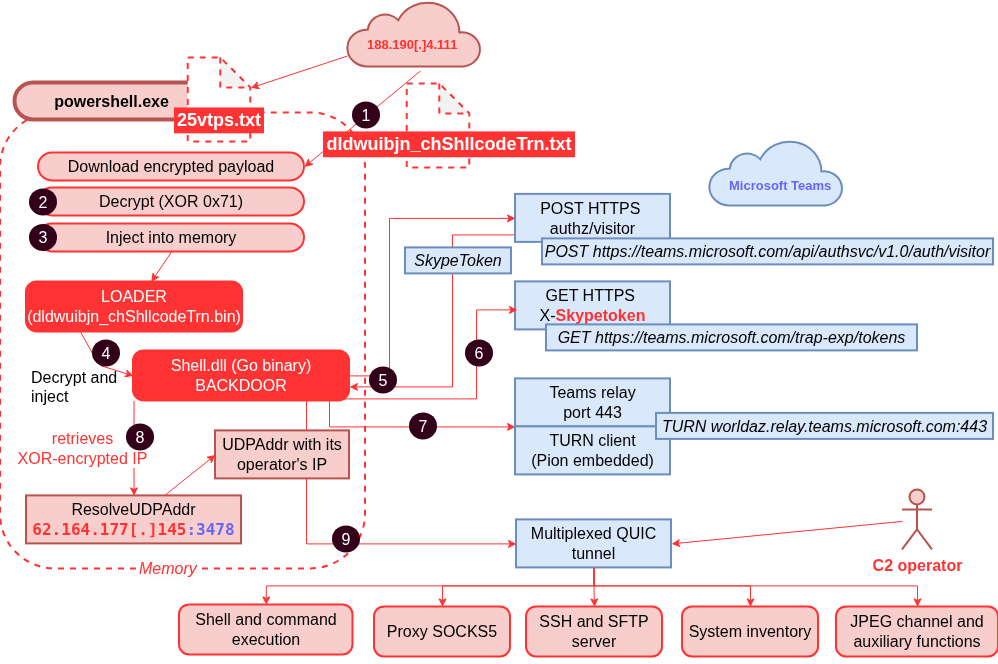
DRAGONFORCE has expanded its backdoor toolkit to use Microsoft Teams TURN relays as a covert command-and-control channel, with MQTT acting as a fallback path if the primary route is unavailable. The operation, attributed by Lab52 to the DragonForce ransomware group, describes two distinct backdoors active after an initial breach.
In Symantec’s earlier findings, the actors were observed occupying the environment of a US services firm for one to two months, leveraging the Teams TURN infrastructure to blend in with legitimate traffic.
The first backdoor is a Go-based in-memory implant that decrypts its server address at runtime and maintains a private SSH key, avoiding disk-stored plaintext. The second backdoor is more persistent: it is launched via a scheduled task and uses a legitimate Java executable to load a malicious DLL, which then fetches the next stage from an encrypted text file.
That loader file has a system-specific hash, rendered ineffective against simple hash-blocklists, and the text payload is protected with Windows DPAPI so it decrypts only on the originating machine. C2 communication rides on Teams’ TURN relays, with the attackers able to download task chunks, verify them via MD5, decrypt and execute payloads in new threads, and even upload data in small blocks during the initial handshake.
If TURN fails, the malware polls an MQTT broker for XOR-encrypted JSON messages, with tasks enabling URL fetches, PowerShell execution, or remote host connections. It also encrypts its memory region during idle periods to evade detection. Defence guidance focuses on monitoring for anomalous Teams-related traffic, non-standard Java DLL load paths, and memory-based scanning to detect these memory-resident backdoors.