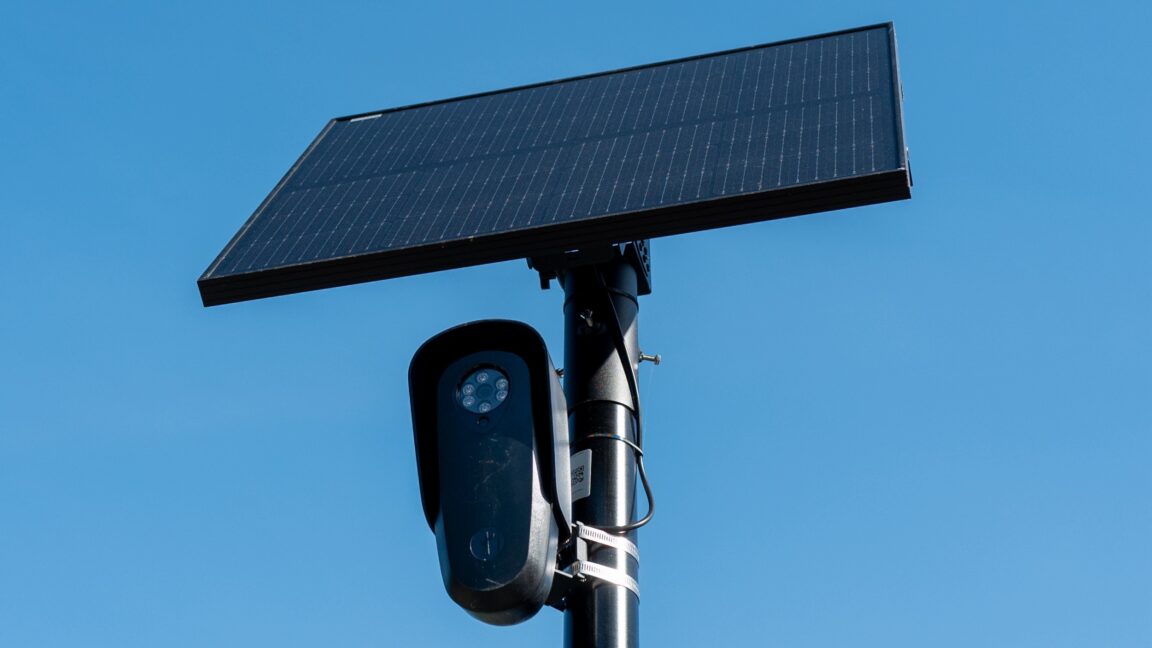
HACKERS calling themselves stegan0gram removed a Flock Safety automatic number-plate recognition camera and made an almost complete copy of its stored data, sharing the material with 404 Media, WIRED and Distributed Denial of Secrets. Their analysis found that the camera’s Android system contained unencrypted partitions, including one holding an encryption key that unlocked other stored media. Flock has promoted on-device encryption, but much of the camera’s most sensitive storage remained inaccessible.
The company said the removal and tampering were illegal, that it had received no vulnerability report, and that it could not assess the claims without more technical detail.
The recovered software showed the camera detecting people as well as vehicles, number plates and bicycles. It took rapid bursts of photographs—typically about 28 images per vehicle, though sometimes more than 100—and sent them to Flock’s servers for plate and vehicle identification. Logs covering roughly 21 days recorded about 50,200 vehicles and 1.6 million images.
Testing found people in 11 of 27,321 short video clips, all riding motorcycles, while the plate detector sometimes cropped bumper stickers, dealership frames and other graphics as plates. The investigators found no evidence that Flock’s own software used facial recognition. They also reported more than 27,000 “no space left on device” errors, alongside crashes and reboots.
The findings follow security researcher Jon “GainSec” Gaines’s 2025 research documenting flaws that could provide root access after physical access to a camera.