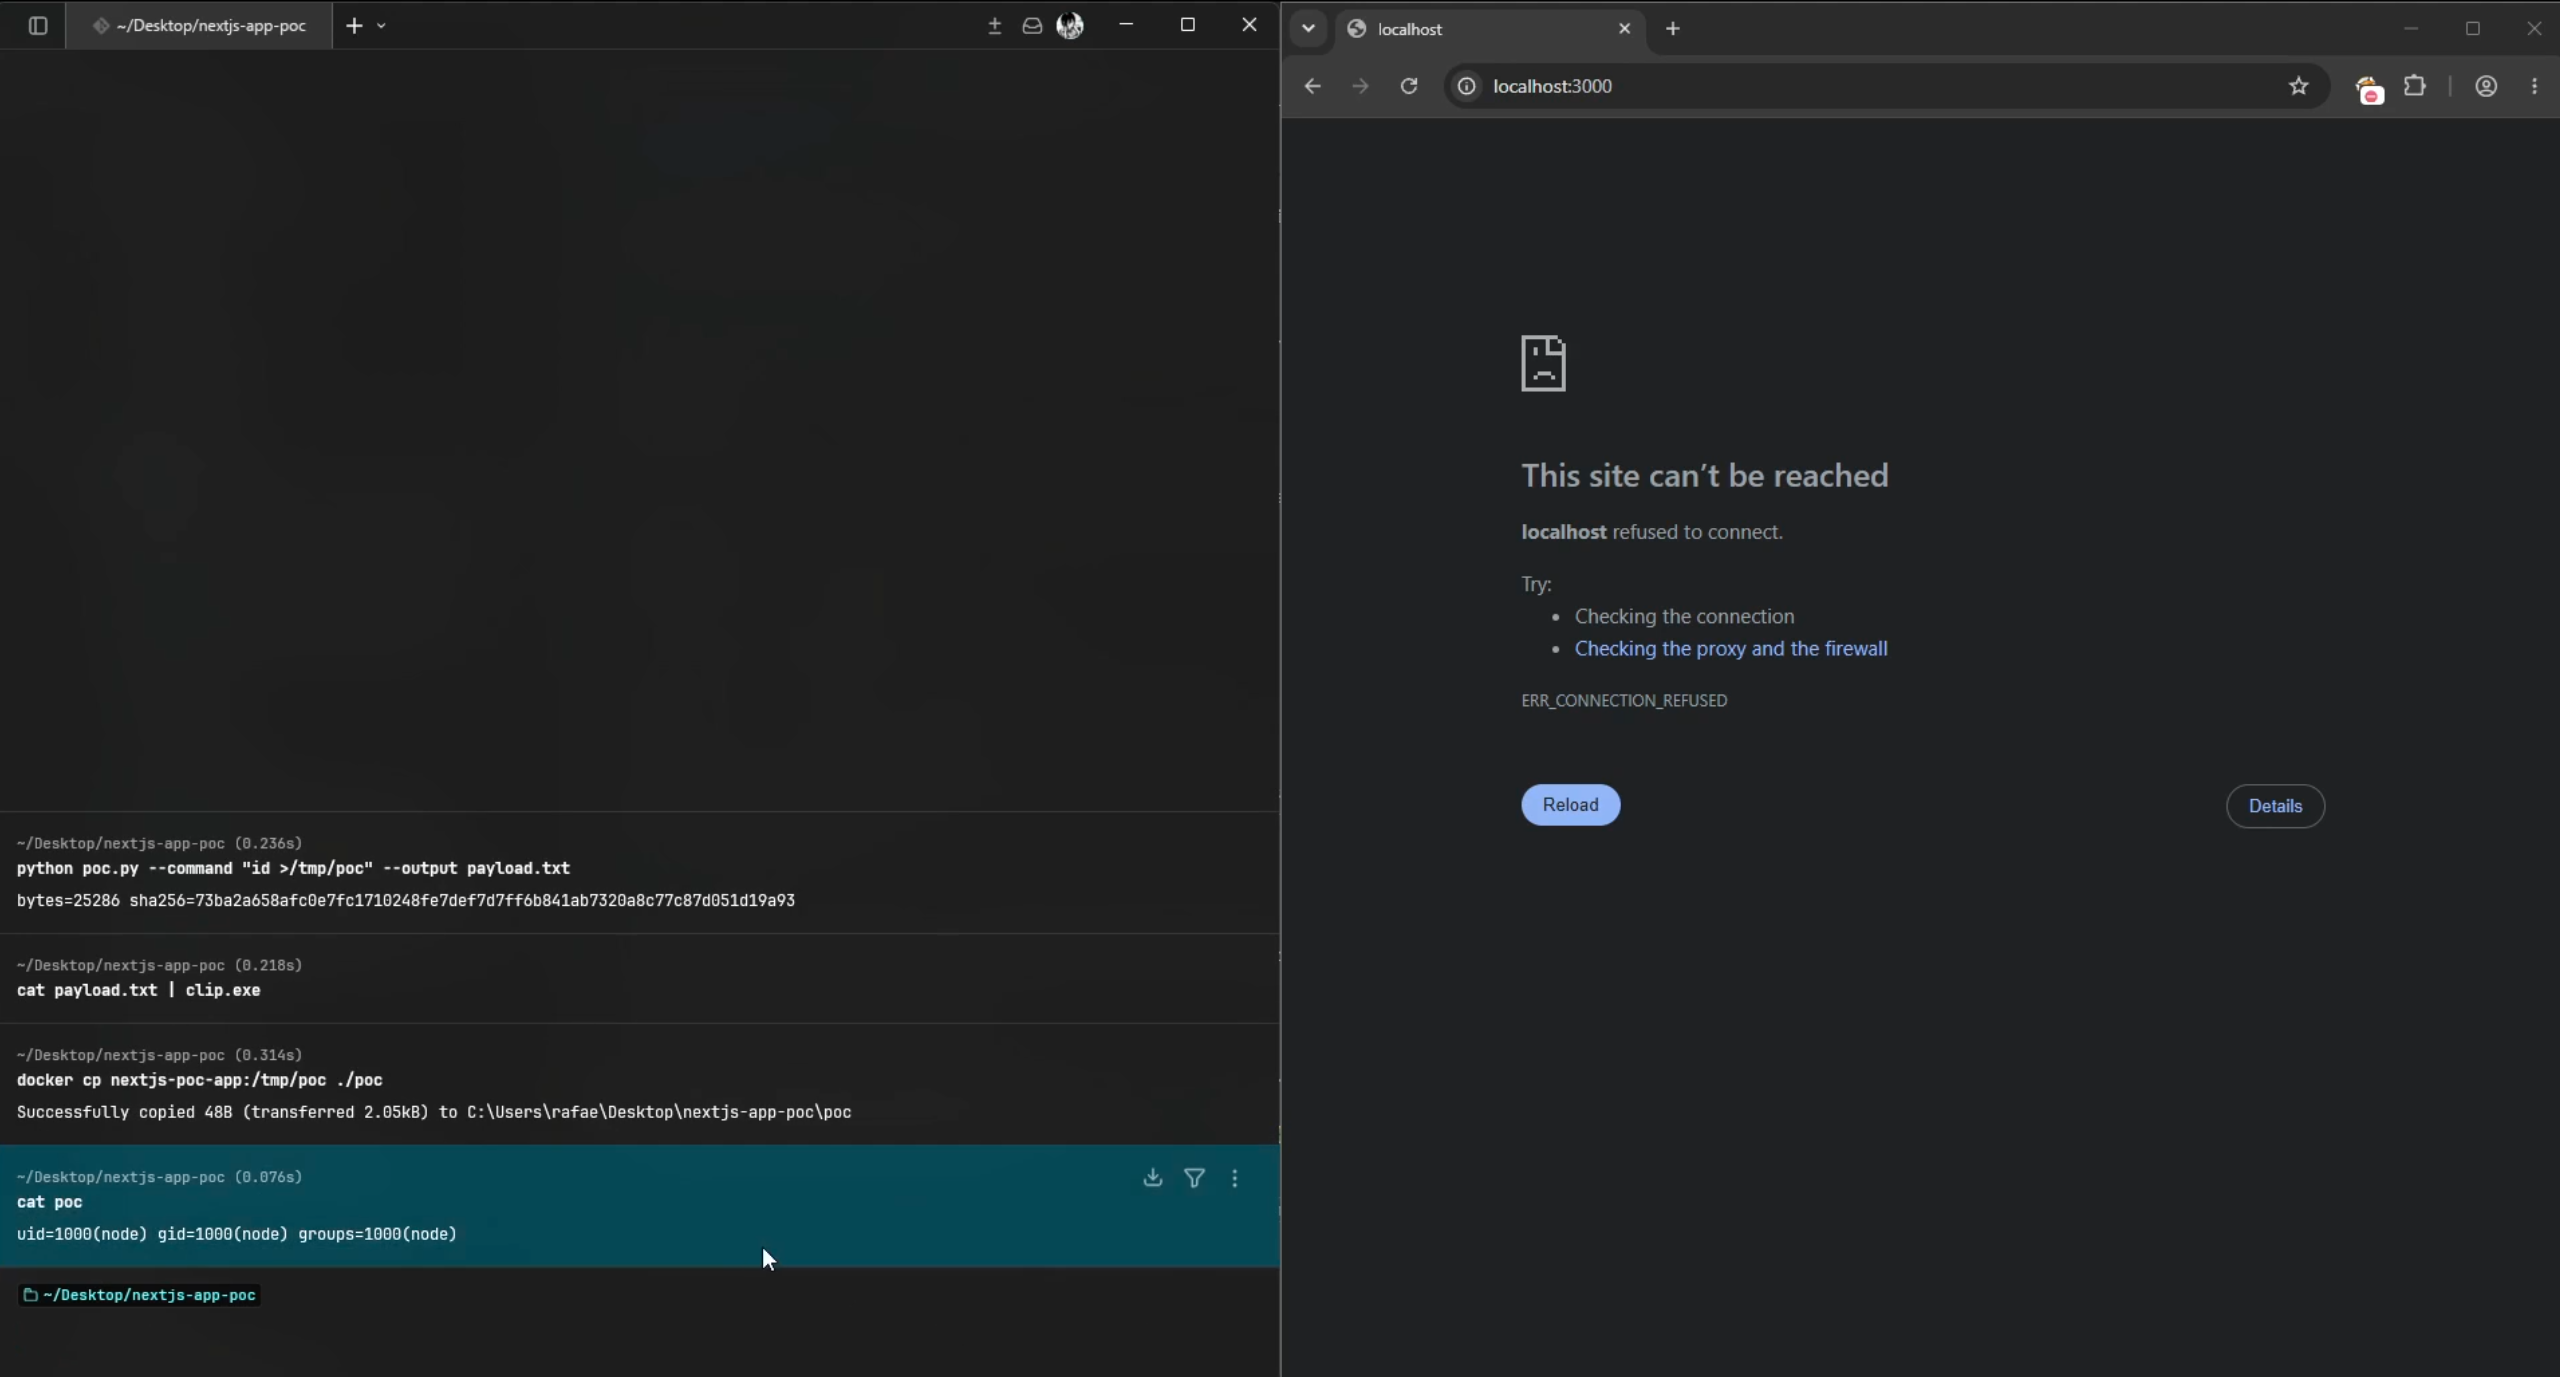
ON 22 September 2026, Vercel issued an emergency fix for a critical Next.js remote-code-execution vulnerability, tracked as CVE-2026-94545. The flaw has a CVSS base score of 9.5 and affects Next.js versions 16.2.0 through 16.3.5. It is located in the Node.js implementation of `next/og`, which generates Open Graph images, where improper escaping in SVG output produced by Satori can allow unauthenticated attackers to execute arbitrary code on Node.js runtimes. Applications using the Edge runtime are not affected, and the article says 15.x releases do not contain the remote-execution flaw.
The issue can arise when applications insert untrusted input, such as query-parameter values, into dynamic SVG social cards. Crafted input may escape SVG filtering and cause downstream parsers to process malicious markup within the server runtime. The reported impact includes potential compromise of host servers and theft of application data, although the article says there was no confirmed exploitation in the wild and no public proof-of-concept code had been released.
Developers should upgrade to Next.js 16.3.6 and consult Vercel’s security guidance. Where immediate updating is not possible, the stated workaround is to avoid passing untrusted parameters into SVG content or style properties rendered by the Node.js `ImageResponse` module. Next.js 15.5.26 includes related defence-in-depth hardening.