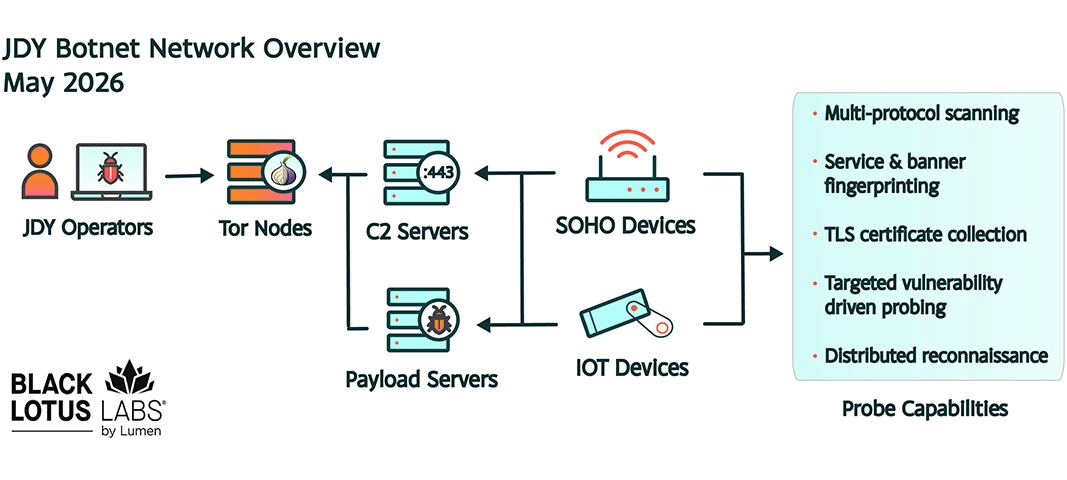
THE JDY botnet, a reconnaissance network linked to Chinese state-sponsored hackers, has re-emerged, expanding from 650 to over 1,500 compromised devices since early 2024. Primarily targeting military-related networks, the botnet conducts rapid scans for new vulnerabilities, leveraging a diverse array of compromised devices, including Cisco and Ubiquiti hardware, to enhance its stealth.
The malware, designed for MIPS-based routers and embedded systems, executes targeted scans and communicates via hidden Tor services. Given its capability to exploit vulnerabilities shortly after disclosure, the botnet presents a significant threat, emphasizing the need for quick patching and updates on edge devices to mitigate risks.