CLOUDFLARE has announced plans to operate a free, publicly trusted Certificate Authority (CA) and issue certificates for websites without charge, positioning itself as a major alternative to Let’s Encrypt. The company has begun submitting to the root programmes of Chrome, Apple, Microsoft, and Mozilla, a necessary step for any public CA to be trusted by browsers and devices.
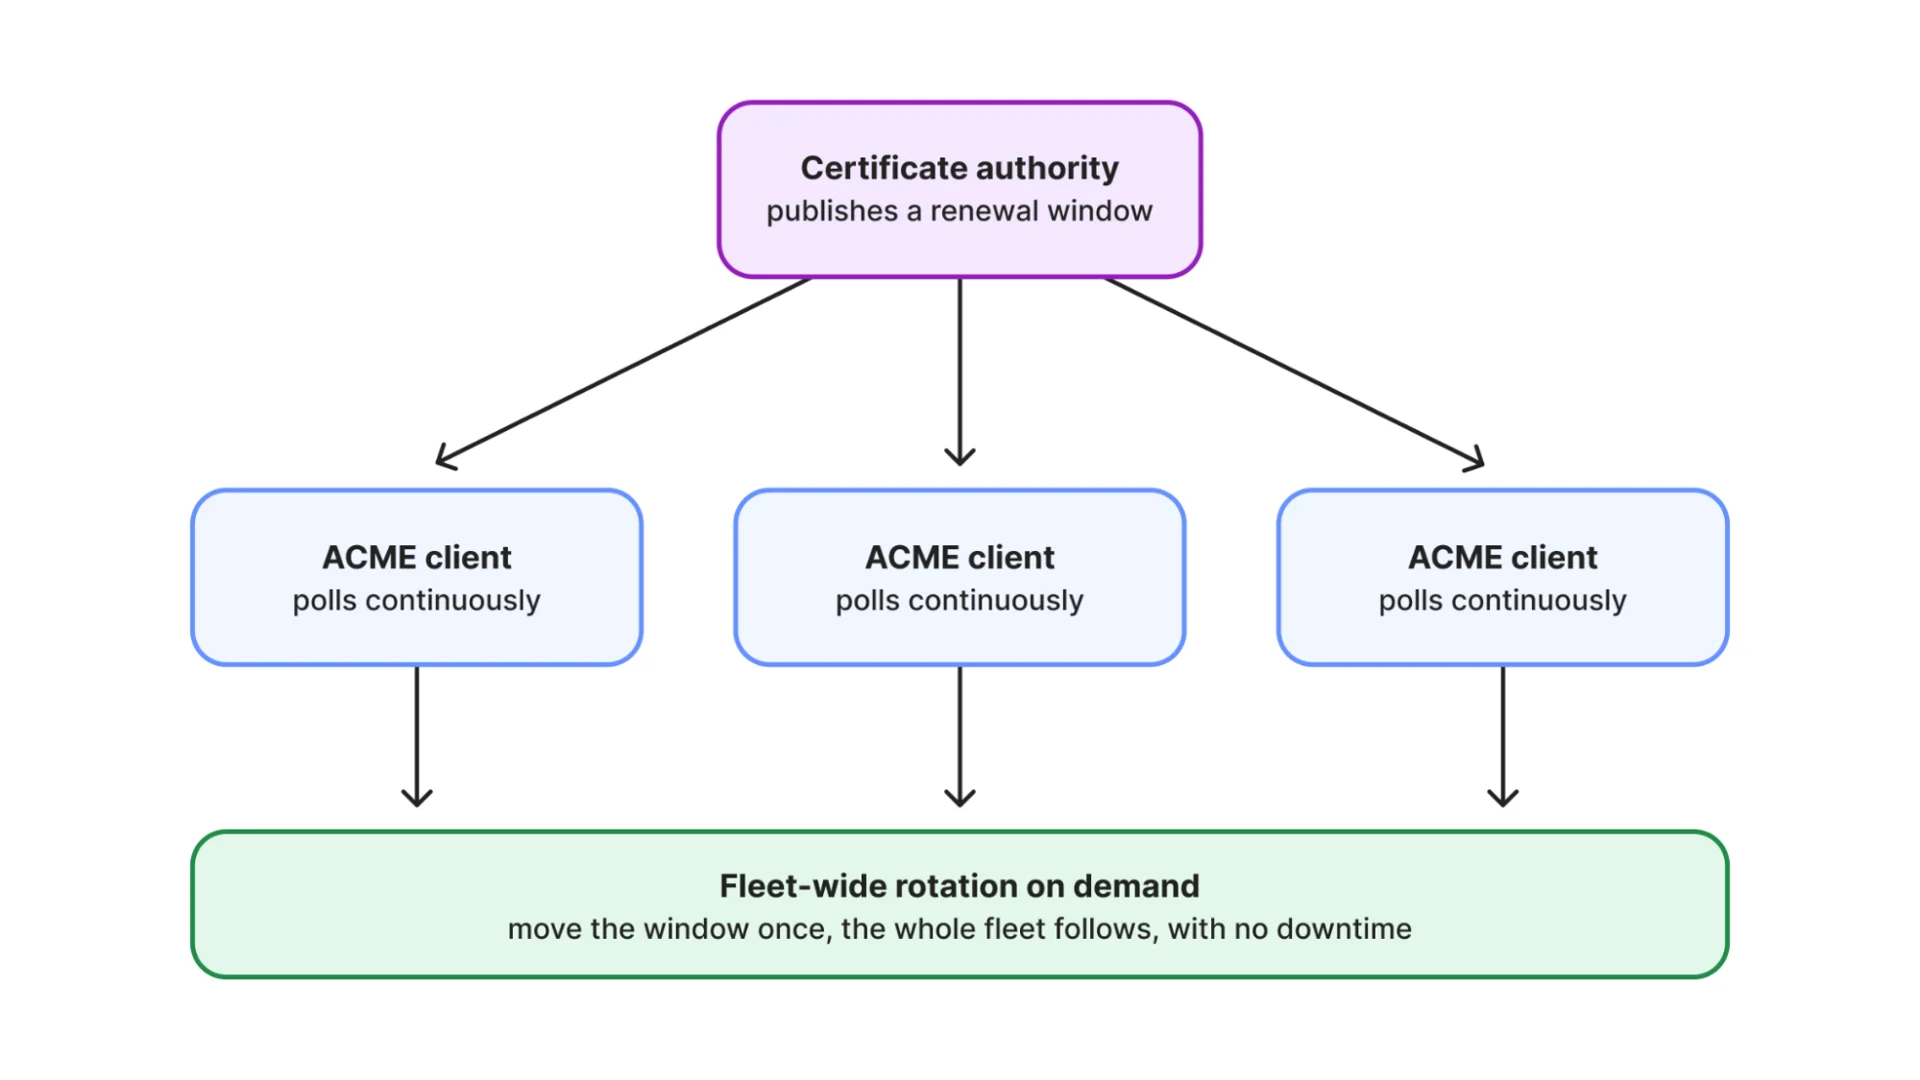
Cloudflare emphasises automation and intends to base its issuance and renewal processes on the ACME protocol, with the aim of making renewal mandatory and seamless for administrators who support ACME Renewal Information (RFC 9773). The move follows a context of shrinking TLS certificate lifespans and a broader industry shift toward automated certificate management to mitigate risks from delayed renewals.
In parallel, Cloudflare has reached a definitive agreement to acquire an established GlobalSign root certificate to broaden coverage for older devices while it develops new roots for contemporary trust programmes. The project also introduces a Merkle Tree Certificates (MTC) approach, slated to begin in early 2027, which signs the top of a Merkle tree and provides compact proofs to browsers, reducing data overhead during the post-quantum transition.
Cloudflare notes it will run both classical certificates and MTCs in parallel and plans to publish reproducible builds, verify hardware security module integrity, and provide an issue dashboard. The company highlights that Chrome has signalled Merkle Tree Certificates as a path for quantum-resistant HTTPS, while emphasising that a mass rollout of traditional public certificates remains contingent on future developments.