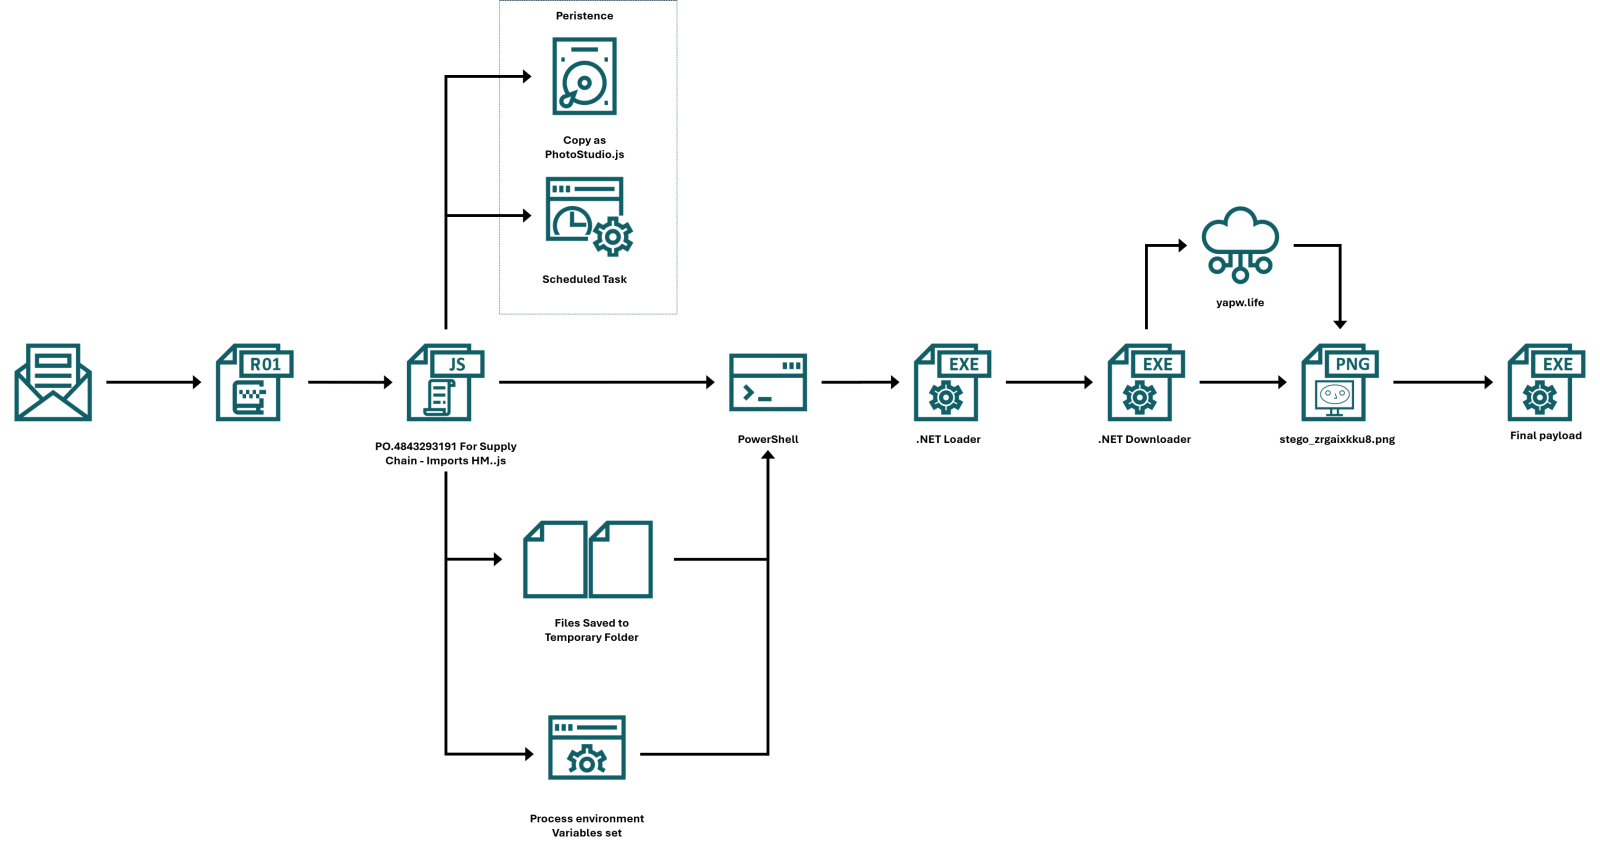
A malspam email intercepted in late August attempted to impersonate an employee of a legitimate company and lure the recipient into reviewing attached requirements and providing a quotation for a fibre-optic system. The quarantined archive used an `.r01` extension and contained a 613 KB JavaScript file named `PO.4843293191 For Supply Chain - Imports HM..js`. The file had a 28/55 detection rate on VirusTotal when analysed and was identified as part of the LausivLoader malware family. Failed SPF and DMARC checks also reduced the likelihood that the message would reach its intended recipient.
The script uses 450 junk comment lines and obfuscated string construction to hide its behaviour. It copies itself to `%LOCALAPPDATA%\Microsoft\PhotoEngine\PhotoStudio.js` and attempts to create a hidden logon task named `\MicrosoftEdgeUpdateTaskCore`. It also creates two temporary files, stores their paths in process environment variables, and launches hidden PowerShell through headless `conhost.exe`; the child processes inherit those variables, allowing the stages to exchange data.
PowerShell combines and deletes the files, then uses AES-128-CBC decryption and GZip decompression to recover a 315,904-byte .NET loader, which is executed directly in memory.
That loader attempts to interfere with AMSI before unpacking a 59,904-byte .NET downloader. The downloader was configured to retrieve a PNG from `hxxps://yapw[.]life/phpt/stego_zrgaixkku8.png`, extract an encrypted payload from an `iTXt` metadata chunk, and decompress it. The URL was no longer live during analysis, so the final payload and whether it would have used reflective loading or process hollowing could not be confirmed.