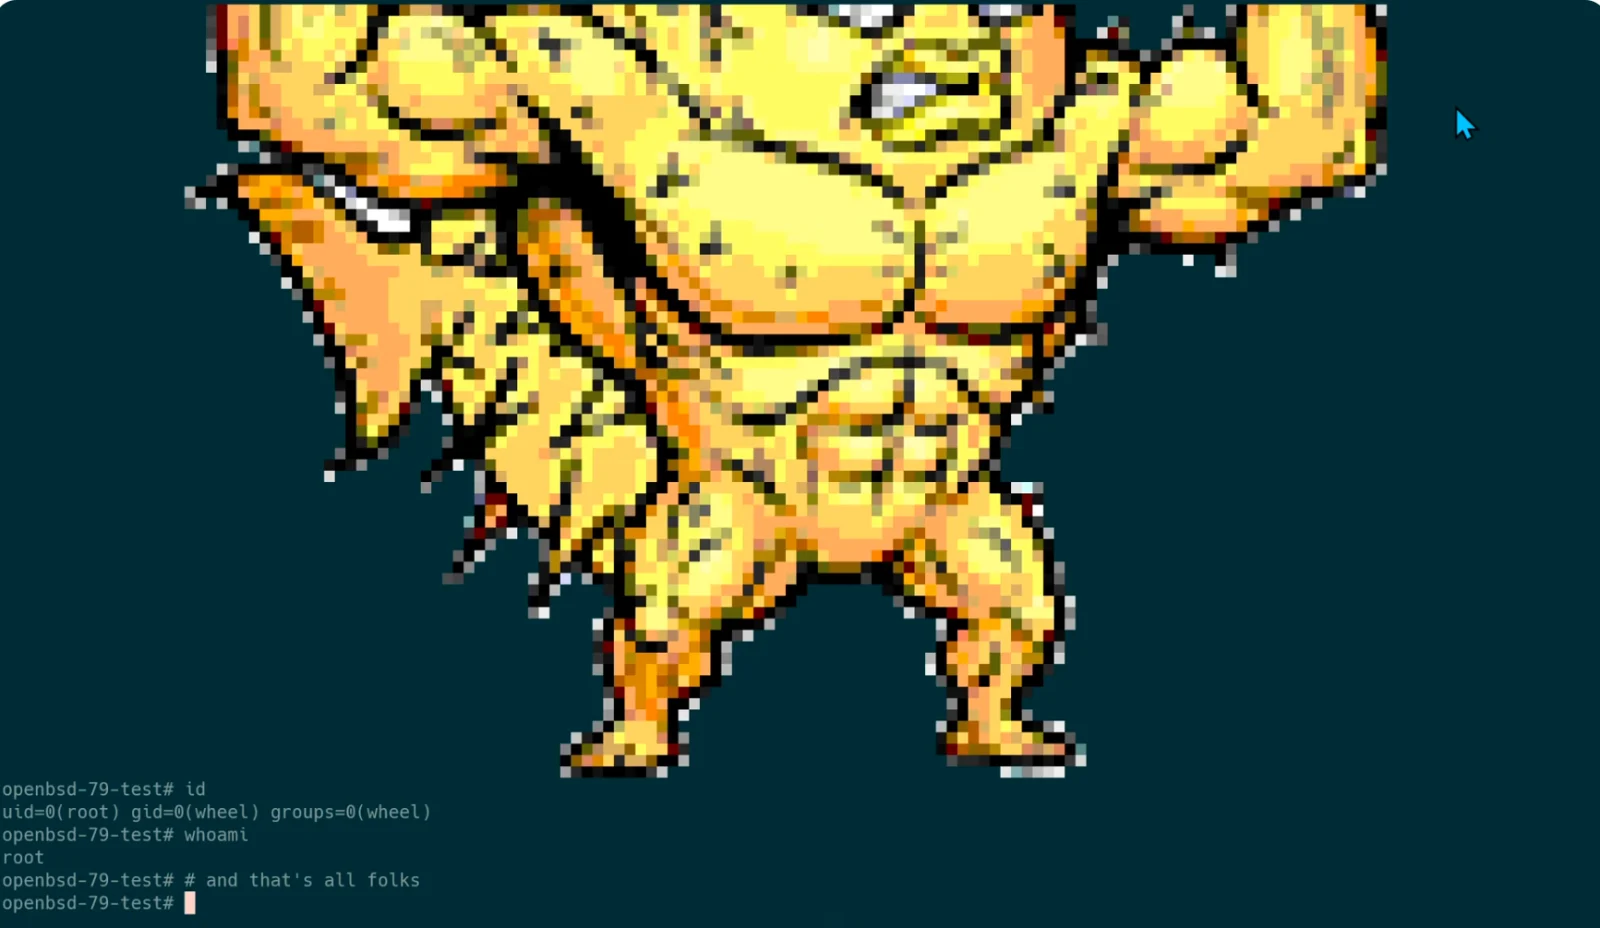
IN a public disclosure on 16 October 2026, researcher Calif released full technical detail and working proof-of-concept (PoC) code for a local privilege escalation chain dubbed “Big Fish” affecting the OpenBSD kernel. The chain enables a local user to gain root privileges on OpenBSD 7.9 even when security features such as KARL, SMAP and SMEP are enabled. OpenBSD has issued errata patches to fix the flaws.
OpenBSD versions and exposure: The flaws affect OpenBSD 7.9 systems that have not applied the latest errata. The Hacker News notes that one of the fixes also appeared for OpenBSD 7.8. There is a public PoC and accompanying exploit code on GitHub, with the author indicating that the details allow study or reuse against unpatched systems. No CVE identifiers have been assigned to this chain at the time of reporting.
How the attack works and evidence: The exploit chain combines two bugs. First, a 16-bit shared memory counter can overflow and wrap to a negative value, enabling a use-after-free via a race condition. Second, an out-of-bounds write in the kernel completes the escalation. Although KARL relinks the kernel to randomise addresses, the kernel’s memory allocators remain deterministic, aiding exploitation. There has been no reported exploitation in the wild to date, and no CVEs have been published. Evidence rests on Calif’s write-up and the public PoC on GitHub.
Mitigation and response: Administrators should apply OpenBSD 7.9 errata 018 and 026 via syspatch, then reboot to load the updated kernel, and restrict local shell access on shared hosts. Calif also proposes deeper fixes, including safer unlinking checks, a randomized page table map, and a less predictable kernel allocator.