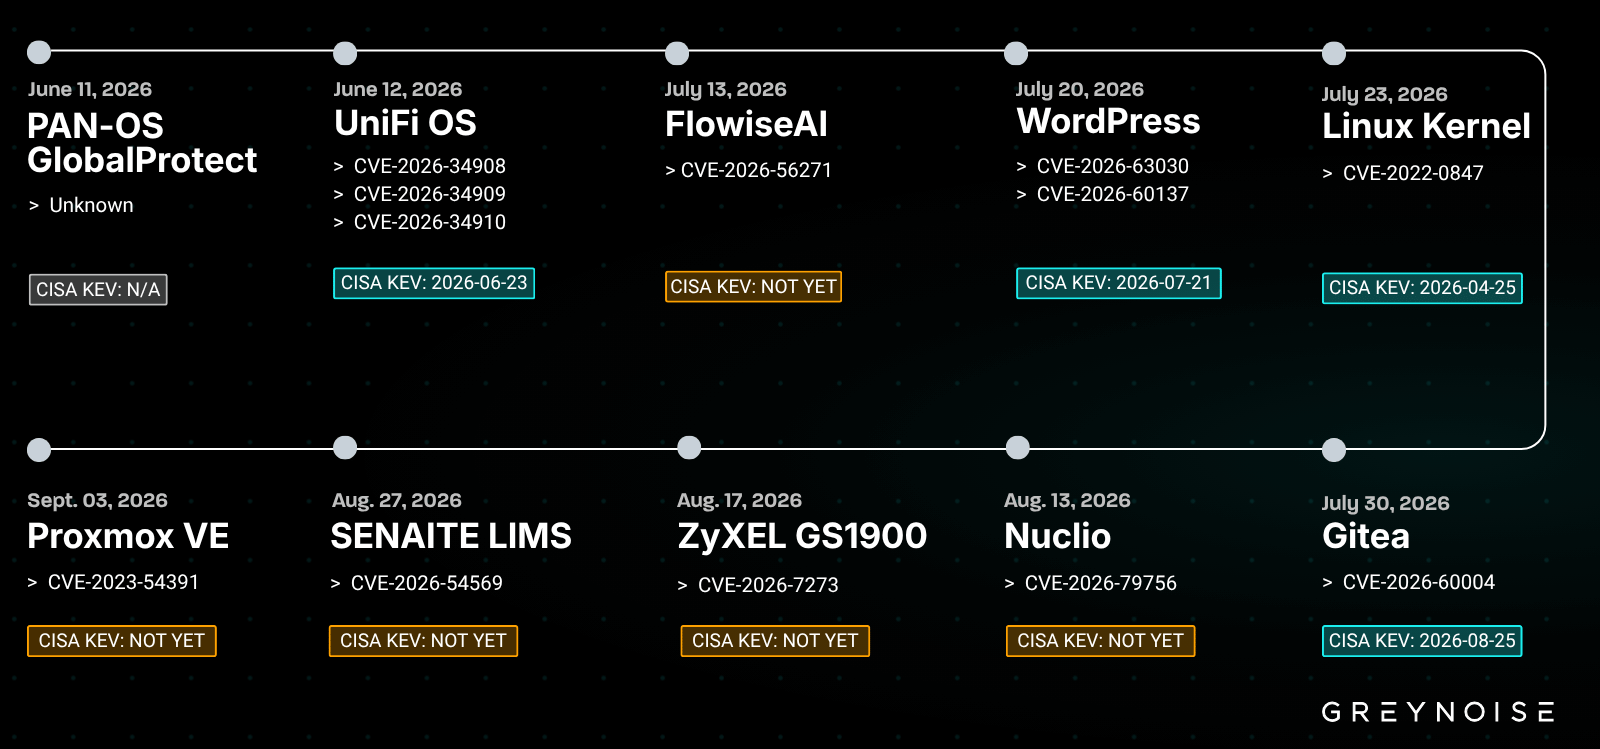
GREYNOISE and Acronis researchers have linked a suspected Chinese-speaking actor to a campaign exploiting WordPress sites and other internet-facing systems. On 22 July 2026, the actor reportedly used a two-stage chain involving CVE-2026-63030 and CVE-2026-60137 against a Western government web portal, then deployed a custom web shell disguised as a “kapibala” plugin.
The attackers extracted the core user table, exposed 13 administrator accounts, created a backdated account, searched for credentials and used recovered database passwords to access internal systems. They ultimately stole 18,566 records, including plaintext credentials and personal information relating to government and law-enforcement personnel.
The reported campaign affected at least 49 organisations across 29 countries, including government and commercial entities. GreyNoise also observed attacks against ZyXEL GS1900 switches using a reported zero-day, CVE-2026-7273, with 996 switches compromised across 48 countries; 564 still used factory-default credentials.
Researchers said the actor tested 17 script variants to evade Microsoft Antimalware Scan Interface detections and found evidence suggesting large-language-model assistance in tool development, including Chinese comments in the code. The group is assessed with moderate confidence as Chinese-nexus and may be linked to the “Red Heron” activity based on shared infrastructure and techniques.
Recommended responses include patching exposed systems, auditing for backdated accounts and rogue plugins, checking for bulk database exports, updating switch firmware, removing default passwords and isolating management interfaces from public networks.